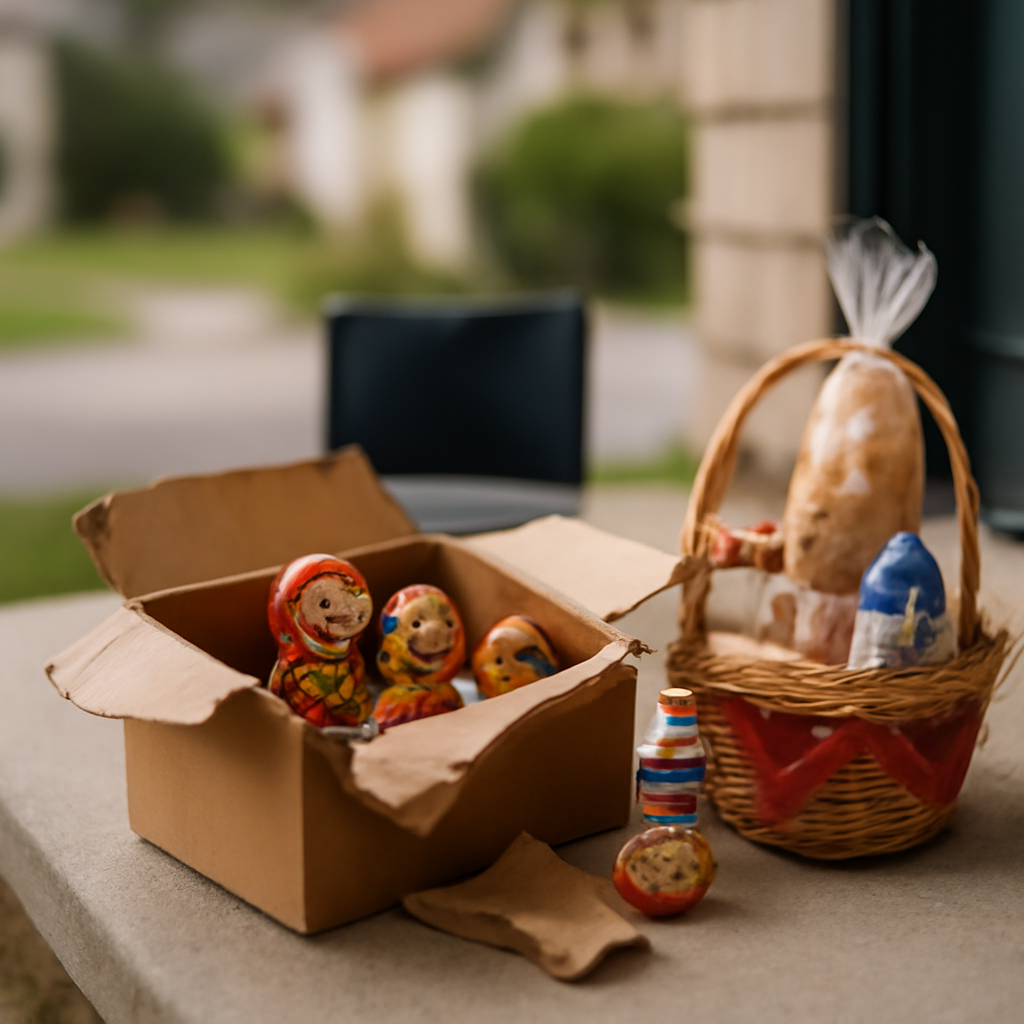
"We-know-where-you-are kind of stuff." — Tim Beasley
Tim Beasley’s experience: a package on the doorstep
While investigating a cyberattack tied to Russia’s Midnight Blizzard, Tim Beasley — then lead investigator for Microsoft’s Detection and Response Team and now a senior incident response consultant at Semperis — found a delivery on his doorstep: nesting dolls and regional souvenirs. He told The Register he assumed the package was from the group, which has been linked to the Kremlin’s Foreign Intelligence Service (SVR). “Just little souvenirs and gift basket stuff from that area of the world,” Beasley said. “It’s a real eye-opener when you get that type of thing.”
Semperis’ ransomware risk report: the hard numbers
Semperis’ annual ransomware risk report surveyed 1,200 post-ransomware organizations across the first half of the year and documents a striking shift: psychological and physical intimidation are now common tools of extortion. The study found that 37 percent of ransomware incidents involved psychological or physical threats directed at staff. Breaking that down, attackers used psychological intimidation in 23 percent of cases and physical threats in 17 percent.
- 25 percent of victims experienced doxxing (names, home/work addresses, phone numbers posted online).
- 25 percent of ransomed personnel sought psychological and/or medical treatment after incidents.
- 24 percent of victims hired personal security teams.
- 23 percent experienced swatting calls — false emergency reports intended to trigger armed responses.
- 53 percent of respondents reported attackers carried through on threats in the past year.
- 69 percent of surveyed ransomware victims were targeted multiple times within the past 12 months; 31 percent made multiple payments.

The cyber insurance questionnaire just landed. Now what?
SOC 2, HIPAA, insurance renewals - someone has to own security strategy. Nubivance provides fractional CISO leadership without the full-time salary.
Get a security leadThe Com, Europol, and “violence as a service”
Law enforcement and investigators are flagging evidence that these campaigns are not isolated. Over the summer, Europol and partner investigators identified 4,340 “horrific” URLs for removal as part of a crackdown on The Com — described as a loosely knit network of online groups whose young members participate in hacking, swatting, digital extortion, real-life shootings, and other physical violence. “We’ve seen violence as a service get used,” Beasley said, tying the online marketplaces and social networks of criminal groups to real-world harm.
Named operators and the escalation to real-world targeting
Beasley pointed to several groups he’s observed using psychological and physical threats to force payments. “I've seen Scattered Spider, I've seen ShinyHunters, I've seen Lapsus$,” he told The Register. In an exclusive interview with The Register, ShinyHunters claimed they “don't attack human beings,” but conceded that “there are times in the work we do sometimes we have to push the corporate to the absolute limit to get them on the table.”
Specific tactics reported in the Semperis survey and Beasley’s investigations include sending executives images of their children’s schools, doxxing family contact data, threatening texts/letters/packages (reported by 57 percent of affected employees), threats against family or friends (37 percent), and direct physical intimidation: physical intrusion (19 percent), abduction (17 percent), bodily harm (13 percent), and stalking (6 percent).
Law enforcement, executives and security teams: the recommended response
Beasley’s practical imperative is blunt: “stand your ground.” He urged organizations and individuals to involve authorities early. “If you feel like you're under duress, then by all means get law enforcement involved. Don't be afraid to call the cops. Don't be afraid to get the FBI involved, sooner rather than later. And don’t pay them.” He emphasized the danger of payment as a recurring liability: once a victim pays, attackers are likely to return — a pattern reflected in the report’s finding that 31 percent of victims made multiple payments.
A closing observation
The record assembled by Semperis and the incidents described by Beasley show a chilling evolution: ransomware is no longer purely a digital financial crime but an operation that routinely weaponizes fear and the prospect of physical harm. With 53 percent of victims reporting that attackers carried through on threats and with organized online communities like The Com amplifying real-world violence, the choices for victims are stark and consequential. Organizations and law enforcement are being pushed to respond not only as digital defenders, but as protectors of people — employees and their families — whose lives are now explicitly part of the extortion calculus. How law enforcement and companies scale protections for those families, and whether that will deter groups that advertise violence as a service, remains an urgent question.