"France condemns in the strongest possible terms the unacceptable cyberattacks carried out on its territory by the Islamic Republic of Iran against its interests," reads the statement from France's Ministry for Europe and Foreign Affairs.
Attribution: France pins the October supermarket campaign on Shahid Kaveh
French authorities say the October 11–12 cyberattacks that disrupted refrigeration systems at retail sites were carried out by Shahid Kaveh, a cyber‑offensive unit affiliated with the electronic and cyber center of Iran's Islamic Revolutionary Guard Corps (IRGC). The attribution was issued by France's Cyber Crisis Coordination Center (C4), which includes the national cybersecurity agency ANSSI, military cyber command, and intelligence agencies, and was summarized in a technical report from CERT‑FR.
Tactics observed: refrigeration controllers and propaganda amplification
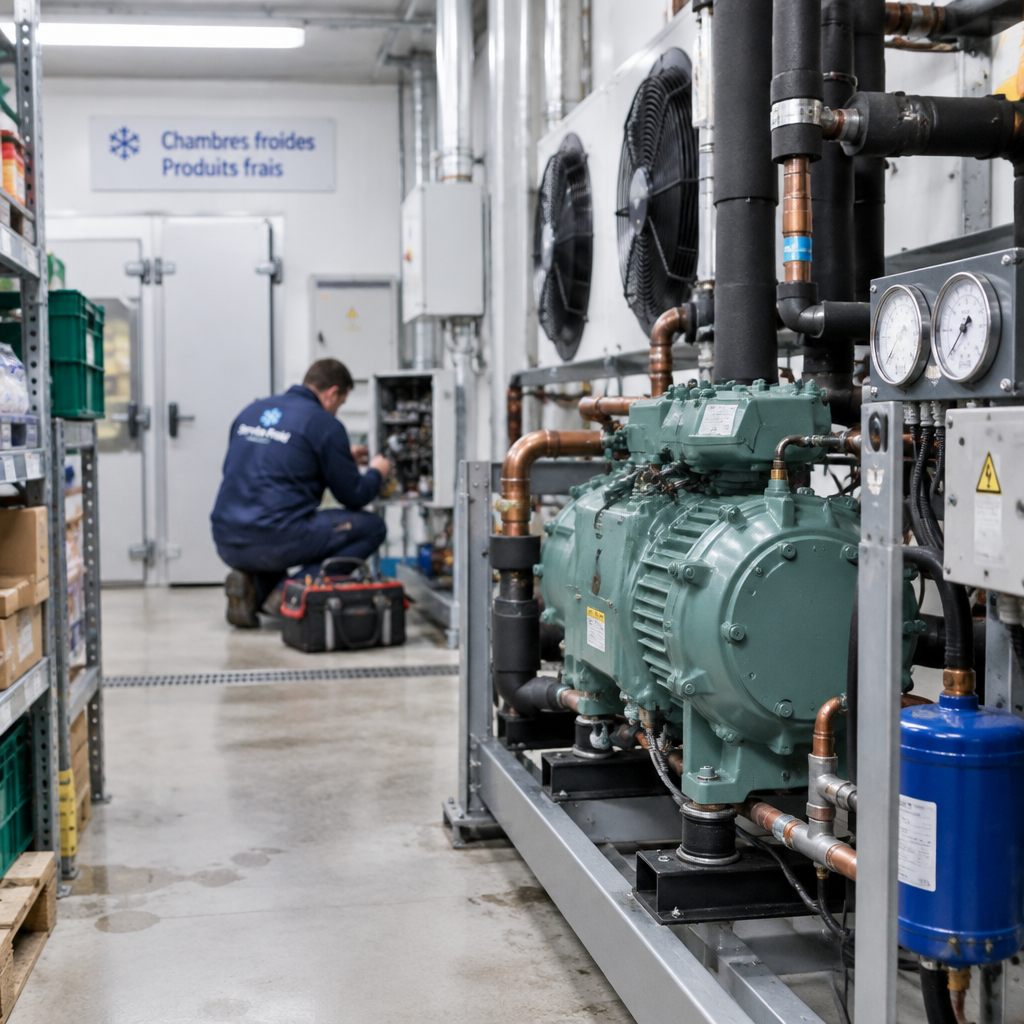
Investigators found that attackers compromised industrial refrigeration controllers and remotely changed defrost settings to high temperatures, a manipulative change intended to defeat cold‑chain preservation. CERT‑FR noted that the campaign was relayed on the propaganda outlet CyberbanNews — which France links to Shahid Kaveh — as early as October 13, 2026. The French report also identified traces of Farsi within the attack infrastructure and the use of the FOFA internet‑connected device search platform, which CERT‑FR says the group commonly uses.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleImpact on stores, food supplies and fires
Initial public reporting cited 250 to 350 affected supermarkets; French authorities have since reported that approximately 700 retail locations were targeted in the October incidents. The attacks forced stores to discard fresh and frozen products, caused tens of millions of euros in food losses, and sparked at least 15 fires. CERT‑FR's technical report lists major retail brands and food facilities affected, including Casino, Leclerc, Coopérative U, Metro, Carrefour, Intermarché, smaller butcher shops, a slaughterhouse, and cooperative food‑processing facilities.
Associated operations: Schneider Electric reconnaissance and hydroelectric sites
French investigators linked related reconnaissance and intrusion activity against Schneider Electric industrial control systems to the same campaign. In April 2026, the Shahid Kaveh unit was observed conducting large‑scale reconnaissance of Schneider Electric systems, including systems located in France, and CERT‑FR says the attacker infrastructure used against refrigeration controllers was also used to conduct reconnaissance against Schneider systems using techniques previously associated with the Iranian unit. During the October timeframe, investigators detected attacks against Schneider Electric equipment at small hydroelectric installations; those incidents reportedly produced only moderate effects on targeted equipment.
Spread beyond October: later waves, blood storage, and international warnings
France's report is explicit that its attribution applies to the October attacks against French supermarkets; it does not attribute later incidents. A second wave of refrigeration‑system attacks reported in November affected more than 115 stores across six European countries. France's national blood service also reported a similar incident that altered temperature and defrost settings at three facilities used to store blood products. Separately, the FBI and CISA issued a warning — cited by French authorities — about ongoing cyberattacks targeting industrial refrigeration and cold‑chain monitoring systems worldwide.
What this means for technologists, policymakers, and retailers
- Technologists and security teams: CERT‑FR highlights concrete forensic indicators — reuse of attacker infrastructure, FOFA platform queries, Farsi artifacts, and public bragging on CyberbanNews — that can be searched for in incident response. The link to Schneider Electric reconnaissance suggests defenders should review exposure of industrial controllers and remote access points used for refrigeration and small utility controls.
- Policymakers and regulators: France says it will summon Iran's ambassador to condemn the attacks and propose new European Union sanctions against Iranian individuals and organizations involved in malicious cyber operations. That is the stated diplomatic and policy response France is pursuing.
- Retailers and cold‑chain operators: The campaign demonstrates a risk vector through industrial refrigeration controllers. Retailers named in CERT‑FR's report faced both product loss and physical harm — including a minimum of 15 fires — and should expect scrutiny of operational technology protections and supply‑chain resilience.
France's public case combines technical indicators, observed operational messaging on CyberbanNews, and historical activity tied to Shahid Kaveh — including a claimed sabotage campaign in March and April 2026 that targeted Israeli and U.S. interests and included attacks on Israeli refrigeration equipment and other industrial control systems. The nation has framed those findings as sufficient to attribute the October refrigeration attacks on French territory to the IRGC‑affiliated unit and to seek both diplomatic rebuke and expanded sanctions at the EU level.
The events raise immediate questions about exposure of cold‑chain infrastructure and the interplay between reconnaissance activity and destructive operations against industrial controllers. France's action — attribution, diplomatic summon, and a push for EU sanctions — establishes a clear line from forensic finding to policy response; whether that will change operational behavior or reduce similar incidents remains to be seen.
Read the original report: France blames Iranian hackers for supermarket attacks that sparked fires — BleepingComputer