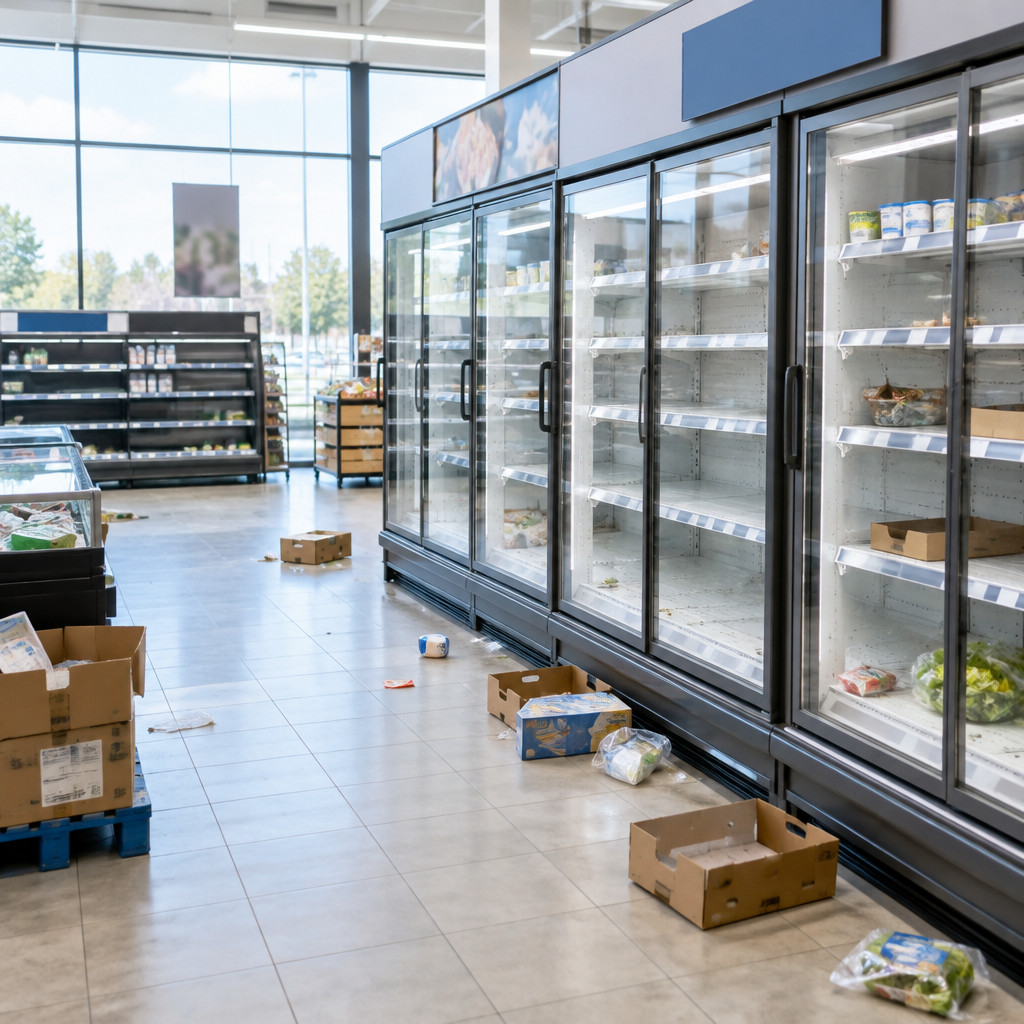
“The unidentified threat actors gained unauthorized access to refrigeration controllers and set them to defrost mode, resulting in hundreds of supermarkets across the region having to throw away spoiled food.”
Scope and timeline of the attacks
Unit 42’s reporting ties the first wave of malicious activity to the night of Oct. 11–12, 2026, when roughly 700 supermarkets in France were targeted. A second wave struck overnight between Nov. 1–2, 2026, spreading across at least 10 additional European countries and impacting over 100–115 retail locations. The timing — as retailers were building inventory for the holiday season — amplified the operational and economic disruption for stores and consumers.
How the attacks behaved and immediate consequences
According to multiple sources cited by Unit 42, the attackers manipulated refrigeration controllers to enter defrost mode and raised temperatures as high as 50°C (122°F). In some instances this activity culminated in fires. French authorities also disclosed that refrigeration systems used by medical facilities were affected; at this time there is no evidence that blood products were spoiled as a result. Retailers were forced to dispose of spoiled food at scale.

Nobody's watching your logs at 2 AM.
Full SOC coverage without building one. Nubivance deploys and manages Rapid7 InsightIDR and MDR for organizations that need detection and response, not another dashboard.
Get coverageDevice exposure measurements and trends from Cortex Xpanse
Between Nov. 5–6, 2026, Unit 42 identified over 5,000 internet-exposed devices that were manufactured by companies listed in a recent CERT-FR advisory. Unit 42 cautions that these counts do not necessarily mean the devices were running exploitable software versions. Focusing on devices in France, Unit 42 tracked a decline in internet-exposed devices across three intervals: 1,853 devices between Oct. 1–15; 558 devices between Oct. 16–31; and 316 devices between Nov. 1–6. Censys has also reported on device-exposure trends in Europe.
Claims of responsibility and government advisories
On Nov. 3, 2026, the pro‑Russian hacktivist groups NoName057(16) and Z‑Pentest claimed responsibility via Telegram posts; those allegations remain unverified. The Cybersecurity and Infrastructure Security Agency (CISA) issued an advisory on Nov. 5, 2026 warning of potential exploitation vectors including authentication bypass, arbitrary code injection, and weak configurations.
What this means for technologists, policymakers, and retailers
- Technologists and security teams: the incident highlights internet-exposed controllers as a measurable exposure; Unit 42 recommends tools such as Cortex Xpanse and Device Security to identify exposed devices, assess weak configurations and default credentials, and monitor anomalous control-plane traffic.
- Policymakers and regulators: public advisories from CISA and CERT‑FR, and disclosures by French authorities about medical refrigeration impacts, provide the formal signals regulators can use to prioritize guidance on device hardening, supplier practices, and incident reporting.
- Retailers and healthcare facility operators: the attacks demonstrate that compromised controllers can cause large-scale inventory loss and physical risk — including fires — and that mitigation may require both visibility into exposed devices and network-layer protections such as virtual patching and inline threat prevention.
Mitigation options Unit 42 lays out
Unit 42 outlines several detection and protection capabilities for organizations with exposed OT and IoT controllers. Cortex Xpanse can discover internet-facing devices and escalate findings; Device Security offers continuous discovery, risk assessment and protocol‑level visibility to identify weak configurations and default credentials; and Frontier Virtual Patching with Advanced Threat Prevention inspects inline network traffic to block exploit attempts, command‑and‑control communication, and arbitrary code injection in real time. Unit 42 also promotes Continuous Frontier AI Defense for proactive exposure discovery and testing, Threat Intel Services including deep and dark web monitoring, and incident response engagement to investigate compromises or provide proactive assessments.
Important caveats in the reporting: the initial access vector for the attacks remains unconfirmed, and public device-count statistics do not prove that exposed devices were running vulnerable firmware or software that was actually exploited.
The immediate record is concrete about impact — widespread spoilage, some fires, affected medical refrigeration with no confirmed loss of blood products — and about mitigations advised by cybersecurity teams and agencies. The outstanding factual hinge remains how the attackers first gained control of the controllers; resolving that will determine whether remedies must focus more on vendor firmware, default credentials, supply-chain practices, or network segmentation.