"Access and control are separate findings, and the public evidence on VL Prosperity stops before engine control," said Jacob Krell, Senior Director: Secure AI Solutions & Cybersecurity at Suzu Labs.
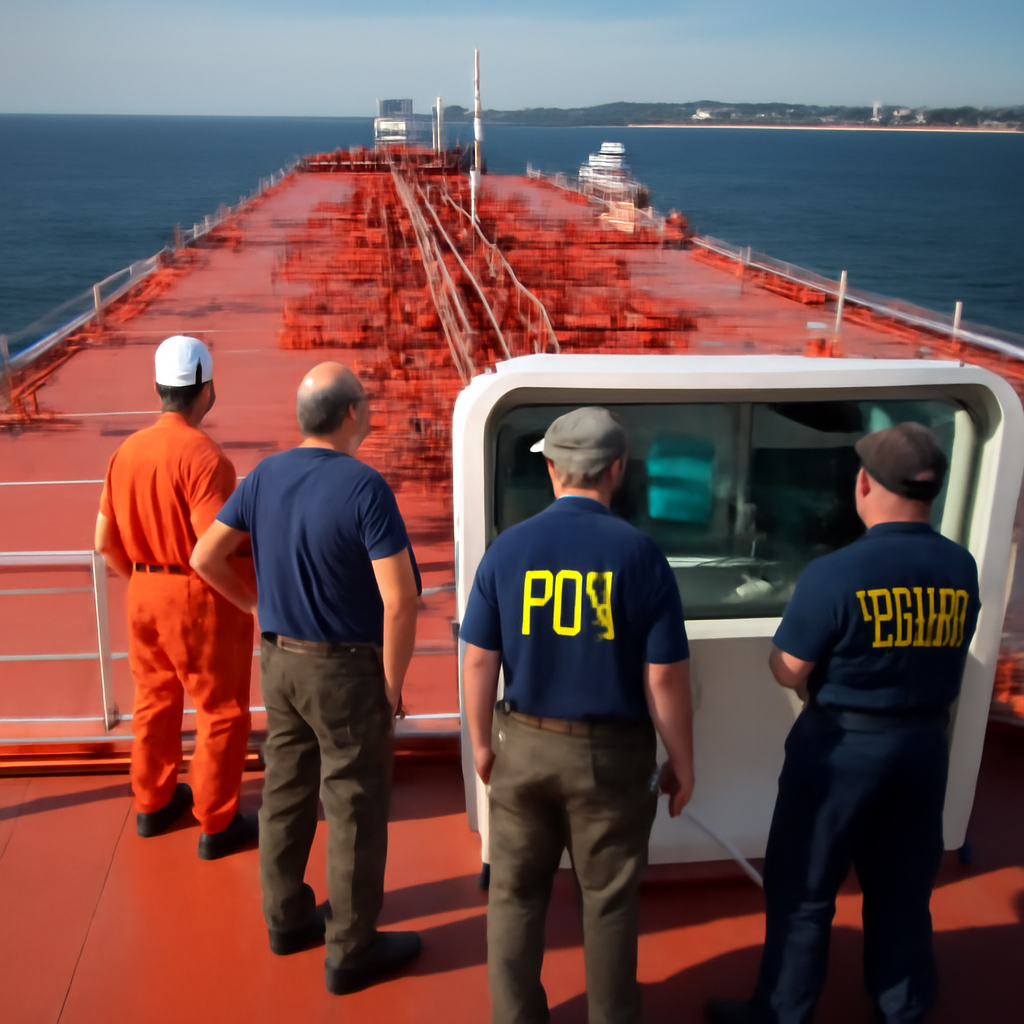
FBI and U.S. Coast Guard boarding of VL Prosperity
While approaching the coast of Texas, an oil supertanker — identified in public reporting as the VL Prosperity — was the subject of a cyber intrusion that prompted a joint response by the Federal Bureau of Investigation and the U.S. Coast Guard. The agencies boarded the vessel to examine its information technology (IT) and operational technology (OT) systems after indications that its networks were compromised, the joint statement says.
Bloomberg reported investigators found temporary access to the tanker’s digital propulsion system. The joint public statement from the FBI and U.S. Coast Guard makes a point of reporting no operational disruption, vessel instability, physical danger to the crew, or environmental impact. At this time the breach is still under investigation and it is unknown who conducted it.
Jacob Krell: distinguishing access from control
Krell framed the core forensic question plainly: investigators must show whether an intruder reached a write-capable propulsion controller and issued a valid command that the controller accepted. He warned that “this would be the first publicly documented, independently confirmed cyberattack against a commercial vessel’s propulsion controls,” but stressed the current public record “stops before engine control.”
He and the public reporting draw careful distinctions between different onboard components — a propulsion-related bridge console, engineering workstation, machinery automation gateway, and engine controller — because each represents a materially different level of operational impact. The decisive evidence would be a forensic trail showing a write-capable session, a valid command to the engine controller, and acceptance by that controller; until such evidence appears, Krell and others are describing the event as a propulsion-access incident, not a confirmed propulsion takeover.

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildComparisons to prior maritime OT incidents
The public account situates VL Prosperity against earlier maritime cyber events. The U.S. Coast Guard’s 2019 response to a malware incident aboard a deep‑draft vessel found that essential vessel control systems remained unaffected even when onboard computer networks were seriously degraded. Maersk’s experience during the 2017 NotPetya campaign similarly saw shore and terminal systems disrupted while its vessels remained maneuverable.
The closest publicly documented physical-control event cited by specialists is a 2013 University of Texas test in which researchers spoofed GPS and induced navigation corrections on a yacht; that experiment moved the vessel off course but did not control the engine. In 2025, French authorities investigated Remote Access Trojan (RAT) malware on the ferry Fantastic; the operator said the intrusion was neutralized without operational consequences.
Damon Small, market impact, and defensive prescriptions
Damon Small, a member of Xcape, Inc.’s board, warned of broader economic consequences: “The rapid escalation from a single novel maritime intrusion to federal tracking of nearly 20 compromised vessels globally directly threatens an already precarious global oil market, creating upward pressure on crude prices and downstream refined products.”
Small described supertankers as “self-sufficient floating cities” whose interconnected OT manages life support, navigation, and cargo operations — a complexity that raises the stakes when network boundaries are violated. He urged asset owners to enforce strict physical and digital network segmentation between vessel bridge controls, satellite communications, and IT networks, and to deploy unidirectional security gateways and mandatory anomaly monitoring across onboard industrial control systems.
The source’s summary of critical takeaways echoes those prescriptions: escalating market impact; recognition of complex OT vulnerabilities on supertankers; and essential defensive controls including segmentation, unidirectional gateways, and continuous industrial network monitoring. The report closes with a practical admonition: “Air-gapping vessel networks only works if you do not run an ethernet cable straight from the satellite dish to the propulsion engine.”
What this means for asset owners, security teams, and regulators
- Asset owners and ship operators: Expect heightened scrutiny of vessel OT configurations and pressure to demonstrate physical and logical segmentation between satellite links, bridge systems, and propulsion controllers. Operators will be asked for forensic logs showing whether any write-capable sessions reached engine controllers.
- Security teams and technologists: The incident reinforces emphasis on unidirectional gateways, continuous anomaly monitoring of industrial networks, and clear forensic trails that differentiate read-only access from write-capable control sessions.
- Regulators and investigators: The federal boarding and joint statement signal that agencies will combine criminal and safety inquiries; their findings — particularly any forensic evidence of commands sent to engine controllers — will set a public benchmark for what constitutes a confirmed propulsion takeover.
For now, investigators have confirmed a compromise of onboard networks and temporary access to the digital propulsion system, but public authorities have not reported operational disruption or environmental harm, and attribution remains unknown. The single, concrete forensic hinge that would change how this incident is recorded in maritime cybersecurity history — a logged, write-capable command accepted by an engine controller — has not been produced publicly. Whether investigators will find that trail is the central fact the industry, markets, and regulators are waiting to see.