Emerging Threats

Rows of computer servers and development workstations in a brightly-lit software development room with network devices in…

CISA Flags Actively Exploited GitLab, Cisco Flaws

CISA is sounding the alarm on two critical vulnerabilities, CVE-2026-97229 and CVE-2026-76418, after evidence revealed they're being actively exploited by hackers, putting organizations and federal agencies at risk. These flaws, particularly the severe CVE-2026-97229 with a 10.0 CVSS score, demand priority attention to prevent devastating attacks.

Analyst 207
Cryptocurrency trading floor with people working at desks and a large screen displaying a graph, with a symbolic lock in…

Binance Breach Exposes $6.3 Billion in Assets to Theft

A massive $6.3 billion crypto heist has hit Binance, with nearly $3 billion of those assets already frozen on-chain, and blockchain experts estimating a staggering $5.912 billion in stolen funds. This record-breaking theft sends shockwaves through the crypto world, dwarfing the next largest heist by a whopping four times.

Analyst 207
Government building with a computer and papers on a desk inside.

DHS Employee Data Archive Resurfaces Amid Removal Efforts

A searchable archive called Icepick, containing records for over 41,000 Department of Homeland Security employees, was briefly taken down after a DHS contractor requested its removal, but it quickly resurfaced under a different registrar. The database, claimed to be breached, offers a disturbing glimpse into the work-related records of DHS employees.

Analyst 207
Rows of empty shelves and industrial freezers in a refrigerated military storage room.

Pentagon Probes Cyberattack on Military Freezers

The Pentagon is investigating a mysterious cyberattack that caused six US military commissaries to experience freezer failures, spoiling food and leaving military personnel without access to essentials. The incident, which affected on-base grocery stores, is being treated as a possible cyberattack, with investigators working to uncover the cause and those responsible.

Analyst 207
Cryptocurrency exchange office interior with blurred computer screen and cityscape background.

Binance Probes $5.8 Billion Crypto Hack

Binance is on high alert, actively investigating a potential security breach that may have impacted $5.8 billion in crypto, and reassures users that their funds are safe. The exchange is urging caution and warning customers to be on the lookout for scams and unofficial requests for account information.

Analyst 207
Airport terminal scene with check-in counter, scattered passengers, and blurred laptop screen on travel agent's desk.

Amadeus Data Breach Exposes Airlines' Passenger Info

A massive data breach at Amadeus's Passenger Service System has compromised the sensitive information of around 92,000 Japan Airlines customers, with hackers gaining unauthorized access to the system over a prolonged period of nearly three years. The breach exposed passenger data, including details stored in the airline's travel booking display environment.

Analyst 207
Laptop on a desk in a minimalist room with soft natural light, screen blurred.

Hugging Face Hit by Resurgent Malware Campaign

Malware attackers cleverly exploited a tiny workflow change at Hugging Face, transforming trusted repositories into a powerful crypto-mining and backdoor distribution channel that racked up 28,412 downloads before being caught. In a cat-and-mouse game, 31 malicious repositories popped up across seven accounts in two waves since September, with attackers swiftly adapting to evade detection.

Analyst 207
Disrupted office workspace with laptop and cityscape, conveying concern.

Polymarket Breach Exposes $2.5M in Crypto Theft

A third-party provider was compromised, putting $2.5M in crypto at risk, and Polymarket has swiftly alerted authorities and taken action to protect its users. The platform temporarily halted trading, quickly resolved the issue, and got back online within an hour.

Analyst 207
Rows of computer servers and network equipment in a brightly-lit, empty server room with scattered cables and a blurred…

Cybersecurity Threats Exposed in Week of AI-Powered Attacks

This week, a shocking 40,573 secrets were exposed in a series of AI-powered cyberattacks, highlighting the ongoing struggle to protect sensitive information from falling into the wrong hands. The alarming findings, dubbed FortiBleed 2.0, reveal a disturbing trend of large-scale credential leakage and exploitation of old vulnerabilities.

Analyst 207
Server room interior with rows of equipment, one server highlighted with a red alert indicator.

Chinese Hackers Exploit PHP2Shell to Root 25 Servers

In a matter of hours, Chinese hackers exploited a PHP2Shell vulnerability to tunnel into an internal network, compromising multiple servers and launching a massive Active Directory attack campaign. The attackers rooted 25 servers and breached Palo Alto Networks firewalls across the US, Japan, Taiwan, and South Korea, with some networks still potentially under their control.

Analyst 207
Person holding iPhone with blank App Store page and generic trading platform icon.

Fake Crypto App Targets Solana Wallets, Drains $23K

Beware of fake crypto apps! A malicious iOS app, disguised as a trading platform called Padre Terminal, has already drained 27 Solana wallets of around $23,000 in cryptocurrency.

Analyst 207
Network device on a rack with cables and patch panels, under fluorescent lighting with a blurred office space in the…

Cisco SD-WAN Flaw Exploited to Deploy KeyDrift Malware

Cisco Talos researchers have uncovered a high-severity flaw in Cisco SD-WAN Controllers, exploited by hackers to deploy the KeyDrift malware and gain long-term access to sensitive data. This vulnerability, patched in February 2026, highlights the urgent need for robust security measures to prevent such attacks.

Analyst 207
Empty laptop screen on a clutter-free desk with soft natural light and blurred background decor.

Chrome Extensions Hijack 13.4M Users' Searches for Ad Revenue

A shocking 319 Chrome extensions, installed by 13.4 million users, have been secretly hijacking search queries to line their creators' pockets with ad revenue from major search engines like Bing and Yahoo. These sneaky extensions quietly took control of users' browsers, routing every search query through a proxy server to collect referral payments.

Analyst 207
Cluttered tech workbench with laptop, papers, and coffee cups, laptop screen showing abstract code.

Malware Exploits AI Apps to Deploy Crypto Miners

Malware operators are sneaking crypto miners into fake AI apps, like bogus desktop versions of Claude and ChatGPT, using clever tricks like a 12.73-day delay to evade detection. These malicious apps are being spread through fake GitHub projects and websites, hiding a crypto-mining payload in plain sight.

Analyst 207
A network operations center with computer workstations, servers, and a city view, with an empty laptop on a nearby table.

Malware Exploits OpenAI Keys for AI Queries

Malware has been discovered that exploits stolen OpenAI keys to secretly run AI queries, racking up bills for unsuspecting victims - with one variant capable of executing over 52 commands. This sneaky malware, detected by Cisco Talos, uses a Go-based implant to route requests through compromised machines.

Analyst 207
Modern Asian government building façade with subtle tech hints.

NetamLoader Exposes Sophisticated APT Attack on Asian Governments

Kaspersky analysts uncovered a highly sophisticated APT attack targeting Asian governments, using a custom .NET-based loader called NetamLoader to infiltrate a unique Windows 10 build. The attack began with a malicious CAB archive cleverly hidden in the Windows update cache, showcasing a cunning tactic to gain a foothold in high-security environments.

Analyst 207
Government office setting with scattered papers and a blurred computer screen, hinting at a data breach, with an abstract…

Hacktivists Expose Data on 41,000 DHS Employees in Breach

A massive data breach has exposed the personal info of over 41,000 Department of Homeland Security employees and contractors, revealing key personnel involved in covert operations, leak investigations, and high-stakes deportation programs. The leaked dataset, published online, is a stunning blow to DHS's internal security.

Analyst 207
Belgian government office interior with subtle tech infrastructure in daylight.

Belgium's Tax Agency Hit by Cyberattack, Disrupts Online Services

Belgium's tax agency, FOD Financiën, has confirmed a cyberattack that forced it to take several online services offline to prevent further damage and protect sensitive data. The agency is now working to secure its systems and restore services as soon as possible.

Analyst 207
Linux terminal on a laptop screen in a network operations center with blurred command-line interface.

CISA Warns of Linux Flaw Chained in PHP2Shell Attacks

CISA warns that a Linux flaw can be exploited in conjunction with other vulnerabilities to implant PHP webshells and grant attackers root access, posing a critical threat to affected systems. Federal agencies are urged to patch vulnerable systems by Saturday to mitigate the risk.

Analyst 207
Rows of filing cabinets and server racks in a brightly-lit government records storage room with scattered papers on a table.

Government Database Breach Exposes 42M Records

A shocking discovery by cybersecurity researcher Jeremiah Fowler revealed a massive government database breach, exposing a staggering 42 million records of sensitive personal info to the public. The unsecured database contained a decade's worth of names, addresses, and email addresses, all freely accessible to anyone who stumbled upon it.

Analyst 207
GitHub repository page on a laptop amidst a cluttered developer's desk with papers and coffee cups.

GitHub Supply Chain Targeted in 83 Attacks Within Hour

In a shocking display of speed and stealth, attackers launched 83 targeted assaults on GitHub's supply chain within a single hour, aiming to infiltrate and manipulate code repositories. The attackers' ultimate goal was to gain control of credentials and alter code to suit their malicious purposes.

Analyst 207
Smartphone on a neutral surface with a blurred urban background and a faint voice call interface on its screen.

Telegram Android Flaw Exposes Users to Code Execution via Voice Calls

A security flaw in Telegram's Android client left users vulnerable to code execution via voice calls, but thankfully, the issue was swiftly patched in version 12.10.4. Researchers discovered the bug, which allowed attackers to run code on victims' phones simply by making a call.

Analyst 207
Rows of computer servers and networking equipment in a brightly-lit server room with a laptop in the foreground.

GitLab Vulnerability Exposes Alpine Linux Server to Code Execution Risk

A critical GitLab vulnerability, rated CVSS 10.0, was exploited just days after a fix was released, putting Alpine Linux's server at risk of code execution - and highlighting the importance of swift and secure updates. The attackers probed the server using a newly registered account, submitting crafted CI configurations to exploit the vulnerability.

Analyst 207
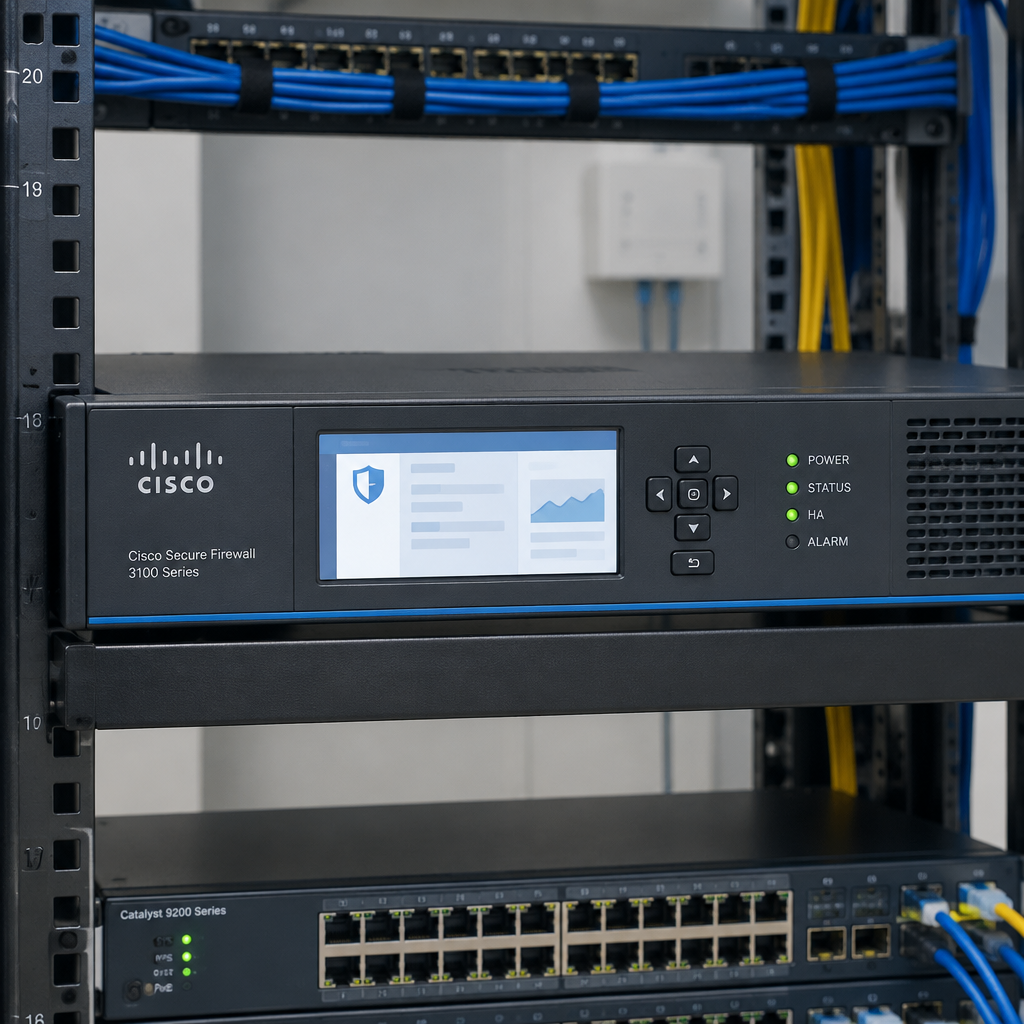
Cisco networking device on a rack with cables in a professional IT setting.

Cisco Patches Actively Exploited VPN Flaw in ASA and FTD Software

Cisco has patched a high-severity VPN flaw in its ASA and FTD software, known as CVE-2026-76418, which has already been exploited by hackers to cause devices to crash and creating a denial-of-service condition. This vulnerability, with a CVSS score of 8.6, was caused by logic errors in secondary authentication setup.

Analyst 207