[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
In a single, remarkable run, an AI-powered security agent uncovered 21 zero-day vulnerabilities in the widely-used FFmpeg library, a feat that cost just $1,000 and showcases the incredible potential of autonomous security testing. The agent scanned 1.5 million lines of code to produce these groundbreaking findings.
Oxford University student data has been breached once again, this time through a career platform compromise, leaving records exposed. The incident is a separate attack from a break-in that occurred just last month.
Cisco is warning of a high-severity vulnerability in its Catalyst SD-WAN Manager that allows attackers to execute commands as root, and it's already being exploited by hackers. This flaw, rated 7.8 on the CVSS scale, could give attackers control over your system if they're able to upload a malicious file.
Imagine a game-changing air defense system that seamlessly connects NATO nations, allowing countries with different systems to share data and operate as one - Lockheed Martin's groundbreaking concept is making this vision a reality. Led by Lockheed Martin UK, a consortium of industry leaders has unveiled a pioneering Ground-Based Air Defense solution that could revolutionize allied defense operations.
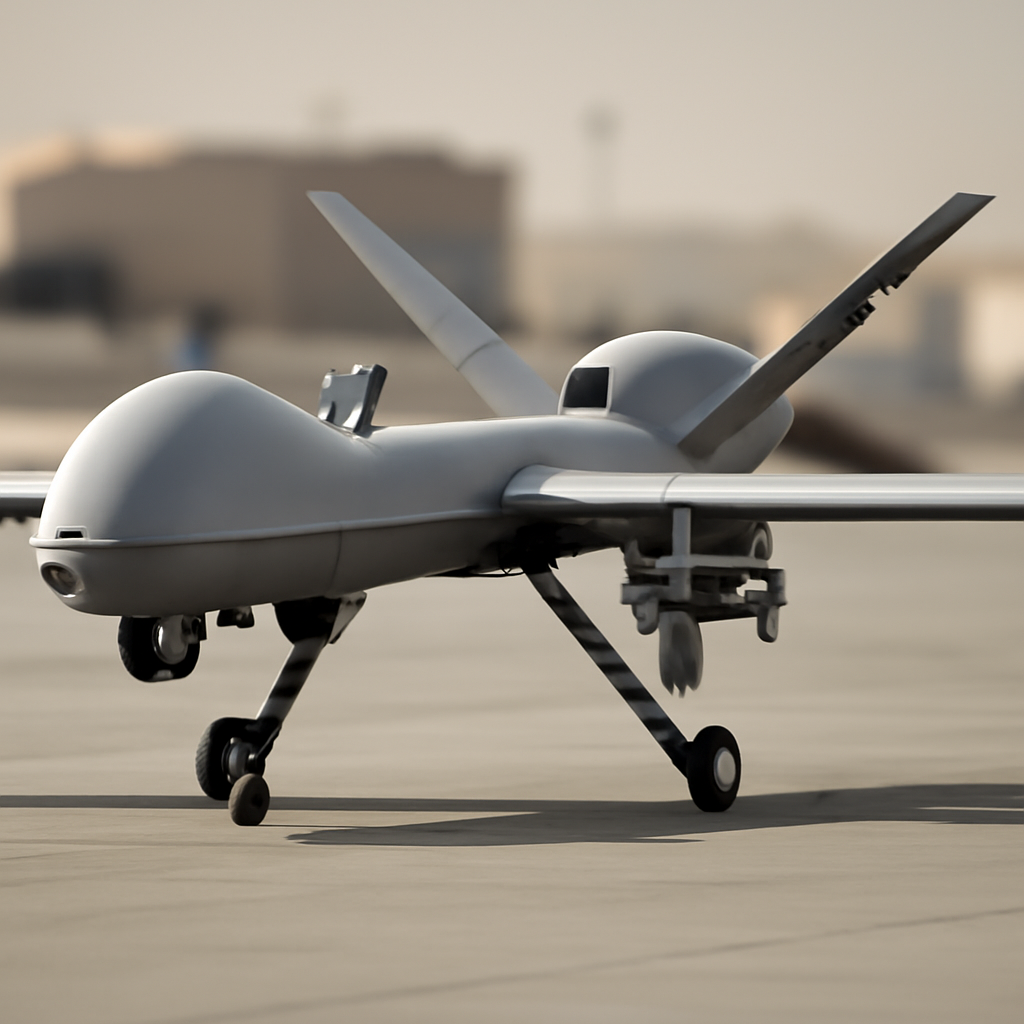
The US Air Force is on a mission to replenish its fleet of MQ-9 Reapers, and it's turning to General Atomics for help, with plans to buy several unused MQ-9A Block 5 aircraft. The scramble comes as General Atomics reveals an alarmingly small inventory of just a handful of new MQ-9As available worldwide.
The Pentagon is fast-tracking the acquisition of small, one-way attack drones to equip every squad with a powerful new weapon, aiming to achieve this goal later this year. This push comes after Defense Secretary Pete Hegseth vowed to cut through red tape and unleash the full potential of the US drone industrial base.
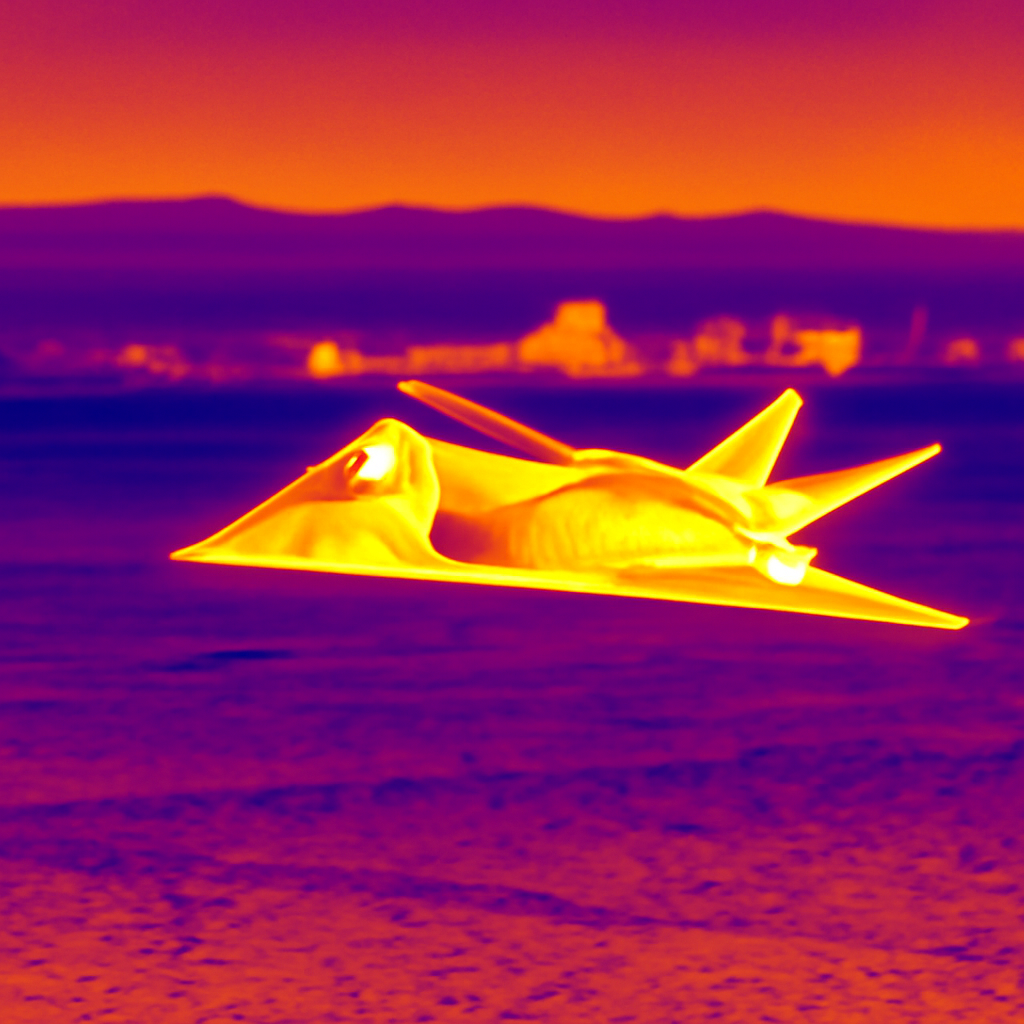
A decades-old stealth fighter concept has resurfaced in discussions after a viral sighting near Area 51, sparking fresh interest in a mysterious aircraft that was once deemed too unstable for serious consideration. The unusual plane's distinctive double arrowhead design was caught on thermal footage near Groom Lake, leaving many to wonder about its true purpose.
The Navy has raised its budget for the new trainer jet's development phase by $900 million to $2.7 billion, citing new information about program costs. This change comes amid pushback from the industry, as the service seeks to move forward with its Undergraduate Jet Training System.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
US forces have intercepted and shot down four Iranian drones heading towards the Strait of Hormuz, swiftly responding to an immediate threat to regional maritime traffic. The bold move also included targeted strikes on Iranian coastal radar sites to prevent further attacks.
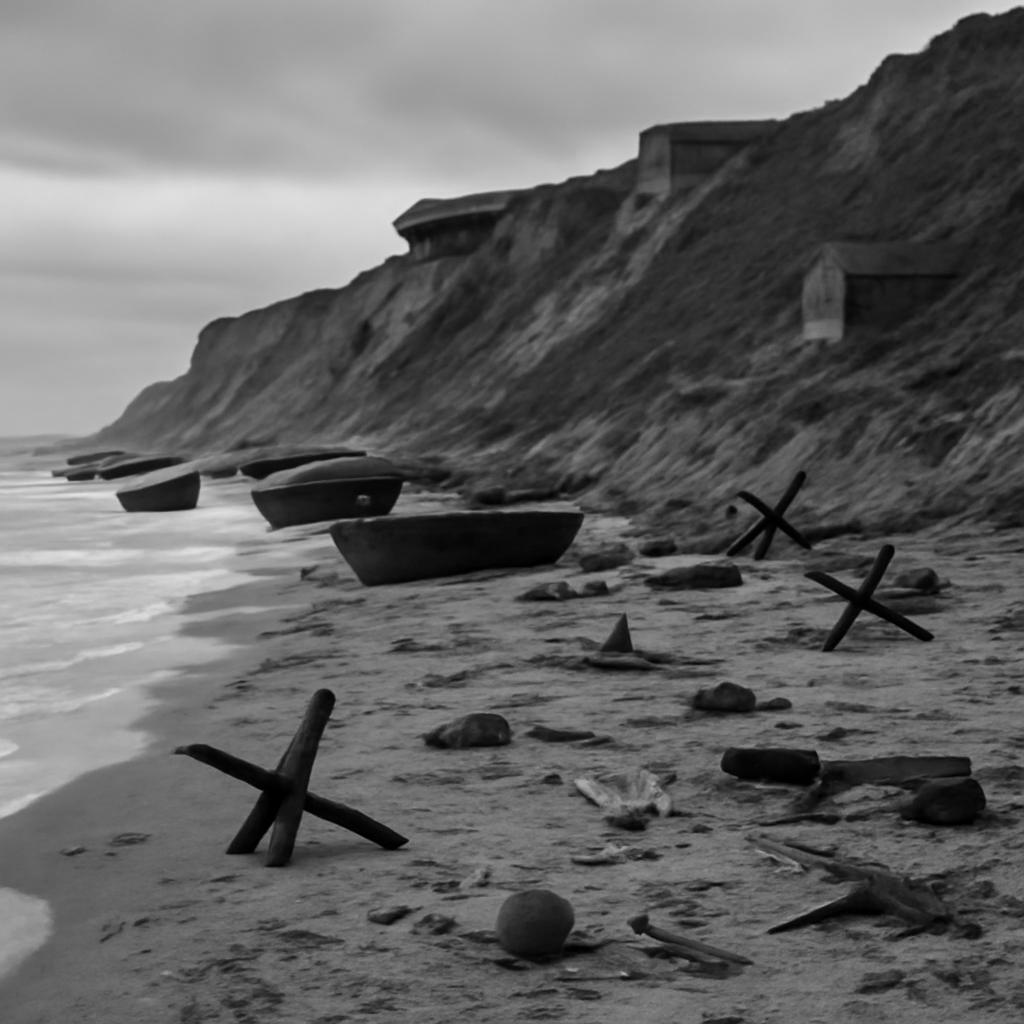
Imagine facing machine gun fire head-on, seasick and disoriented, as you stormed Omaha Beach on June 6, 1944, with nothing but chaos and destruction awaiting you. For brave soldiers like Private First Class John Robertson and 1st Lieutenant Jimmie Monteith Jr., this was the terrifying reality that tested their valor and forever shaped history.
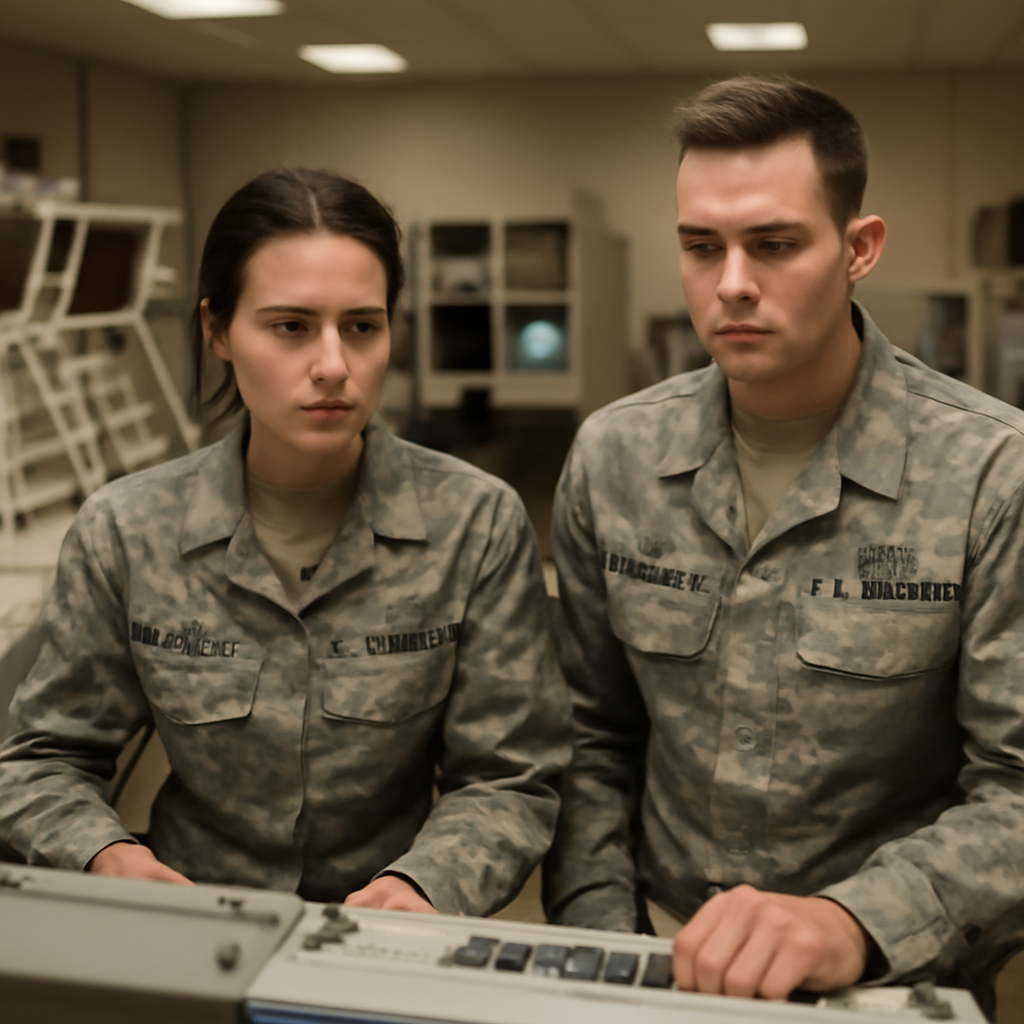
In a simulated launch exercise, skilled missileers like First Lt. Pamela Blanco-Coca and 2nd Lt. John Anderson demonstrate their expertise with the Minuteman III system, carrying out precise key turns that send a launch vote to ICBMs in their flight area. With a properly conducted key turn, these airmen showcase their critical role in maintaining a strong national defense.
Join a live webinar on June 24, 2026, to explore how the Pentagon's new emphasis on research security is transforming the way universities, government agencies, and institutions protect against foreign exploitation. Earn 1 CPE credit while learning how to bolster defenses for basic and applied research in a rapidly evolving security landscape.
Microsoft is stirring up controversy in the vulnerability disclosure debate, clashing with a security researcher over the responsible handling of zero-day vulnerabilities. The tech giant's strong response, including threats of legal action, has sparked heated discussion on coordinated disclosure.
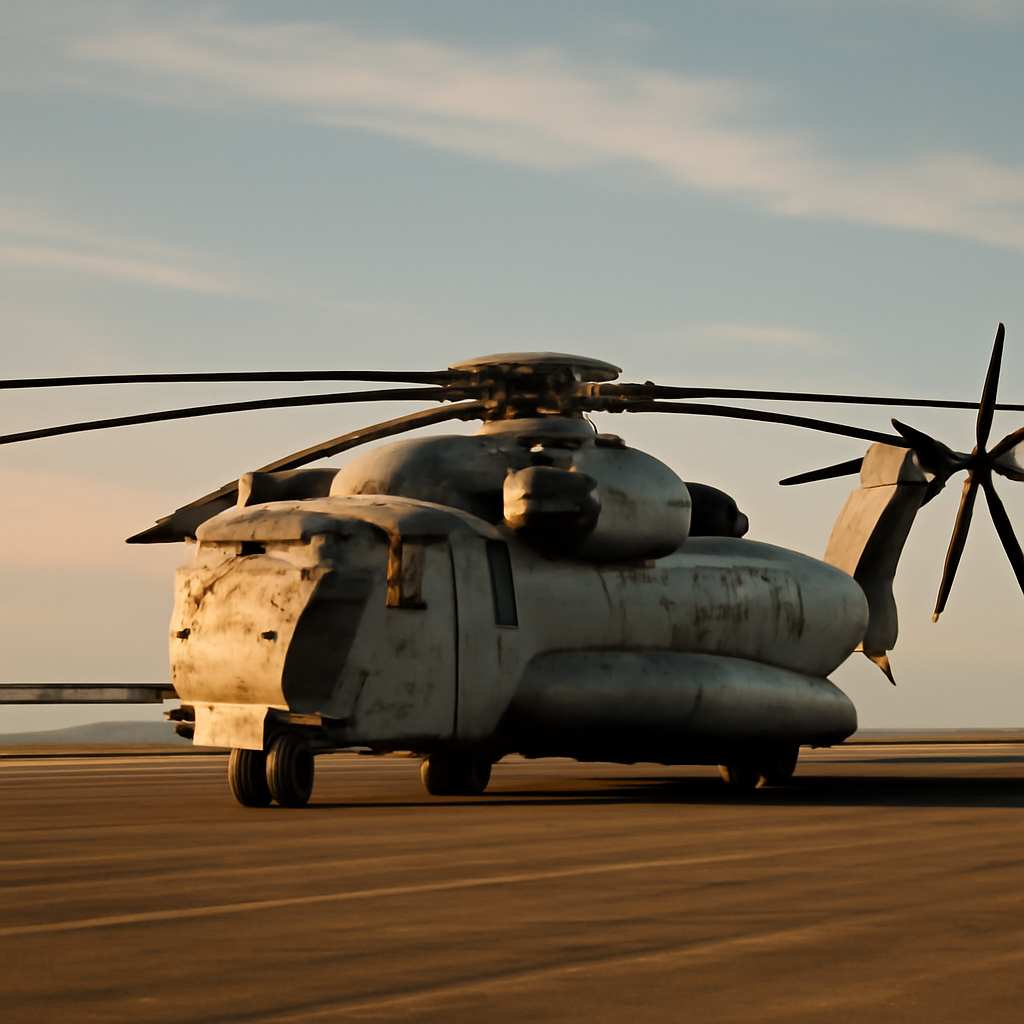
Meet Steve Jones, a former MH-53E Sea Dragon pilot who learned the helicopter's limits the hard way - and lived to tell the tale of this powerful machine, built for brute strength and endurance with three GE engines and massive fuel sponsons. The MH-53E was a beast that could fly, hover, and tow with the best of them, but as Jones puts it, "it's really a young person's game."
US Secretary of Defense Pete Hegseth's recent speech at the Shangri-La Dialogue in Singapore left many wondering why he didn't seize the opportunity to reaffirm US support for Taiwan, a crucial moment to make a strong statement in the region. By choosing not to directly address Taiwan, Hegseth missed a chance to show strength and clarity in the face of growing uncertainty.
Palo Alto Networks has sounded the alarm on a critical PAN-OS vulnerability, CVE-2026-0257, that's being actively exploited by threat actors to bypass authentication and gain unauthorized access to VPN connections. This security gap could allow attackers to circumvent controls and initiate their own VPN sessions, putting your network at risk.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Congress is pushing the Army for a clearer roadmap to achieve its transformation goals, with Rep. Mike Rogers bluntly stating that the Army hasn't done its homework. The House Armed Services Committee has now mandated an annual report and briefing from the Army to keep lawmakers in the loop.
Beware of UNC3753, a notorious group that's been stealing sensitive data from US law firms and other professional services, using clever vishing tactics and lightning-fast intrusions to extort their victims. In some cases, they can go from initial contact to data theft in under an hour.
Meet UNC3753, a notorious extortion gang that's taking corporate hacking to a whole new level - from deceitful phone calls to in-person visits, where they show up at companies' doorsteps with thumb drives, targeting dozens of US banks, law firms, and professional services firms in just a few short months. Their tactics have evolved from fake emails to help-desk calls and now, brazen doorstep drop-offs.
Major websites, including Toshiba and Muji, have been compromised by a rogue login prompt scam through polyfill.io, tricking visitors into entering sensitive information. If you encountered the fake sign-in screen, be sure to cancel and change your password to protect your account.
SolarWinds has issued an emergency hotfix to address a critical flaw in its Serv-U file transfer product, which hackers are actively exploiting to crash servers with specially crafted POST requests. A denial-of-service vulnerability, tracked as CVE-2026-28318, can be triggered without authentication, posing a significant threat to users.
Meet IronWorm, a sneaky Rust-based malware that's infecting the npm ecosystem by scraping sensitive secrets from developers' machines and spreading through poisoned packages. This stealthy threat hides behind an eBPF kernel rootkit and communicates with its operators over Tor.
A Chinese-linked espionage group, tracked as UNC5221 or VerdantBamboo, exploited new malware to secretly maintain access to US networks for over 18 months, evading detection by blending in with legitimate traffic. The attackers used a sophisticated backdoor called Brickstorm to prolong their stay undetected.
Cisco SD-WAN is under siege from a zero-day vulnerability that's being actively exploited - and there's no patch in sight, leaving sys admins scrambling to protect their networks.