[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
A critical vulnerability in SimpleHelp, known as CVE-2026-48558, lets hackers create rogue remote support accounts and gain privileged access to servers, allowing them to execute scripts and wreak havoc on your system. This gaping security hole enables unauthenticated attackers to bypass multi-factor authentication and log in as a Technician user, putting your entire network at risk.
Fincantieri Marine Group CEO George Moutafis says the Navy's Constellation frigate program was doomed by procurement issues, noting that sometimes "perfection is the enemy of more than good enough". The program's struggles began when constant change orders derailed its development, despite starting with the proven FREMM design.
A Russian Tu-22M3 bomber dramatically crashed during a routine training flight in Siberia, with footage showing the aircraft plummeting nose-first into the ground, but thankfully, all crew members ejected safely with no ground casualties. The incident occurred during an approach to land in the Irkutsk region, with the plane not carrying a combat load.
The Air Force's commitment to keeping the A-10 flying through 2030 is being undermined by its own budget, which allocates zero dollars for modernization and cuts depot maintenance, putting the fleet's future in jeopardy. This disconnect between promise and funding is slowing down rebuilding efforts, making them costlier and increasingly infeasible.
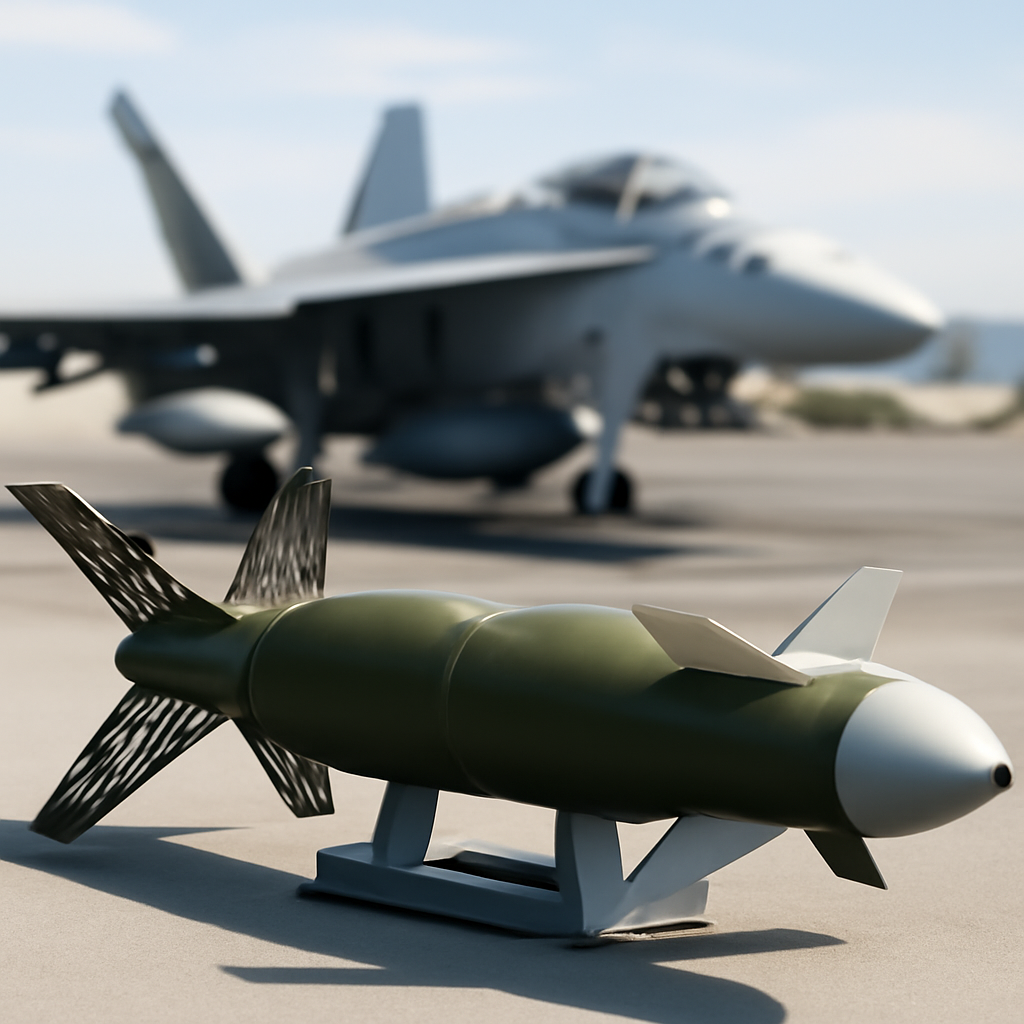
The US military is exploring the potential of the 2,000-pound Joint Direct Attack Munition Extended Range (JDAM-ER) to take out heavily fortified bunkers and deeply buried targets. The Pentagon is seeking to assess and upgrade the JDAM-ER's capabilities to enhance its bunker-busting abilities.
France is taking a bold step towards European defense cooperation, announcing exclusive negotiations with MBDA and Safran to develop a cutting-edge, long-range artillery system to replace its aging Lance Roquettes Unitaire launchers. This strategic move aims to bolster Europe's military capabilities and sovereignty.
The government's sudden move to restrict exports of Anthropic's Fable 5 AI model has sparked a heated debate, with experts arguing that such limitations could hinder crucial bug fixes and security patches. By restricting Fable 5, is the White House inadvertently putting innovation and cybersecurity at risk?
As Sweden's defense landscape evolves, Peter Hultqvist, the country's former defense minister, is open to the idea of the state taking part-ownership in Saab, a move he believes would bolster national security. This potential stake would enable Sweden to protect its core interests in critical defense technologies like submarines, sensors, and fighter aircraft.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A sophisticated cyber threat group linked to China, known as UNC6508, has launched a targeted attack on medical research institutions in North America, exploiting vulnerabilities in REDCap servers to gain a foothold. The intrusions, which began in September 2023, aim to compromise sensitive research data.
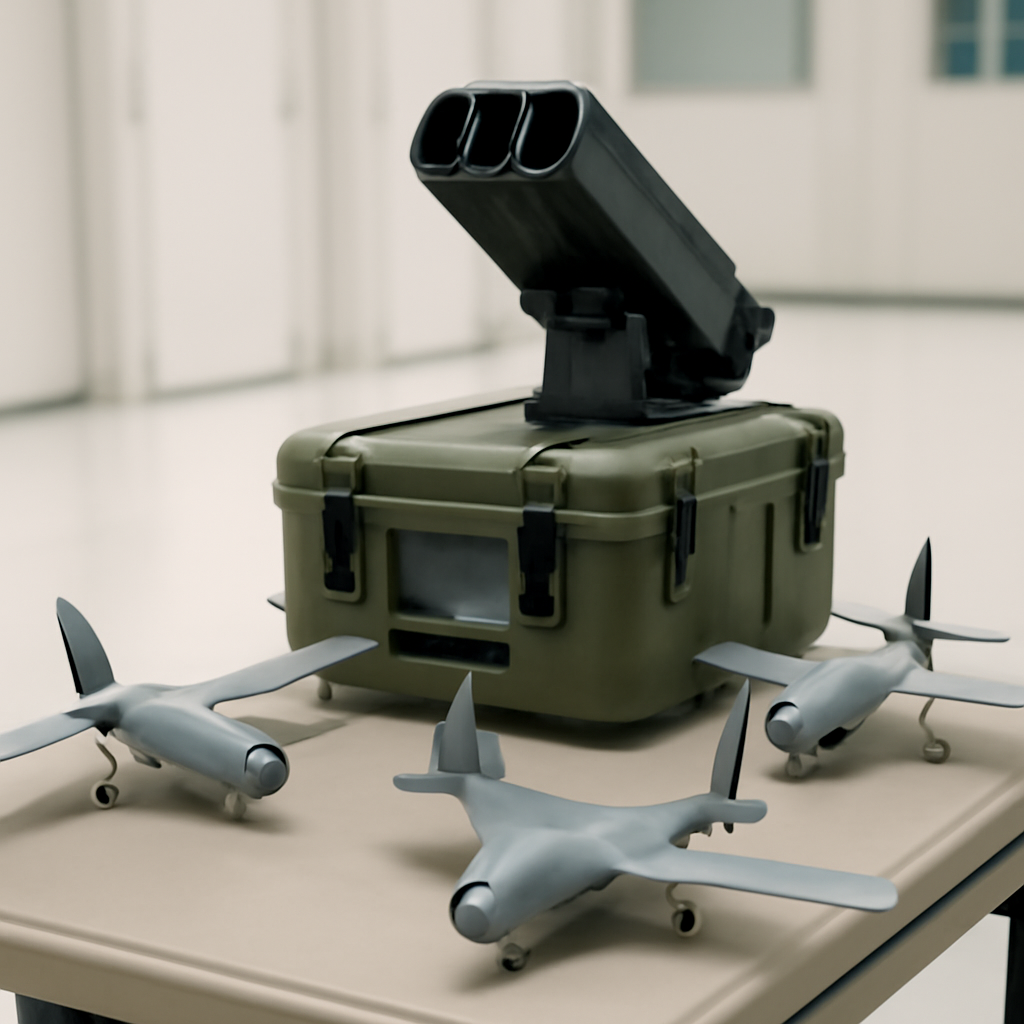
Meet the Black Recon microdrone system, a game-changing innovation that empowers operators with persistent situational awareness and faster access to actionable intelligence. This cutting-edge tech launches, recovers, and recharges autonomously from manned ground vehicles, revolutionizing high-tempo missions.
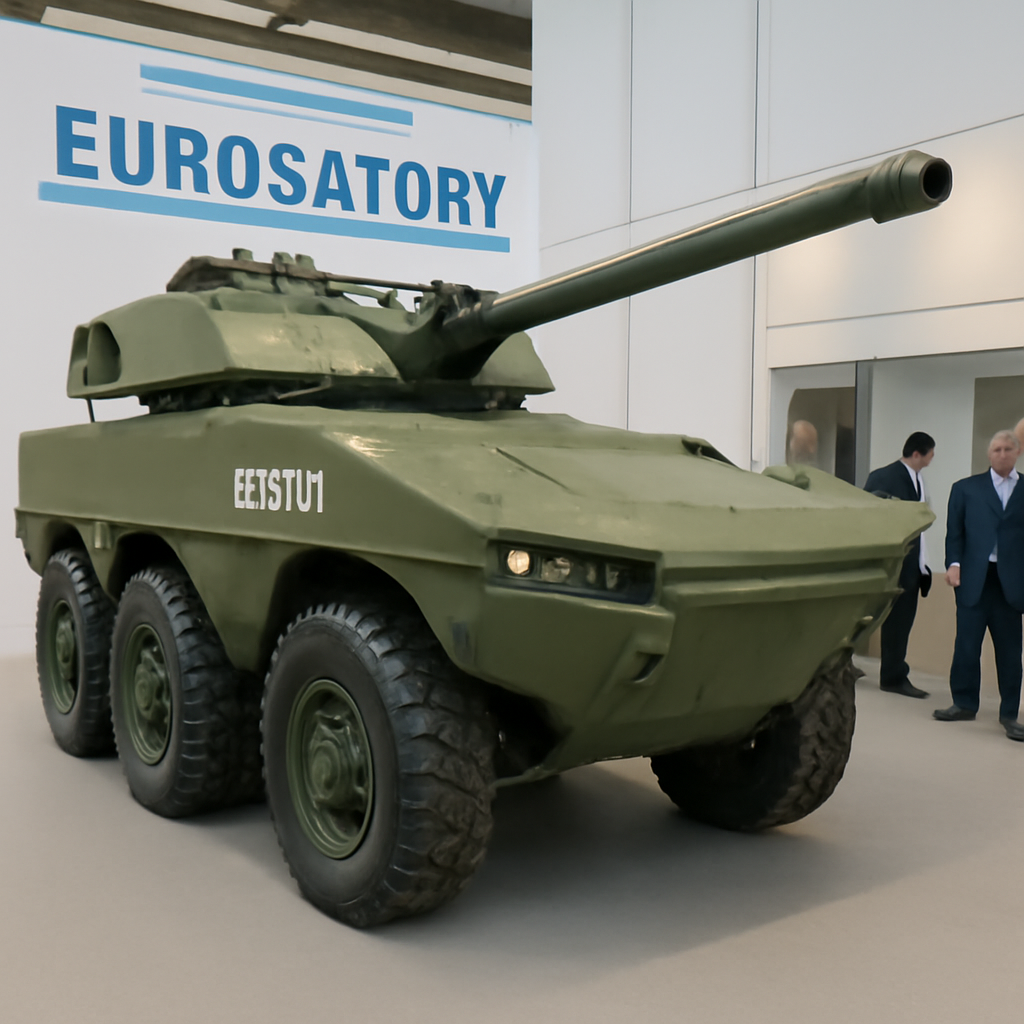
Meet Fenris, a game-changing 6×6 armored vehicle packing a powerful 105mm gun that can be airlifted, even on an A400M. Developed in just over a year, Fenris is Arquus and John Cockerill Group's rapid response to the renewed need for direct fire support on the battlefield.
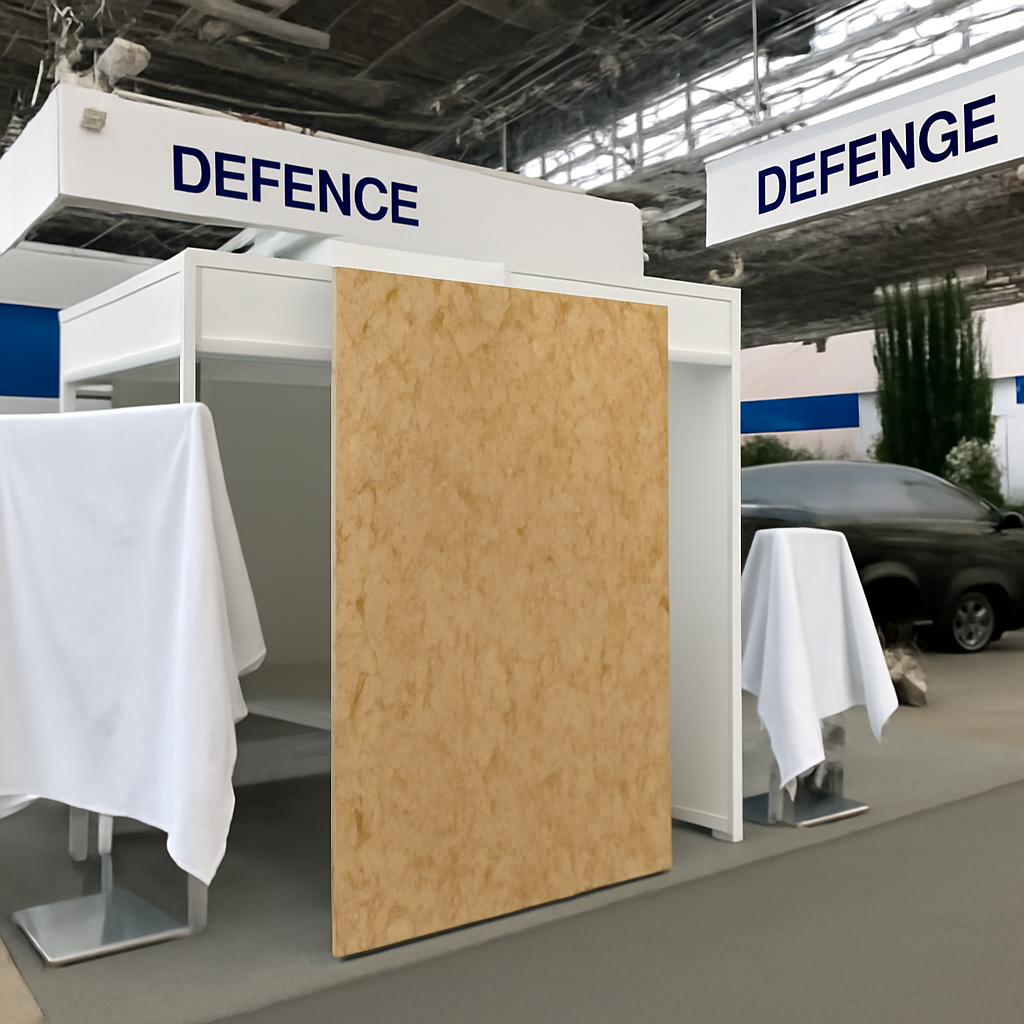
The Eurosatory exhibition took a shocking turn when organizers suddenly boarded up Israeli defense industry pavilions, despite the companies meeting all French government demands and showcasing only defensive systems. The Israeli Ministry of Defense blasted the move as discriminatory and politically motivated.
The harsh reality is that most organizations are flying blind when it comes to their data, with little insight into what they have, where it's stored, or if it's properly secured. This knowledge gap is a major hurdle for federal agencies looking to harness the power of AI while keeping sensitive data safe.
The US Department of Defense is overhauling its cyber defense strategy, shifting towards a holistic approach that emphasizes cyber resilience, enterprise modernization, and operational effectiveness. Chief Information Officer Kirsten Davies is leading the charge, driving practical reforms to boost automation, streamline processes, and strengthen cybersecurity across the department.
A critical security breach has hit the popular OptinMonster plugin, used by over 1.2 million websites, which delivered malicious JavaScript to unsuspecting users via a compromised content distribution network. The attack, detected by ecommerce security firm Sansec, injected harmful code into websites for a brief but perilous window of time.
The Council of Europe has fallen victim to a massive data breach, with hackers claiming to have stolen a whopping 297 GB of sensitive information, including HR records, payslips, and medical data, by exploiting a zero-day flaw in Oracle PeopleSoft. The ShinyHunters extortion group is behind the breach, boasting a haul of 429,000 files from the attack.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A shocking vulnerability chain in LiteLLM has been discovered, allowing hackers to hijack servers with just a low-privilege account, and experts warn it's a critical threat with a near-perfect CVSS score of 9.9. By chaining three distinct bugs, attackers can escalate their access to full admin rights and run code on the server.
Cisco has patched a high-risk SD-WAN flaw, known as CVE-2026-20262, that was being exploited in zero-day attacks to gain root privileges. The vulnerability allowed attackers to create or overwrite files on affected systems, and Cisco has now released security updates to fix the issue.
A ransomware attack by the Anubis group on the Adriatic Port Authority exposed significant gaps in maritime security, putting sensitive employee records and critical infrastructure at risk. The breach, which occurred on December 11, 2025, resulted in the loss of around 2% of the authority's data, with some information making its way to the dark web.
As the Federal Data Center Enhancement Act of 2023 lapses on September 30, 2026, a crucial safeguard for secure and reliable access to federal information systems will vanish, leaving gaping security holes unaddressed. Without an extension or replacement, federal data centers may operate with little oversight, putting sensitive information at risk.
Over 1.2 million WordPress sites are at risk after attackers infiltrated a trusted vendor's network, injecting malicious code into popular plugins like OptinMonster, TrustPulse, and PushEngage. This sneaky hack creates rogue admin accounts, putting sites at risk of takeover - all without ordinary visitors even noticing.
The Council of Europe is actively investigating claims by the ShinyHunters extortion group that sensitive internal documents were stolen, and is working to assess the situation. The organization, which represents 46 European member states, has confirmed the probe but declined to provide further comment at this stage.
A single click on a seemingly trustworthy Microsoft link could have put sensitive information like emails, calendar details, and files at risk of being exposed to attackers, thanks to a flaw in Microsoft 365 Copilot Enterprise Search. This vulnerability, known as SearchLeak, highlights the importance of staying vigilant even with trusted sources.
A critical lapse in Microsoft's SSL certificate caused widespread disruption, leaving IT professionals scrambling with untrusted-connection warnings when testing Microsoft 365 connectivity via connectivity.office.com. The certificate expired on June 14 and took 35 hours to address, impacting routine diagnostics and network checks.