[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
Cyber attackers are exploiting two zero-day vulnerabilities, CVE-2026-15409 and CVE-2026-15410, in SonicWall appliances, with ransomware attacks seemingly their ultimate goal. Rapid7's team has thwarted attempts at data exfiltration and encryption, but the threat remains.
Australia's laid-back approach to the polar regions is no longer sustainable, and it's time for a bold new strategy to keep up with global competition. The country's reactive posture is putting its interests at risk, warns a new report on polar security.
The Royal Air Force has clarified that its recent purchase of a dozen F-35A aircraft is primarily for training and conversion purposes, not to bolster its nuclear strike capabilities. This move underscores a strategic shift, separating the jets' day-to-day role from their potential nuclear support functions for NATO.
As Gen. Chance Saltzman prepares to retire, he's urging international military leaders to prioritize unity and strategic advantage in the face of budget cuts, emphasizing that the path forward will be crucial to securing a military edge. With his departure looming, Saltzman's parting words stress the importance of collaboration and wise decision-making.
Federal agencies are racing against the clock to modernize their identity infrastructure, securing legacy systems while navigating the rapid evolution of AI and emerging post-quantum threats. As AI continues to advance at breakneck speed, agencies must build adaptable cybersecurity strategies to stay ahead of the threat landscape.
Imagine having your every online move tracked by someone you trust - all because they exploited a feature meant to make your life easier. A security researcher found that a stalker can use Google Chrome's sync feature to monitor a victim's online activity, gaining access to their browsing history from anywhere in the world.
Dutch police have cracked down on a massive €100 million investment fraud ring, arresting multiple suspects, including a 46-year-old Israeli-Polish national with a notorious hacking past. The international sweep resulted in detentions across Cyprus, Greece, and Belgium, with authorities vowing to bring the alleged perpetrators to justice.
Zoom has warned users of a high-severity vulnerability in its Windows desktop client and software development kit that could let hackers hijack accounts without authentication. This critical flaw, tracked as CVE-2026-53412, has a severity score of 9.8 out of 10.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Researchers just uncovered a cutting-edge IoT botnet framework, TuxBot v3 Evolution, that leverages AI to streamline its development - but surprisingly, the AI also slipped in a crucial safety disclaimer that was left intact. This innovative framework combines old-school botnet tactics with modern tools, making it a potent threat.
A Russian-speaking hacker, known as "bandcampro", cleverly exploited Google's open-source Gemini CLI AI tool to create a small but powerful botnet, taking control of eight systems at a dental clinic and breaching the OpenDental database. The AI tool even helped the hacker troubleshoot problems and optimize operations in real-time, making it a highly effective accomplice in the cyber attack.
Beware of OkoBot malware, a sneaky threat that's been targeting hardware wallet users since April 2025, tricking hundreds of victims in over 25 countries into divulging their seed phrases through clever phishing tactics. This malicious software can even infiltrate legitimate wallet apps like Ledger and Trezor, replacing their interfaces with fake recovery pages.
The US Cybersecurity and Infrastructure Security Agency (CISA) has warned of three SharePoint vulnerabilities, including CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164, that are being actively exploited by attackers. These flaws, affecting on-premises SharePoint Server installations, pose a significant threat, with one remote code execution flaw rated 8.8 in severity.
On July 14, a supply-chain intrusion briefly introduced trojanized AsyncAPI packages into the npm ecosystem, putting users at risk of credential-stealing malware. Five malicious releases in the @asyncapi namespace were downloaded hundreds of thousands of times during a four-hour window.
A massive six-month phishing campaign, dubbed SeasonalInvite, used fake electronic greeting cards to trick victims into installing legitimate remote monitoring and management software on their devices. Over 959 domains were used in this scam, which went undetected from January to June 2026.
Thousands of systems may be at risk of a Secure Boot bypass due to vulnerabilities in 11 UEFI shim bootloaders, all signed by Microsoft, that allow attackers to circumvent security measures. These weaknesses have the potential to create a broad attack surface, putting many devices at risk of compromise.
Major tech players, including Adobe, Mozilla, Google, and Broadcom, have just rolled out critical security updates to fix dozens of vulnerabilities - and it's crucial to install them ASAP to avoid potential code execution and privilege escalation threats. Adobe alone is patching 88 flaws, including eight high-risk issues in ColdFusion that could lead to serious security breaches.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Microsoft has temporarily halted a critical patch update for certain Dell devices due to compatibility issues that can cause overheating, shutdowns, and poor performance. A fix is expected soon, with both companies working together to resolve the problem.
Meet the AI-powered tool that just discovered a zero-day vulnerability in a popular WordPress plugin, and learn how its automated pipeline can detect and exploit weaknesses in code. This game-changing technology can extract sensitive data, like password hashes and secret tokens, from live databases.
A security researcher has unveiled a proof-of-concept exploit, called LegacyHive, that targets a vulnerability in Windows User Profile Service, allowing for a potential elevation of privileges. This newly disclosed exploit requires just a standard user credential and a third username to launch.
Ransomware attacks are surging, with a staggering 79% of incidents linked to compromised identities and legitimate user logins, making it the most common entry point for hackers. This marks a significant shift away from traditional software flaw exploitation, now accounting for just 18% of initial attacks.
As enterprises shift to AI-driven workflows, their security teams struggle to keep up, risking loss of visibility as data interactions move beyond traditional network boundaries. With modern protocols like TLS 1.3 and HTTP/3 blocking interception, outdated SASE architectures are failing to keep pace.
A security researcher is sounding the alarm about a newly unveiled Windows zero-day exploit, dubbed LegacyHive, which targets the Windows User Profile Service and could allow for a full system compromise. The proof-of-concept exploit, published by a zero-day hunter known as NightmareEclipse, is just a glimpse of the potential damage this vulnerability could cause.
Progress Software swiftly responded to a credible security threat, suspending ShareFile Storage Zones Controller for four days to safeguard customer data, before resuming service on July 14. The brief outage ensured the protection of its flagship enterprise file-sharing service and private data storage.
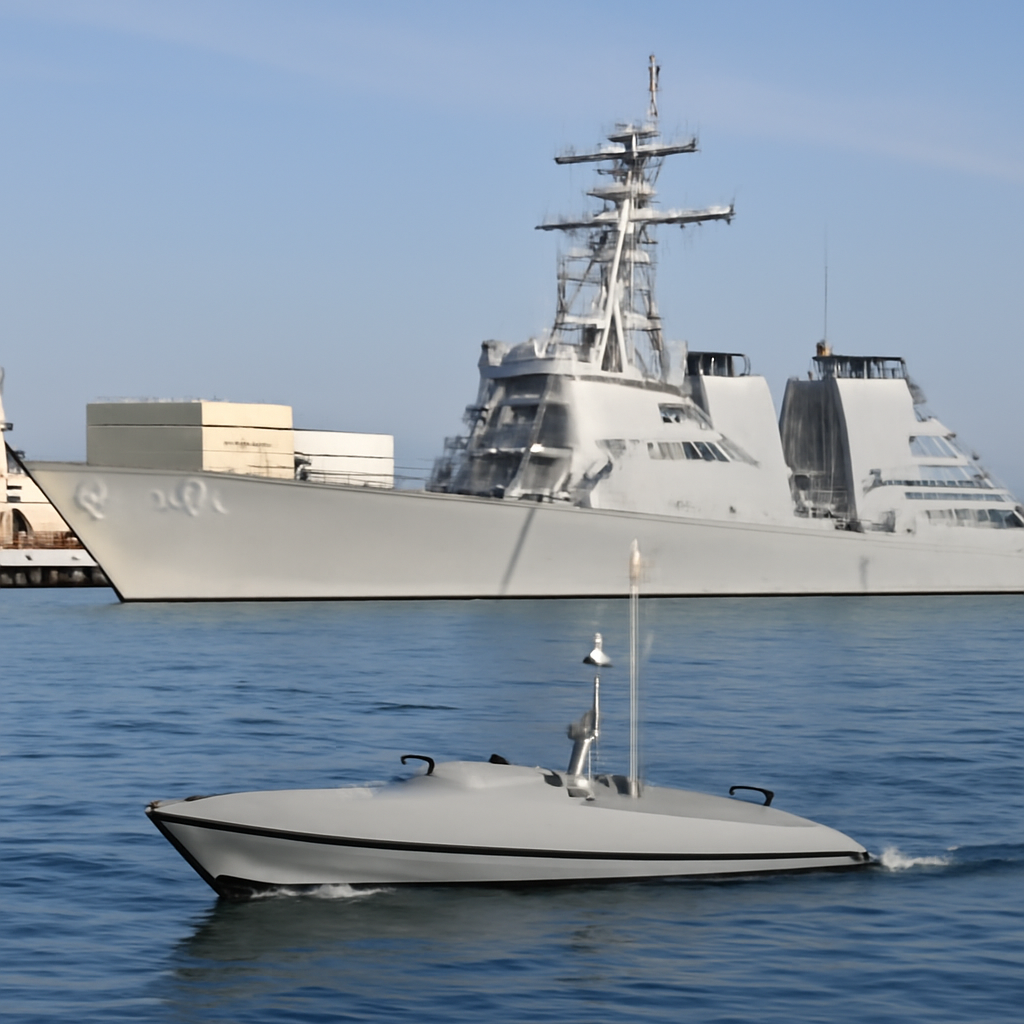
The US has made history with its first combat strike using sea drones, targeting Iran's Bandar Abbas Naval Base in a bold move to protect commercial shipping in the Strait of Hormuz. The daring operation, carried out by CENTCOM, hit a submarine facility and dozens of other targets across southern Iran.