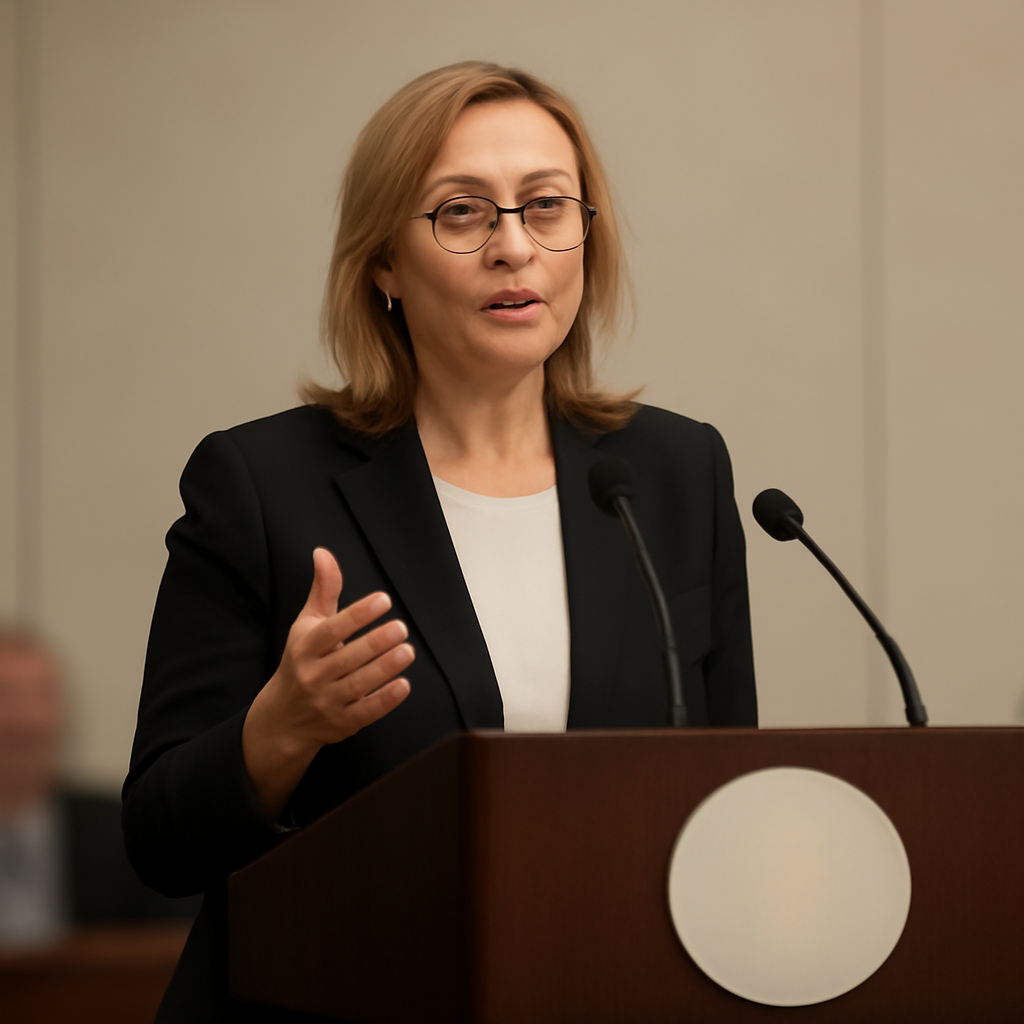
FCA's Jessica Rusu: extend major-incident reporting to AI failures
Speaking at Bloomberg's UK Policy Series on Monday, Jessica Rusu framed increased autonomy in financial services as a force multiplier for risk unless accountability keeps pace. She told the audience that the FCA's existing rules already require firms to report major incidents, and that "must extend to significant AI failures and near-misses." Rusu tied the call to both consumer protection and national security, noting that "near-miss reporting for agentic AI is becoming a national security priority." For the FCA, the question is not if AI incidents should be reported, but how firms should classify and submit reports when systems operate with greater autonomy.
Kanishka Narayan: government plans to work with Parliament and technical experts
Last week, UK artificial intelligence minister Kanishka Narayan outlined government plans to collaborate with Parliament and technical experts on strengthening the regime to guard Britain from "AI-driven cyber threats and loss-of-control risks." Narayan said that work will include "identifying and reporting on serious incidents and near misses, including reducing AI-driven risk across essential services, and ensuring serious AI incidents can be properly reviewed." His statement places incident identification and review at the center of the government's AI safety priorities for critical infrastructure, including financial services.

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildGuidelight AI Standards' Steven Adler: learn from aviation's near‑miss culture
Steven Adler, co‑founder and chief scientist of independent nonprofit Guidelight AI Standards, told MPs that AI oversight could borrow from aviation, where near‑miss reporting is mandatory in most jurisdictions. "The way this works in aviation is that you not only want to learn about the serious crashes where someone has in fact died; you want to learn about the near-misses, because you can learn from those and help avoid them in the future," Adler said. His comparison frames near‑miss reporting as a preventive safety mechanism, one that regulators and firms might emulate to capture actionable lessons before incidents escalate.
Cyber Security and Resilience Bill: amendments still under consideration, says Alexandra Jones
Despite the regulator and ministerial statements, the government has not yet committed to adding AI‑specific measures to the Cyber Security and Resilience (Network and Information Systems) Bill. Alexandra Jones, Director General for Growth, Science and International at the Department for Science, Innovation and Technology, told MPs last week that amendments "remain under consideration." That leaves open whether statutory incident‑reporting duties for AI will be written into the bill—or whether the government will pursue alternative regulatory or supervisory routes.
How technologists and security teams, policymakers, and financial firms are likely to respond
- Technologists and security teams: They will face pressure to instrument AI systems to detect, classify and log significant failures and near misses so reports can satisfy FCA expectations. Rusu's remarks imply operational changes to monitoring, incident triage and documentation when systems behave unexpectedly.
- Policymakers and regulators: With Narayan signalling cross‑Parliament and technical engagement and Jones saying amendments to the Cyber Security and Resilience Bill remain under consideration, regulators and ministers will need to agree whether to pursue statutory reporting requirements, sectoral guidance, or a hybrid approach that leaves specifics to supervisory practice.
- Financial firms and sector leaders: The sector's size—£223.6 billion contributed to the UK economy in 2025, or 8 percent of national output, and the fourth‑highest share among OECD countries—means firms will be scrutinised for how they govern increasingly autonomous systems. The House of Commons Treasury Committee's January call for stress tests to assess readiness for AI‑driven market shocks also signals expectations for proactive testing and clear lines of accountability where AI systems produce harmful or unfair outcomes.
The conversation mapped out by the FCA, the AI minister and expert witnesses leaves two concrete tensions visible: firms already subject to major‑incident reporting will be asked to broaden what they consider reportable as AI autonomy rises, and lawmakers have not yet decided whether to enshrine AI‑specific duties into the Cyber Security and Resilience Bill. With the UK financial sector measured in hundreds of billions of pounds and regulators warning of speed‑and‑scale failures, the next steps will test whether policy, supervision and engineering can move in step to capture near misses before they become crises.