Tag: vulnerability patch
6 articles
BIND 9 Update Fixes 14 Flaws, Including Unauthenticated Crashes
The Internet Systems Consortium has rolled out a crucial BIND 9 update that patches 14 security flaws, including unauthenticated crashes, to keep your DNS server safe and secure. Fortunately, no active exploits have been reported so far, but it's still essential to update to the latest releases: BIND 9.20.29, BIND 9.21.26, or BIND 9.20.29-S1 to fix the vulnerabilities.
PostgreSQL Patches 12-Year-Old Flaw Enabling Code Execution
A 12-year-old flaw in PostgreSQL, just patched, allowed replication users to execute arbitrary code on the database server, posing a significant security risk. The vulnerability, tracked as CVE-2026-6471, was exploitable by accounts with the REPLICATION attribute and has been fixed in releases 18.6, 17.11, 16.15, 15.19, and 14.24.
Thermo Fisher Fixes Flaw Enabling Near-Undetectable DNA File Tampering
Thermo Fisher Scientific has patched a high-severity vulnerability in its Applied Biosystems human identification software that could have allowed nearly undetectable DNA file tampering, giving users a false sense of security. The company has implemented digital signatures to ensure data files remain authentic and trustworthy.
Zimbra Fixes Command Injection Flaw, Four XSS Bugs
Zimbra has patched a critical command injection flaw and four cross-site scripting bugs in its latest update, ensuring users are protected from potential security threats. The fixes, part of version 10.1.20, address vulnerabilities that could allow malicious commands to be executed or sensitive data to be compromised.
7-Zip Patches RCE Flaw in XZ-Compressed Data Handling
Don't risk your files! 7-Zip's latest update, version 26.02, patches a critical vulnerability that could let hackers take control when you open a malicious archive.
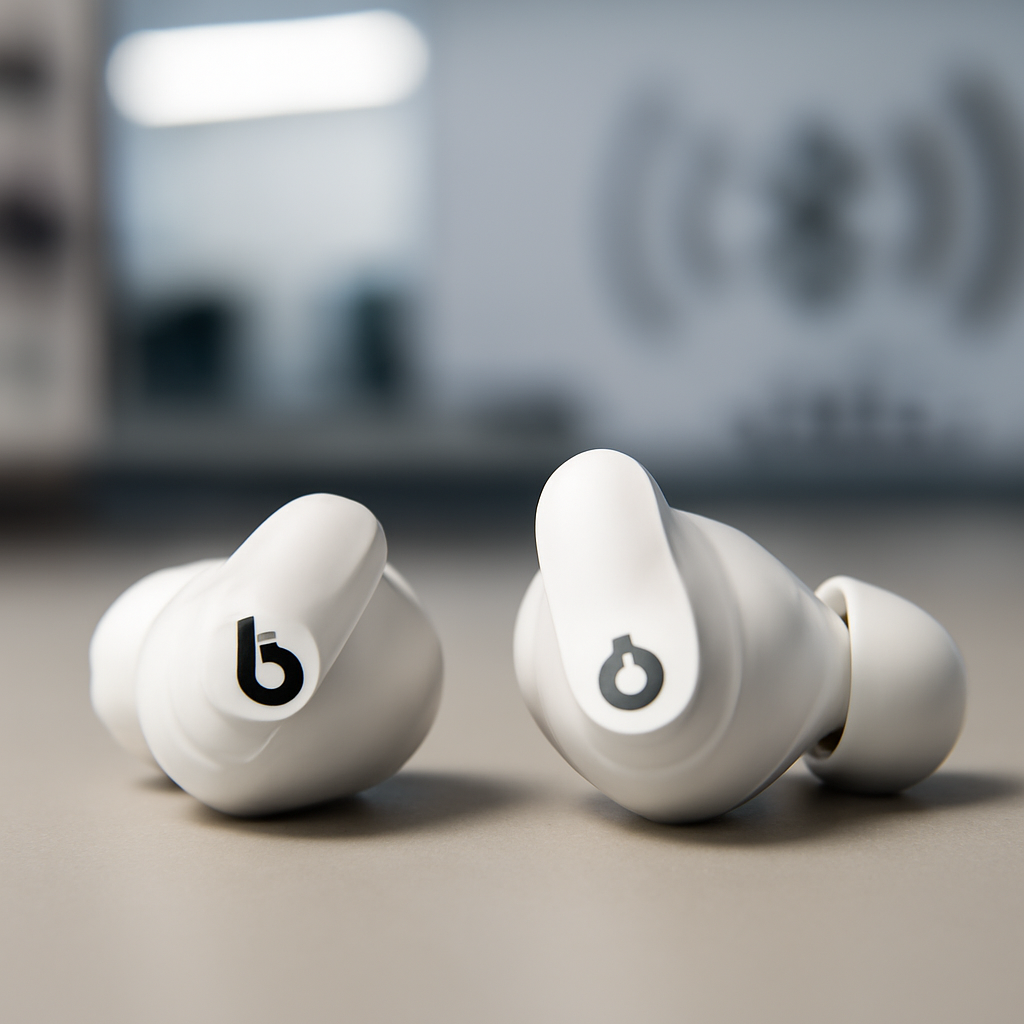
Apple patches Beats Studio Buds flaw that allowed eavesdropping via Bluetooth
Apple just patched a major flaw in its Beats Studio Buds that allowed hackers within Bluetooth range to eavesdrop on conversations through the earbuds' microphone, even if they weren't paired with the device. The company has released a security update, Beats Firmware Update 1B211, to fix the issue.