Tag: threat intelligence
491 articles

Bitdefender Exposes Hidden Attack Surface in Trusted Tools
Did you know that 84% of high-severity incidents involve the abuse of trusted tools, making them nearly invisible to traditional security measures? This shocking statistic highlights the alarming ease with which attackers can hide in plain sight, using legitimate tools against you.
AI-Developed Zero-Day Exploit Exposes New Threats
Google's discovery of the first AI-generated zero-day exploit is a game-changer, revealing a new level of threat sophistication. This historic finding shows that AI can now be used not just to identify vulnerabilities, but to create and deploy malicious code.

Remediation Programs Often Fail to Validate Fixes
The alarming truth is that remediation programs often fall short, with a staggering mismatch between the speed of exploits and fixes - Mandiant's report reveals a mean time to exploit of just -7 days, while Verizon's data shows a median remediation time of 32 days.
Google Exposes AI-Built Zero-Day Threat That Nearly Sparked Mass Attack
The game-changing moment came when a zero-day threat, nearly sparking a mass attack, was uncovered - and forensic evidence revealed its exploit code was astonishingly built by an AI model. This breakthrough highlights how AI is revolutionizing exploit development, making it faster and more accessible to malicious actors.
Security Teams Overlook AI-Driven Threats in Cloud Risk Management
Stay ahead of the threats: are you managing cloud risk effectively, or is it still siloed and vulnerable to AI-driven attacks? Recent research from Google Threat Intelligence Group reveals a new wave of AI-augmented operations that are scaling and accelerating compromises.

Gentlemen Ransomware Group Hit by Data Breach
A recent data breach has exposed the inner workings of the notorious Gentlemen ransomware group, revealing a treasure trove of sensitive information, including chats, images, and operational practices. This rare glimpse into the ransomware ecosystem could provide valuable insights for cybersecurity experts and researchers.
Malware Exploits Chromium Interface to Steal Dev Secrets
Malware is masquerading as a legitimate software installer, tricking developers into spilling their secrets by exploiting the Chromium interface. A simple search ad has become the conduit for this malicious campaign, leading unsuspecting devs down a path of deceit.

Threat Actors Leverage AI for Vulnerability Exploitation and Cyber Operations
Google Threat Intelligence Group has spotted a threat actor using a zero-day exploit likely developed with AI, marking a chilling new trend in cybercrime. This game-changing tactic turbocharges exploit development, malware autonomy, and access to premium AI services.
Hackers Leverage AI to Develop Zero-Day Vulnerability
The AI vulnerability race is no longer on the horizon - it's already underway, with hackers leveraging AI to identify and exploit zero-day vulnerabilities, as seen in a recent coordinated operation. Google Threat Intelligence Group has uncovered the first observed case of cybercriminals using AI to produce weaponized code and bypass security protections.
Google Exposes AI-Generated Zero-Day Exploit Used by Hackers
Google's Threat Intelligence Group has made a groundbreaking discovery - a zero-day exploit, potentially crafted with AI, was used by hackers to bypass two-factor authentication in a widely-used open-source tool. This alarming finding highlights the emerging threat of AI-generated cyber attacks.

Autonomous Teaming Closes Defenders' Speed Gap
The alarmingly rapid pace of cyber threats has left defenders scrambling to keep up, with the time from vulnerability disclosure to working exploit dwindling from 56 days in 2024 to a staggering 10 hours in 2026. Meanwhile, defenders are still stuck on human time, struggling to match the lightning-fast speed of attackers who now operate in seconds.

AI-Driven Attacks Infiltrate Cloud Environments, Exposing Hidden Risks
New AI-driven threats are rapidly exploiting cloud security gaps, making it vital for teams to adopt a proactive, holistic approach to risk reduction to safeguard critical assets and data. Stay ahead of adversaries by understanding how they're weaponizing cloud vulnerabilities at alarming speed.
Vulnerabilities Surge as Exploit Kits Expand in Q1 2026
The Q1 2026 report reveals a concerning surge in vulnerabilities and exploit kits, with attackers increasingly targeting Microsoft Office and Windows with new logic-flaw exploits. This quarter saw a notable rise in security-feature bypasses, including CVE-2026-21509 and CVE-2026-21514, which allow specially crafted files to execute commands with user privileges.
Australia's Security Architecture Needs Diversity to Counter Complex Threats
Australia's national security ecosystem is drowning in data, but struggling to cut through complexity - and simply adding more information can make things worse, not better. To stay ahead of evolving threats, its security architecture needs a fresh approach that prioritises what matters most.
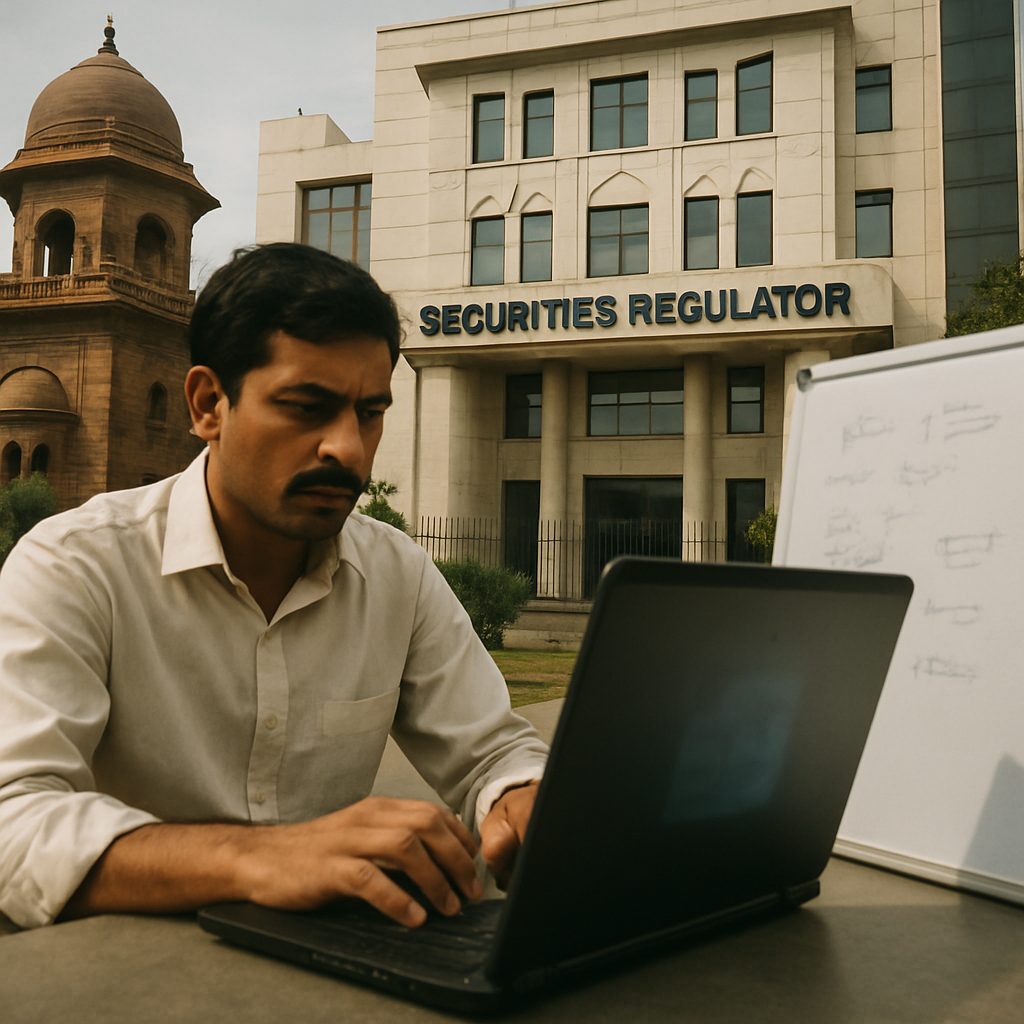
India Issues Infosec Alert as Mythos Threat Looms
India's securities regulator is sounding the alarm on a looming cybersecurity threat, warning market players to bolster their defenses and get ahead of AI-powered attacks. With the Mythos threat on the horizon, it's crucial to develop new strategies and solidify cyber-basics to stay safe.
AI-Driven Attacks Infiltrate Cloud Environments
Stay ahead of the threats: as AI-driven attacks infiltrate cloud environments, it's crucial to adopt a proactive, holistic approach to risk reduction and protect your critical assets and data. Google Cloud and XM Cyber warn that understanding how attackers move laterally throughout your network is key to safeguarding against emerging AI-driven threats.

Criminal IP Enhances ThreatQ with Real-Time Exposure Intelligence
Criminal IP's integration with ThreatQ supercharges threat intelligence by delivering real-time exposure insights, empowering organizations to analyze and respond to threats faster and more effectively. Analysts can now access crucial IP intelligence directly within ThreatQ, streamlining investigations and threat validation.
Phishing campaigns increasingly harness AI to evade detection
Phishing campaigns are getting smarter by the minute, with a whopping 86% of recent attempts leveraging AI to sneak past detection. This marks a significant jump from just two years ago, when AI was used in 80% of phishing ops.
Phishing Kit Bluekit Incorporates AI to Streamline Attacks
Meet Bluekit, a cutting-edge phishing kit that's revolutionizing the game with an AI Assistant panel, pairing traditional templates with advanced AI models to help cybercriminals quickly draft campaign materials. This innovative tool is streamlining attacks, making it easier for malicious actors to launch sophisticated phishing campaigns.
AI-Driven Cybercrime Fuels 389% Surge in Ransomware Victims
Get ready for a wake-up call: ransomware victims have skyrocketed by 389% in just one year, thanks to cybercriminals harnessing the power of AI to launch more sophisticated attacks. This alarming trend is driven by the growing availability of malicious AI tools, making it easier for hackers to wreak havoc.

Attackers Target New Assets Within Minutes of Exposure
The moment a new asset goes live with a public IP address, the clock starts ticking - and within minutes, attackers are circling, waiting to pounce on unsuspecting targets. In just 24 hours, a newly exposed asset can go from discovery to compromise, with threat actors exploiting vulnerabilities at an alarming rate.
Cybercriminals Exploit 2.9 Billion Compromised Credentials
Imagine 2.9 billion personal login details floating around in the dark corners of the internet, vulnerable to exploitation by cybercriminals - that's the staggering reality revealed by a recent threat intelligence analysis. This massive cache of compromised credentials, tracked globally in 2025, is a goldmine for hackers leveraging stolen logins, malware, and AI to wreak havoc.
Anthropic's AI Model Exposes New Vulnerability Risks
Anthropic's new AI model, Claude Mythos Preview, has sent shockwaves through the internet security community by autonomously discovering and exploiting software vulnerabilities that even thousands of expert developers missed. This powerful tool is being cautiously released to a select few, leaving many to wonder about the implications of its capabilities.
AI Accelerates Exploits, Forces New Breach Playbooks
The game-changing capabilities of AI models like Anthropic's Claude Mythos have drastically shrunk the exploit window, allowing them to uncover vulnerabilities in minutes that would take human experts weeks or even hours to detect. This seismic shift is forcing organizations to rethink their approach to vulnerability management and incident response.