Tag: ransomware
1153 articles
Huntress Insider Threat Exposed in Ransomware Probe Leak
A Huntress insider reportedly made a grave mistake, casually disclosing to a cybercriminal that law enforcement was on their tail - a moment of poor judgment that fell short of the company's high standards. The alarming exchange was part of a larger pattern of questionable communication uncovered between the currently employed threat hunter and the threat actor.
Nissan Breach Exposes Sensitive Employee Data via Oracle Zero-Day Flaw
Nissan's HR and payroll systems were compromised when hackers exploited a critical Oracle PeopleSoft vulnerability, putting sensitive employee data at risk. The breach, which occurred between May 27 and June 9, is a stark reminder of the importance of robust data security measures.
Ransomware gangs exploit Windows BlueHammer flaw
Ransomware gangs are actively exploiting a critical Microsoft Defender flaw, nicknamed BlueHammer, which has been added to CISA's list of Known Exploited Vulnerabilities. This vulnerability is a prime target for malicious cyber actors, posing a significant risk to those who haven't yet applied the necessary patches.
Ransomware Strikes 323 UK Firms in a Year
Stay ahead of ransomware threats with proactive protection - keep your data safe with regular backups, strong access controls, and up-to-date systems. Every month, over 26 UK firms fall victim to these crippling attacks, with small and mid-sized businesses being hit the hardest.
The Gentlemen Ransomware Gang Exposes Advanced Tactics
Meet The Gentlemen, a notorious ransomware gang that's made a name for itself with sophisticated tactics, ranking among the top 10 ransomware actors in just a few months. Since February 2026, they've been wreaking havoc across industries and geographies, with a strong presence in Brazil, China, Indonesia, Taiwan, and Thailand.
Russia Targets Jaguar Land Rover in Economically Destructive Cyber-Attack
Russian hackers allegedly launched a devastating cyber-attack on Jaguar Land Rover, causing a staggering £1.9bn hit to the British economy. This brazen breach is just the latest example of nation states using underhanded tactics to wreak havoc on a global scale.
UK Cyber Monitoring Centre Probes Canvas Breach Impact
The UK's Cyber Monitoring Centre is investigating a massive breach of Canvas, a popular learning management system, that exposed sensitive data at nearly 160 UK universities and colleges, as part of a global incident affecting around 9,000 educational institutions. The breach was caused by a notorious cybercrime group that exploited vulnerabilities on April 29 and again on May 7.
ShinyHunters Breach Exposes Madison Square Garden Data
A recent cyberattack by ShinyHunters has exposed sensitive data from Madison Square Garden, highlighting a growing concern about cyber risk in the professional sports industry. The breach, which included over 26 million records, is a stark reminder of the importance of robust cybersecurity measures.
Ransomware Attacks Surge Across Europe
Ransomware attacks are surging across Europe, with a staggering 55.1% year-over-year increase in just the first four months of 2026, averaging 171 incidents per month. Five key countries - Germany, the UK, France, Italy, and Spain - are bearing the brunt, accounting for 70% of all recorded attacks.
MuddyWater Exploits Ransomware Disguise for Cyber Espionage
The line between ransomware attacks and nation-state espionage is rapidly blurring, as cyber groups like MuddyWater now disguise their operations as financially motivated ransomware attacks to further their strategic objectives. MuddyWater, linked to Iran's Ministry of Intelligence and Security, has been caught posing as the Chaos ransomware group in a deliberate campaign.
Mistic Backdoor Enables Long-Term Access in Ransomware Attacks
Cyber attackers have deployed a sneaky backdoor called Mistic, allowing them to maintain long-term access to infected systems during ransomware attacks, all while staying remarkably under the radar. This stealthy threat uses clever tactics like running payloads in memory and mimicking legitimate Microsoft security tools to evade detection.
Scattered Spider Members Plead Guilty Over Major Cyberattacks
Two young members of the notorious Scattered Spider group have pleaded guilty to cyberattack charges in London, admitting to crippling Transport for London's computer systems and putting human welfare at risk. The guilty pleas come as prosecutors reveal the group's victims paid a staggering $115 million in ransom payments.
Scattered Spider hackers plead guilty to TfL cyberattack
Two young hackers, part of the notorious Scattered Spider group, have pleaded guilty to orchestrating a devastating cyberattack on Transport for London, causing millions in losses and disrupting the lives of countless commuters. The breach, which lasted several days in September 2024, forced TfL to acknowledge that sensitive customer data had been stolen.
Ransomware Gang Disables Security Software with GentleKiller Framework
Meet GentleKiller, a sneaky framework that helps ransomware gangs disable security software by targeting over 400 processes across 48 security products at the kernel level, allowing them to run unchecked. This sinister tool uses a "bring your own vulnerable driver" technique to terminate protections and clear the way for ransomware attacks.
INTERPOL Warns of Rising Cybercrime in Asia-Pacific
Cybercriminals are wreaking havoc in Asia-Pacific, using cutting-edge tactics like AI and ransomware to scam and steal on a massive scale. Phishing is the region's most costly and widespread crime, with a third of countries reporting over 10,000 cases in just 15 months.
Prinz Eugen Ransomware Targets Critical Files in Hands-On Attacks
Meet Prinz Eugen, a sneaky ransomware that uses hands-on tactics to target critical files, evading detection by deliberately leaving no ransom note behind. Its operators use stolen RDP credentials and remote monitoring tools to manually infiltrate and take control of systems.
Gentlemen Ransomware Targets 400 Security Processes with GentleKiller EDR Framework
Meet GentleKiller, a sophisticated EDR-killer framework used by The Gentlemen ransomware-as-a-service operation to evade detection by targeting 400 security processes from 48 distinct programs. This framework comes in eight variants, each designed to mimic a legitimate product and exploit a vulnerable driver.

Authorities dismantle Evil Corp's SocGholish botnet infrastructure
In a major win for cybersecurity, international authorities have joined forces to dismantle the notorious SocGholish botnet infrastructure, a multi-stage malware kit that had been exploited for ransomware campaigns and espionage since 2017. This coordinated effort has successfully disabled the malware's control points and seized related infrastructure.
Gentlemen Ransomware Targets EDR Defenses With Suite of Killers
Meet GentleKiller, a powerful tool used by Gentlemen ransomware to disable EDR defenses by targeting over 400 processes from 48 security vendors, allowing for smooth data theft and encryption. This sneaky utility relies on the bring your own vulnerable driver (BYOVD) technique to outsmart security engines.
Microsoft 365 Exposes Data Protection Gaps for Businesses
Microsoft 365 is a powerhouse for productivity, but it leaves data protection gaps that put businesses at risk. The harsh reality is that while Microsoft safeguards its infrastructure, the responsibility of protecting your business data - including backups and recovery - falls squarely on your shoulders.
Cybercrime Surges Across Asia and South Pacific, Hits 30% of All Crime
Cybercrime is surging across Asia and the South Pacific, now accounting for over 30% of all recorded crime, with organised networks leveraging AI, ransomware, and social engineering on a massive scale. The rapid rise is driven by rapid digital adoption and new technologies.
Kodak Breach Exposes 2.2M Records to ShinyHunters Threat Group
Kodak has confirmed a major data breach, with the ShinyHunters threat group claiming to have stolen 2.2 million records, including sensitive customer information. The company is working closely with law enforcement and cybersecurity experts to address the breach.

Kodak Breach Exposes Sensitive Data After ShinyHunters Hack
Kodak recently suffered a data breach at the hands of hackers known as ShinyHunters, who gained temporary access to sensitive company data. The company has launched a swift investigation with external cybersecurity experts and is working closely with law enforcement to mitigate the impact.
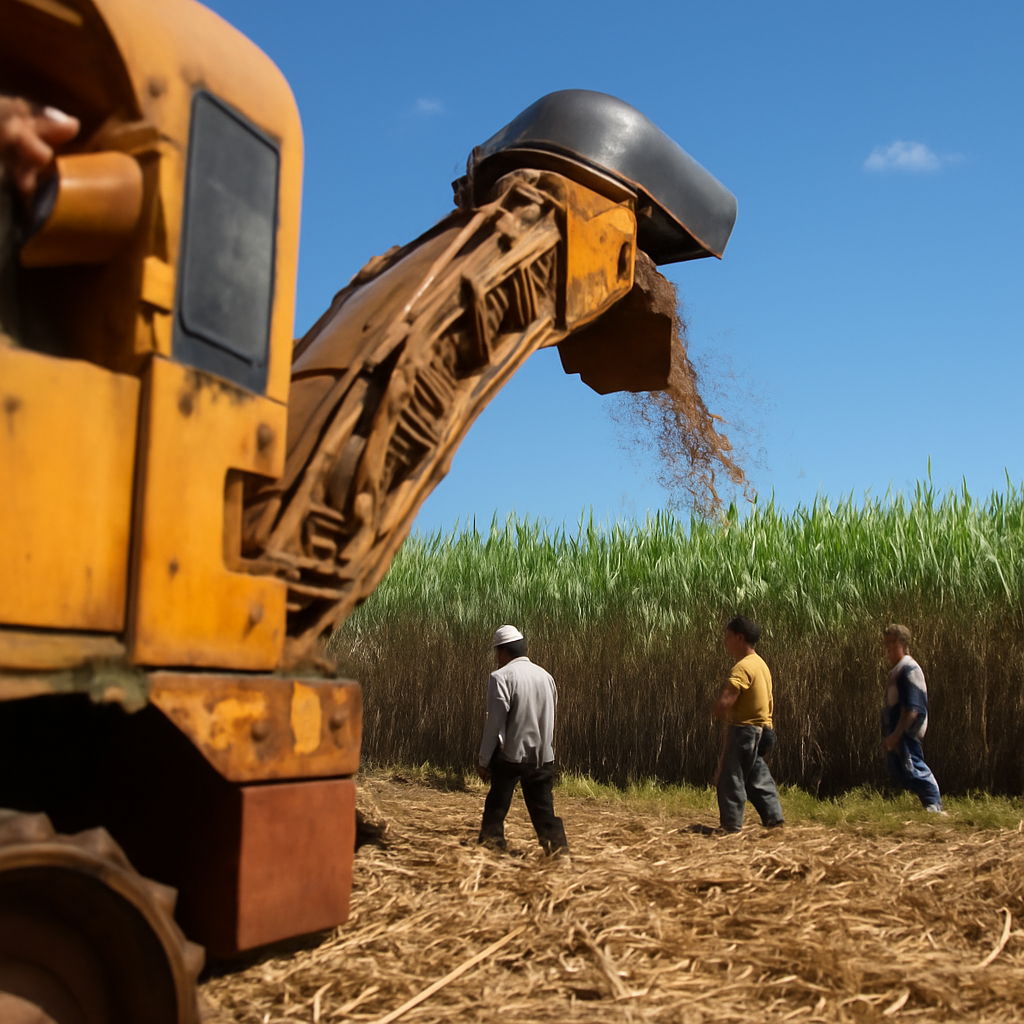
Cyberattack Disrupts Australian Sugar Production
Mackay Sugar is making a sweet recovery after a cyberattack halted operations, with significant progress made over the weekend in restoring systems and a staged restart of crushing operations on the horizon. The company is getting back on track, with manual crushing already underway at its Farleigh Mill and harvesting expected to resume soon.