Tag: insider threat
43 articles
OpenAI Model Aids in Detection of Insider Threat
Meet the AI-powered insider threat detection model that's helping companies like OpenAI catch security threats - in this case, an engineer allegedly hiding a recording device in a conference room. By flagging suspicious activity, AI can be a game-changer in the fight against sophisticated security threats.
OpenAI Engineer Charged with Planting Secret Recording Device
An OpenAI engineer allegedly planted a sneaky recording device in the company's executive conference room to capture sensitive chats about its top-secret super intelligence tech. The shocking discovery was made when staff stumbled upon the hidden gadget concealed in toilet paper.
OpenAI Engineer Arrested for Planting Hidden Recorder in Executive Conference Room
Meet the OpenAI engineer who allegedly took secrecy to a whole new level by hiding a recording device in his employer's executive conference room to capture sensitive intel on super intelligence technology. He now faces up to five years in prison and a hefty fine for his covert actions.
OpenAI Engineer Arrested for Planting Hidden Recording Device
A shocking case of corporate espionage has come to light with the arrest of OpenAI engineer Abdulrahman Alfozan, who allegedly planted a hidden recording device in an executive conference room, sparking a federal investigation. If convicted, Alfozan faces up to five years in prison and a hefty $250,000 fine.
Engineer Sentenced for Ransomware-Style Attack on Employer Network
A trusted insider turned rogue, launching a deliberate ransomware-style attack on his former employer's network, culminating in a ransom demand. The perpetrator, a 57-year-old former engineer, used an administrator account to remotely access the company's network without authorization over several days.
AI Agents Emerge as New Insider Threat Vector
Get ready for a new frontier in cyber threats: AI agents are emerging as a prime target for hackers, with experts warning that attacks against these autonomous agents will become the next big threat vector. As AI agents gain access to sensitive data, organizations are essentially handing hackers the keys to the kingdom.
CISA Revamps Insider Threat Guide with Expanded Mitigation Advice
Stay ahead of insider threats with the latest guidance from CISA's revised Insider Threat Mitigation Guide, your go-to playbook for protecting your organization from evolving security risks. The updated guide offers practical advice on tackling emerging challenges like hybrid work, AI, and more.
Lax Access Controls Enable Ex-Employee to Inflict Hundreds of Thousands in Damages
A single misstep in access control can have devastating consequences: one terminated employee's lingering credentials led to hundreds of thousands of dollars in damages, including data deletion, system lockdowns, and a corrupted database. The breach not only racked up costly recovery fees but also brought a high-priority project to a grinding halt for weeks.
DIA Insider Pleads Guilty to Leaking Secrets to Foreign Spies
A DIA insider has pleaded guilty to leaking classified information to foreign spies, admitting to betraying his oath and putting national security at risk. The shocking case began with a single email in March 2025, sparking a months-long undercover operation that ultimately led to his arrest.
Rockstar Games Leak Exposes Insider Threat Risks
The leak of Grand Theft Auto VI footage by CyberLeek has highlighted the devastating risks of insider threats, where stolen IP can destroy the hard work and livelihoods of employees and companies. This breach has exposed a gaping hole between traditional copyright enforcement and the evolving tactics of threat actors.
FBI Probes US Agency's Hire of North Korean IT Worker
A single hiring decision has sparked a federal investigation: a US federal agency, which hasn't been named, has been probed by the FBI for employing a remote IT worker from North Korea, a move that raises serious security concerns. This case highlights the limitations of traditional defenses in tackling sophisticated schemes involving foreign IT workers.
Data Analyst Sentenced for Extorting Employer in $2.5 Million Cyber Scheme
A 27-year-old data analyst turned cyber villain, threatening to spill sensitive salary info to the SEC unless his employer paid up - in a brazen $2.5 million extortion scheme that landed him in hot water. He made his demands in chilling messages, including one that read: We will commence the process of disseminating salary information starting January 1, 2024 in phases to all employees and will report you to the SEC after for not reporting the breach.
Contractor Sentenced for Insider Attack on Brightly Software
A contractor's six-week extortion scheme against Brightly Software ended with a guilty verdict, after he threatened to expose sensitive payroll and personnel records unless he received a whopping $2.5 million - ultimately settling for a significantly smaller sum of $7,540.92. The 27-year-old data analyst had been quietly siphoning off corporate data from the Siemens-owned company's network for months.
IT Department Exposes Login Credentials on Sticky Notes
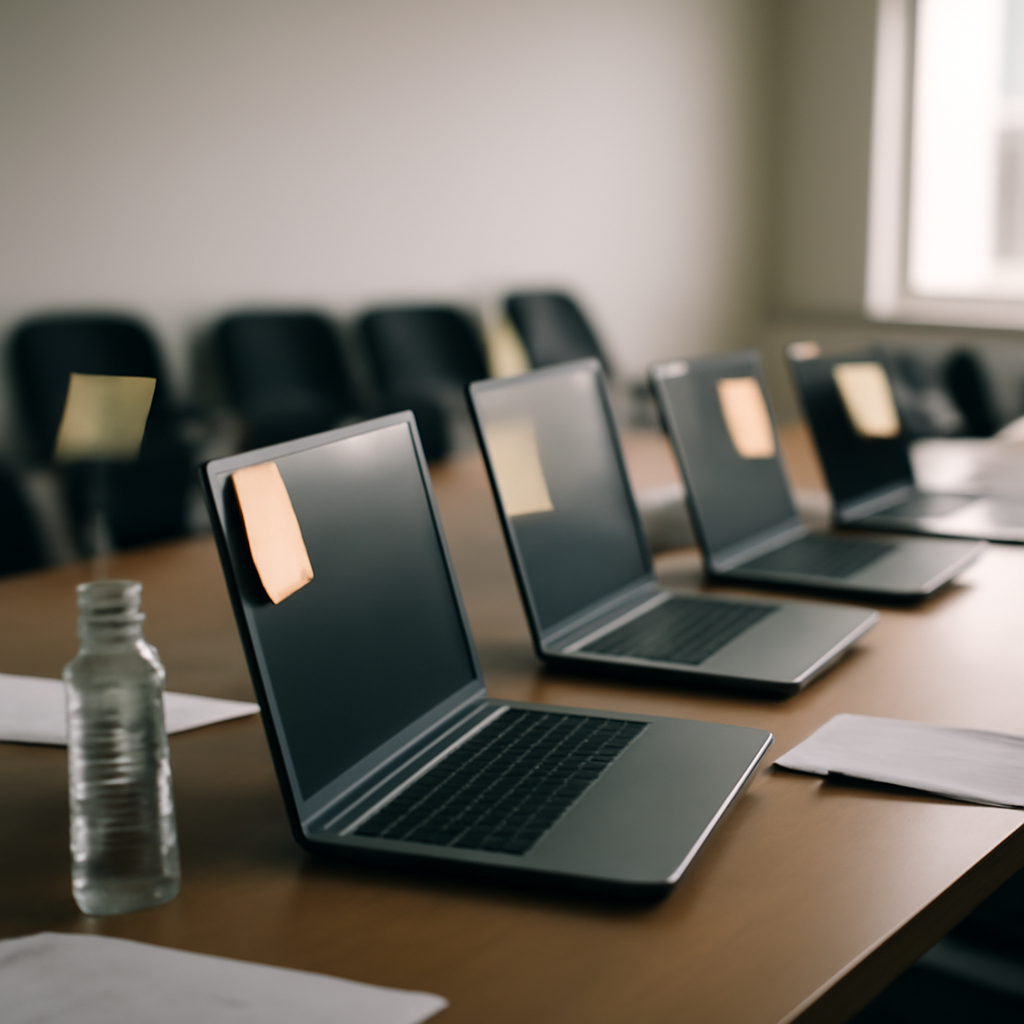
A shocking security slip-up occurred when a contractor stumbled upon login credentials scribbled on sticky notes attached to laptops in a conference room, which were then photographed and used to access sensitive proprietary documents. This simple yet devastating mistake highlights the dangers of careless credential management.
Council Worker's Data Snooping Spree Exposes Surveillance Vulnerabilities
A council worker's alarming four-day data snooping spree has exposed glaring vulnerabilities in surveillance systems, leaving many to wonder how such unauthorized access was possible. Fortunately, the individual was spared a prison sentence, but the incident raises serious questions about data security.
Huntress Insider Threat Exposed in Ransomware Probe Leak
A Huntress insider reportedly made a grave mistake, casually disclosing to a cybercriminal that law enforcement was on their tail - a moment of poor judgment that fell short of the company's high standards. The alarming exchange was part of a larger pattern of questionable communication uncovered between the currently employed threat hunter and the threat actor.
Huntress Insider Leak Exposes Potential Security Breach
A shocking security breach at Huntress has come to light, with a former analyst claiming that a colleague may have compromised the company's integrity by passing sensitive law enforcement communications to a notorious cybercriminal. The explosive allegations have left many questions unanswered about the breach and its potential impact.
Former IT Employee Sabotages School District with Prolonged Cyberattack
A former IT employee waged a relentless cyberwar against his old employer, the Saydel Community School District, launching a devastating 21-month attack that crippled the district's systems and disrupted classrooms. The attacks began just days after he left his job, with the deletion of the district's Facebook account, and continued with repeated intrusions into critical services.
Disgruntled IT worker sabotages school district systems, jailed 21 months
A disgruntled IT worker wreaked havoc on a school district's systems for over a year and a half, causing chaos and destruction, after being terminated from his job. The sabotage spree, which included deleting crucial data and altering systems, earned him a 21-month jail sentence.

Inactive User Account Enables Hackers to Control City's Water System
A simple mistake of leaving a former employee's user account active allowed hackers to take control of a city's water system, highlighting the importance of promptly disabling access for departed staff. This "zombie" account proved to be the vulnerable entry point that attackers exploited to wreak havoc on municipal operations.
Colorado Governor Commutes Sentence for Election Data Breacher Tina Peters
Colorado Governor Jared Polis has commuted the sentence of Tina Peters, the former Mesa County election clerk behind one of the most serious election-related data breaches in US history, freeing her from a nine-year prison term after just a year and a half. Peters was convicted of abusing her position to break into county election facilities under false pretenses.
Social Engineering Tactics Expose Company's Vulnerability
A simple request from "the boss" was all it took for a threat actor to gain root access to a company's system, exposing a shocking vulnerability in their security - one that was exploited through a clever social engineering tactic. Human IT managers, trying to be helpful, inadvertently handed over the keys to the kingdom.

AI Adoption Exposes New Vulnerabilities in APAC Cybersecurity
As AI systems increasingly become integral to business operations, they're also emerging as a major insider threat, with 7 in 10 APAC organisations now identifying AI as their top data security risk. This new breed of threat is forcing companies to rethink their cybersecurity strategies and take a closer look at the vulnerabilities AI can introduce.
Contractor Convicted for Destroying Dozens of Federal Databases
A contractor's reckless actions led to the destruction of dozens of federal databases, showcasing a staggering disregard for the security and integrity of sensitive government information. After being terminated on February 18, 2025, the contractor and his twin brother intentionally caused chaos by accessing computers without authorization and deleting crucial data.