Tag: emerging threats
8360 articles
Cybersecurity's 72-Minute Challenge
The clock is ticking: in the blink of an eye, just 72 minutes, attackers can breach your defenses and make off with your data, highlighting a daunting speed gap between threat actors and security teams. This alarming acceleration demands a serious rethink of traditional security operations.
Cisco SD-WAN Vulnerability Exploited for Root Access
Cisco has warned of a critical vulnerability in its SD-WAN system that allows attackers to gain root access by sending a malicious HTTP request. This flaw, now patched, could have let hackers create or overwrite files and ultimately elevate their privileges.
US Seizes Deepfake Nude Sites in First TAKE IT DOWN Act Enforcement Action
In a groundbreaking move, the US Department of Homeland Security has seized two notorious deepfake nude sites, CFAKE.com and SOCFAKE.com, in the first-ever enforcement action under the TAKE IT DOWN Act. This bold operation, carried out in collaboration with Italy and France, has taken a significant step towards protecting online victims and holding perpetrators accountable.
Researcher Uncovers Feds' Swift Response to Simple Code Prompt
A researcher discovered that a simple code prompt to "fix this code" sparked a surprisingly swift and alarmed reaction from federal authorities regarding the Fable 5 model. However, the researcher disputes that this incident constituted a jailbreak, downplaying its significance.
Chinese Hackers Exploit Google Workspace to Siphon Research and Defense Emails
Chinese hackers have been secretly siphoning off sensitive emails from research and defense organizations using a clever exploit of Google Workspace, with a long-running campaign that spanned over two years. The threat actors, tracked as UNC6508, used custom malware called INFINITERED to breach externally facing servers and steal valuable intel.
North Korean Hackers Exploit Developer Tools in Malware Campaigns
North Korean hackers have launched a sneaky malware campaign, tricking victims into executing cross-platform malware for macOS, Linux, and Windows through malicious scripts hidden in GitHub repositories. Their latest tactic, dubbed UNK_DeadDrop, uses recruitment lures to deliver self-running code to over 75% of targeted organizations across various sectors.
SimpleHelp vulnerability exposes servers to rogue remote support accounts
A critical vulnerability in SimpleHelp, known as CVE-2026-48558, lets hackers create rogue remote support accounts and gain privileged access to servers, allowing them to execute scripts and wreak havoc on your system. This gaping security hole enables unauthenticated attackers to bypass multi-factor authentication and log in as a Technician user, putting your entire network at risk.
Russian Tu-22M3 Bomber Crashes During Training Flight in Siberia
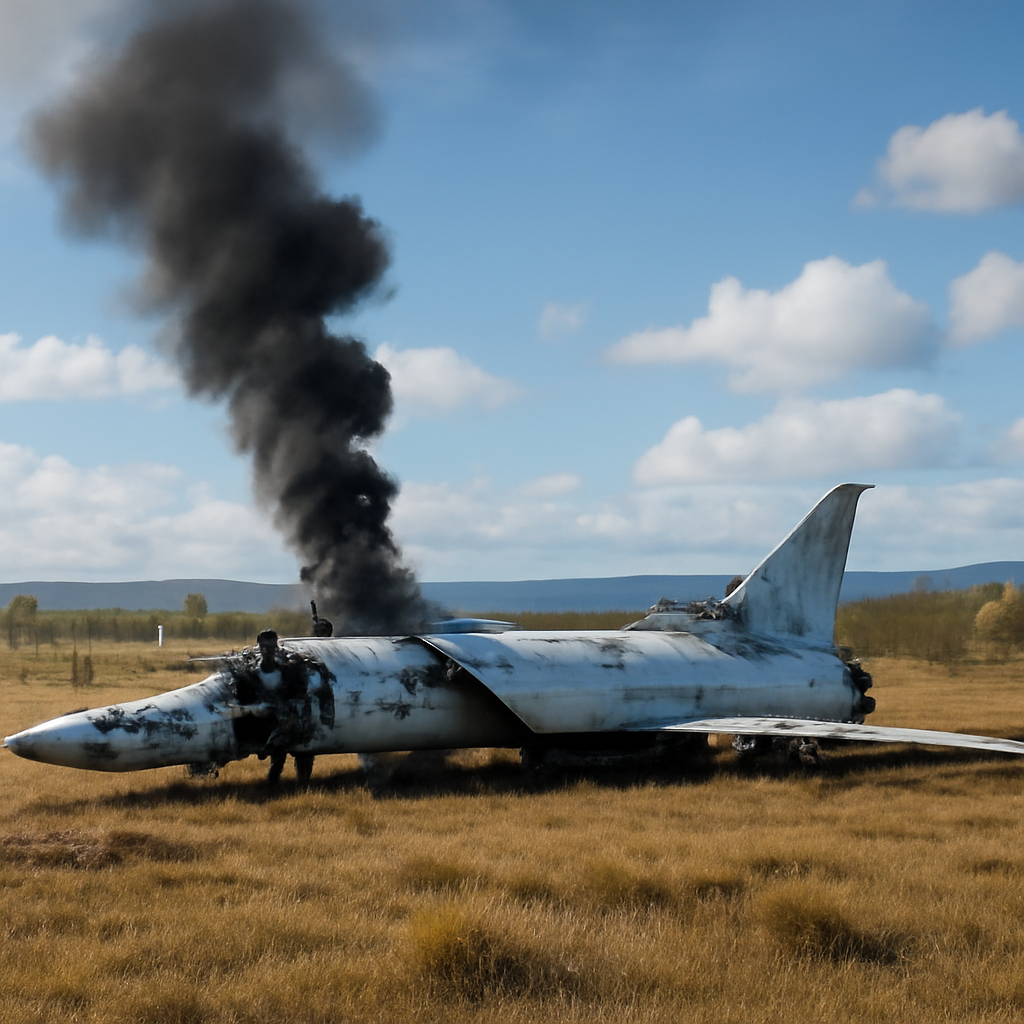
A Russian Tu-22M3 bomber dramatically crashed during a routine training flight in Siberia, with footage showing the aircraft plummeting nose-first into the ground, but thankfully, all crew members ejected safely with no ground casualties. The incident occurred during an approach to land in the Irkutsk region, with the plane not carrying a combat load.
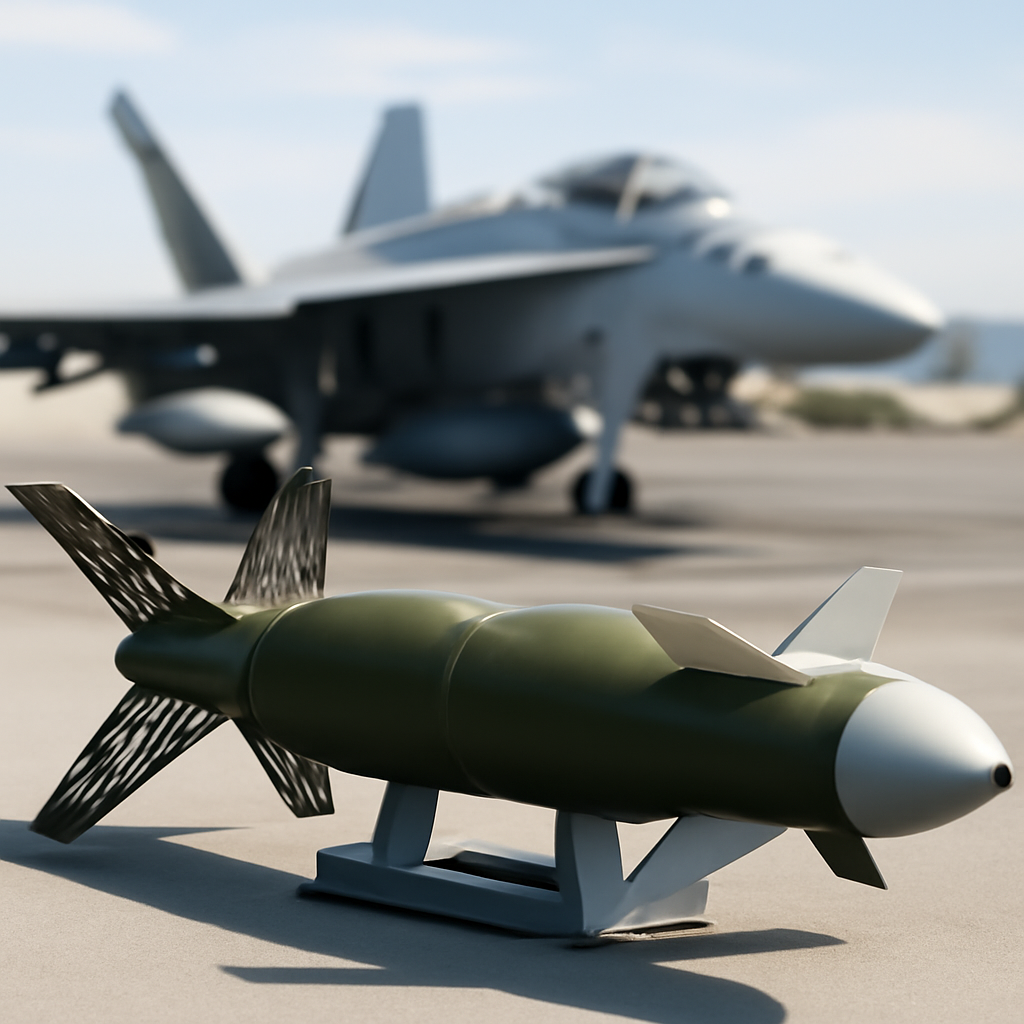
US Military Eyes JDAM-ER for Bunker-Busting Strikes
The US military is exploring the potential of the 2,000-pound Joint Direct Attack Munition Extended Range (JDAM-ER) to take out heavily fortified bunkers and deeply buried targets. The Pentagon is seeking to assess and upgrade the JDAM-ER's capabilities to enhance its bunker-busting abilities.
Experts Dispute White House Move to Restrict AI Model Exports
The government's sudden move to restrict exports of Anthropic's Fable 5 AI model has sparked a heated debate, with experts arguing that such limitations could hinder crucial bug fixes and security patches. By restricting Fable 5, is the White House inadvertently putting innovation and cybersecurity at risk?
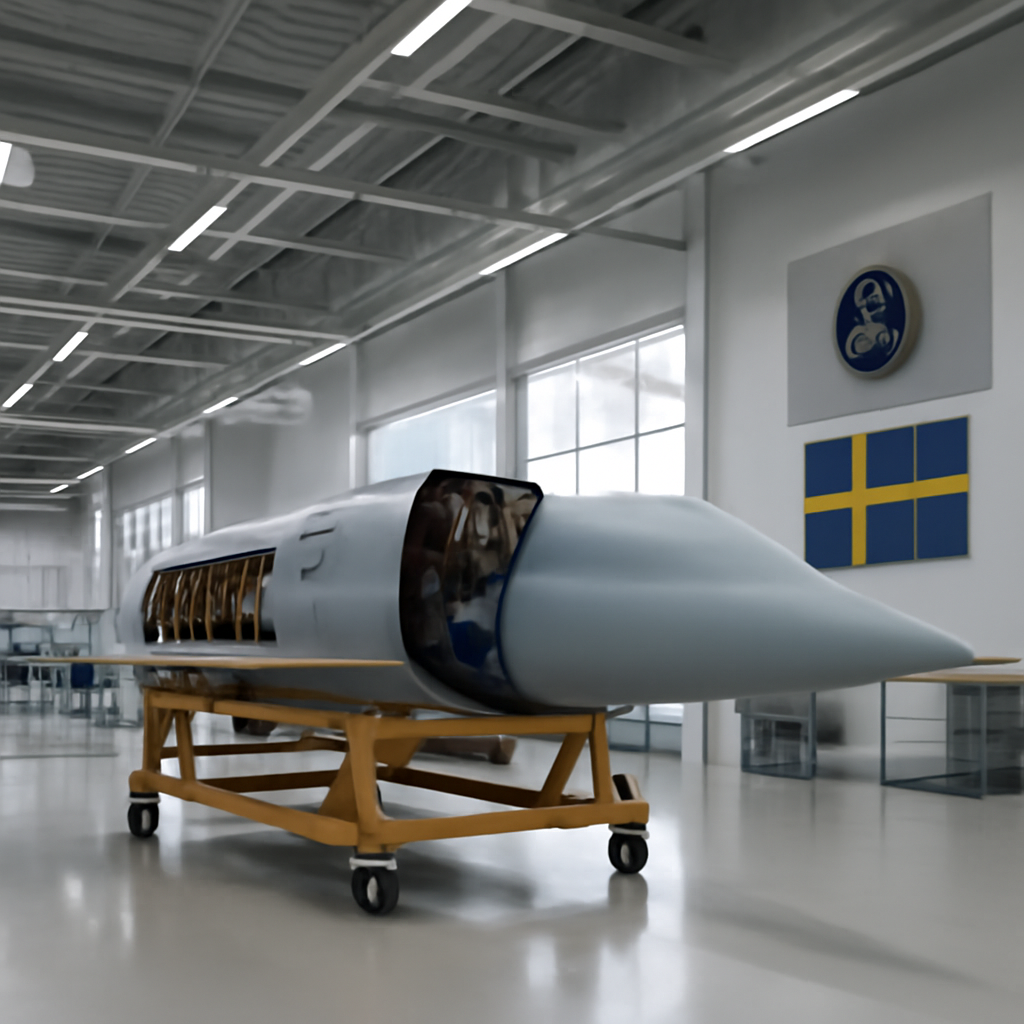
Sweden Weighs State Ownership in Saab Amid Security Concerns
As Sweden's defense landscape evolves, Peter Hultqvist, the country's former defense minister, is open to the idea of the state taking part-ownership in Saab, a move he believes would bolster national security. This potential stake would enable Sweden to protect its core interests in critical defense technologies like submarines, sensors, and fighter aircraft.
China-linked UNC6508 Targets Medical Research Institutions
A sophisticated cyber threat group linked to China, known as UNC6508, has launched a targeted attack on medical research institutions in North America, exploiting vulnerabilities in REDCap servers to gain a foothold. The intrusions, which began in September 2023, aim to compromise sensitive research data.
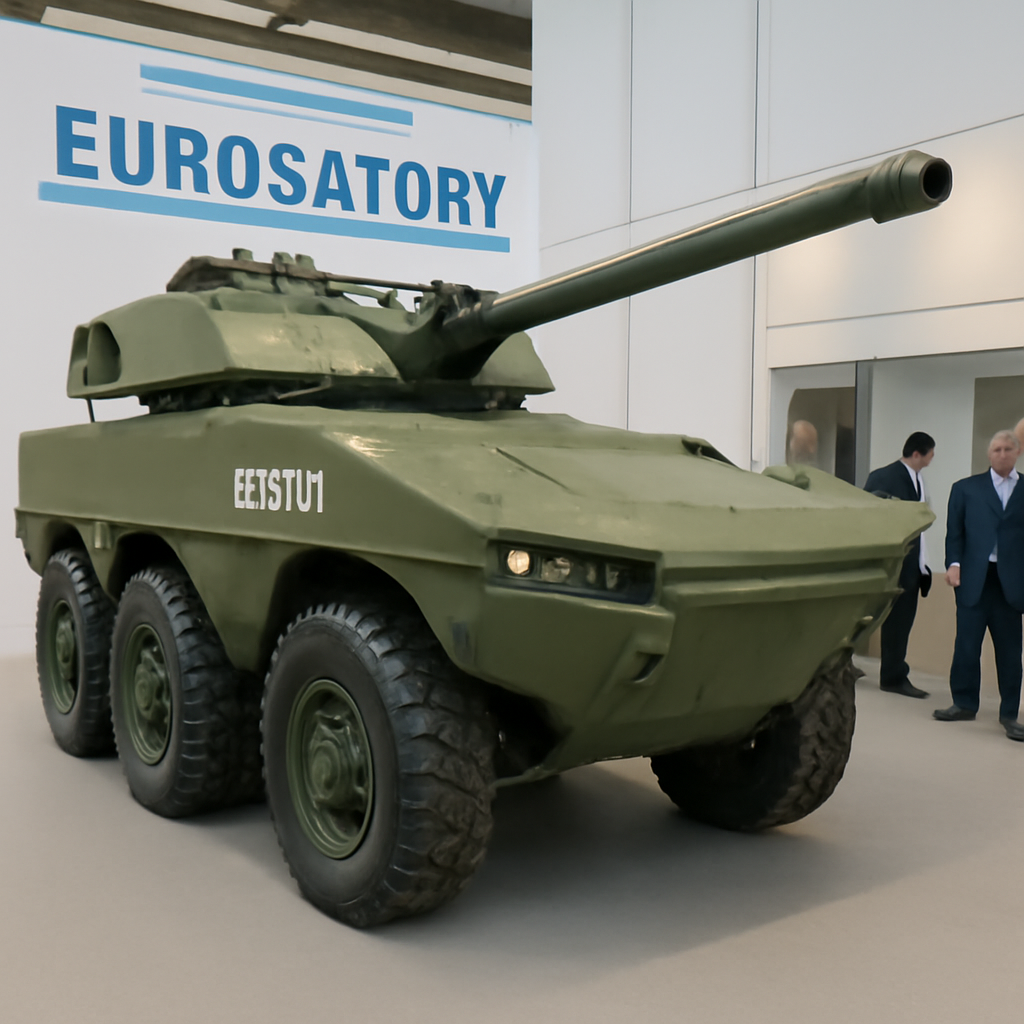
Arquus Unveils Fenris 6×6 Armored Vehicle with 105mm Gun
Meet Fenris, a game-changing 6×6 armored vehicle packing a powerful 105mm gun that can be airlifted, even on an A400M. Developed in just over a year, Fenris is Arquus and John Cockerill Group's rapid response to the renewed need for direct fire support on the battlefield.
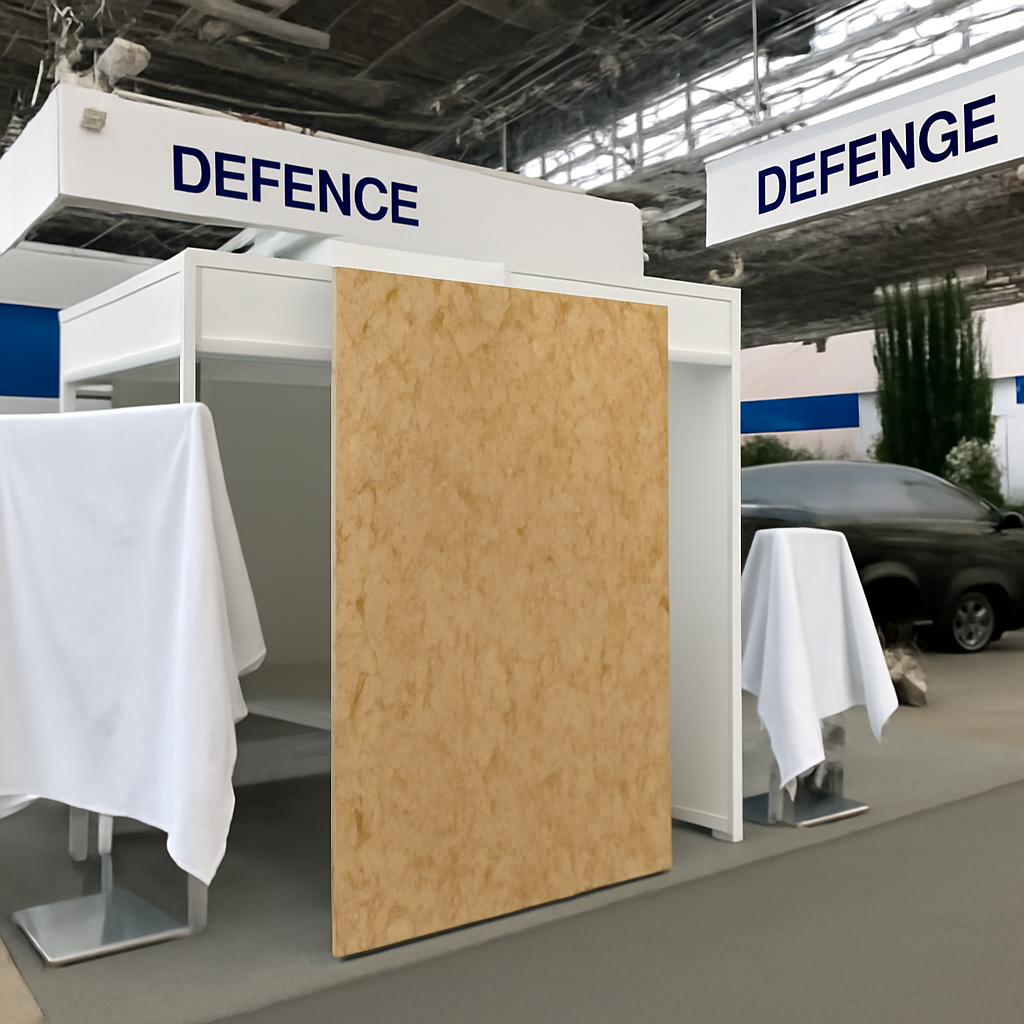
France restricts Israeli defense displays at Eurosatory show
The Eurosatory exhibition took a shocking turn when organizers suddenly boarded up Israeli defense industry pavilions, despite the companies meeting all French government demands and showcasing only defensive systems. The Israeli Ministry of Defense blasted the move as discriminatory and politically motivated.
Federal Agencies Pursue Secure AI With Data Clarity, Infrastructure Overhaul
The harsh reality is that most organizations are flying blind when it comes to their data, with little insight into what they have, where it's stored, or if it's properly secured. This knowledge gap is a major hurdle for federal agencies looking to harness the power of AI while keeping sensitive data safe.
US Agencies Shift Focus to Cyber Resilience
The US Department of Defense is overhauling its cyber defense strategy, shifting towards a holistic approach that emphasizes cyber resilience, enterprise modernization, and operational effectiveness. Chief Information Officer Kirsten Davies is leading the charge, driving practical reforms to boost automation, streamline processes, and strengthen cybersecurity across the department.
OptinMonster Plugin Compromised in Supply-Chain Attack
A critical security breach has hit the popular OptinMonster plugin, used by over 1.2 million websites, which delivered malicious JavaScript to unsuspecting users via a compromised content distribution network. The attack, detected by ecommerce security firm Sansec, injected harmful code into websites for a brief but perilous window of time.
ShinyHunters Breach Council of Europe in Oracle PeopleSoft Heist
The Council of Europe has fallen victim to a massive data breach, with hackers claiming to have stolen a whopping 297 GB of sensitive information, including HR records, payslips, and medical data, by exploiting a zero-day flaw in Oracle PeopleSoft. The ShinyHunters extortion group is behind the breach, boasting a haul of 429,000 files from the attack.
LiteLLM Vulnerability Chain Enables Low-Privilege Server Takeover
A shocking vulnerability chain in LiteLLM has been discovered, allowing hackers to hijack servers with just a low-privilege account, and experts warn it's a critical threat with a near-perfect CVSS score of 9.9. By chaining three distinct bugs, attackers can escalate their access to full admin rights and run code on the server.
Cisco Patches SD-WAN Flaw Exploited in Zero-Day Attacks
Cisco has patched a high-risk SD-WAN flaw, known as CVE-2026-20262, that was being exploited in zero-day attacks to gain root privileges. The vulnerability allowed attackers to create or overwrite files on affected systems, and Cisco has now released security updates to fix the issue.
Anubis Ransomware Targets Adriatic Port, Exposes Maritime Security Gaps
A ransomware attack by the Anubis group on the Adriatic Port Authority exposed significant gaps in maritime security, putting sensitive employee records and critical infrastructure at risk. The breach, which occurred on December 11, 2025, resulted in the loss of around 2% of the authority's data, with some information making its way to the dark web.
US Datacenter Law Set to Lapse, Leaving Security Gaps Unaddressed
As the Federal Data Center Enhancement Act of 2023 lapses on September 30, 2026, a crucial safeguard for secure and reliable access to federal information systems will vanish, leaving gaping security holes unaddressed. Without an extension or replacement, federal data centers may operate with little oversight, putting sensitive information at risk.
Malicious Code Infiltrates WordPress Plugins, Creates Rogue Admin Accounts
Over 1.2 million WordPress sites are at risk after attackers infiltrated a trusted vendor's network, injecting malicious code into popular plugins like OptinMonster, TrustPulse, and PushEngage. This sneaky hack creates rogue admin accounts, putting sites at risk of takeover - all without ordinary visitors even noticing.
Council of Europe Probes ShinyHunters Data Breach Claims
The Council of Europe is actively investigating claims by the ShinyHunters extortion group that sensitive internal documents were stolen, and is working to assess the situation. The organization, which represents 46 European member states, has confirmed the probe but declined to provide further comment at this stage.