Tag: data protection
511 articles
live facial recognition: Risky Exclusive Retail Trial
Sainsbury’s is trialling live facial recognition in two stores to catch repeat shoplifters, promising reduced losses and safer staff—but privacy advocates warn it’s intrusive, error-prone and could normalize constant surveillance. Will a few prevented thefts justify scanning shoppers’ faces, or will public concern and regulation redraw the line?
cookie privacy failures: Stunning Harsh Fines Exposed
France’s privacy watchdog hit Google and SHEIN with big fines for dropping tracking cookies and serving ads without proper consent — a wake-up call that could reshape online advertising and give users real control over their data.
data leaks: Must-Have Critical Detection Tips
A single exposed ClickHouse instance showed how quiet misconfigurations can hand attackers the breadcrumbs they need; detecting leaks early turns that slow-burning risk into a manageable incident. Start with inventory, automated scans, and clear playbooks to stop a minor misstep from becoming a full-blown disaster.
cyber incident: Stunning Risky Blow to Jaguar Sales
A recent cyber incident forced Jaguar to take IT systems offline, halting production and leaving workers home and customers wondering about deliveries. It’s a clear reminder that modern, connected factories can be brought to their knees by digital attacks — with real costs to sales, jobs and reputation.
exposed Ollama servers: Risky Must-Have Security Fix
Cisco Talos found 1,100+ publicly exposed Ollama servers, creating easy paths for data theft, malicious model swaps, and other abuse. It’s a wake-up call to fix misconfigurations, enforce authentication, and make secure defaults the norm.
restaurant robots: Shocking Security Risks Exposed
A researcher known for probing McDonald’s systems found Pudu Robotics left administrative controls wide open, letting attackers redirect delivery bots and issue arbitrary commands. Restaurants, hotels and regulators need to act now to secure these ubiquitous machines before misuse causes safety, privacy or reputational harm.
generative AI Stunning Risky Ban Divides Web
Vivaldi CEO Jon von Tetzchner drew a line in the sand by banning generative AI agents from browsing the web, arguing automation undermines consent, copyright and publishers’ income. The move reignites a crucial debate over who gets to shape the future of the open web.
systemic failures: Stunning $97M fine signals severe risk
SK Telecom was slapped with a record ₩134.5 billion (≈$97M) fine after regulators found basic security blunders that left internal networks exposed — a sharp reminder that weak segmentation and access controls can turn routine services into a breach gateway. The penalty is meant to punish the lapses and push the industry toward stronger, lasting protections for user data.

Church of England Shocking Data Leak: Damaging Trust Breach
A London law firm’s mass-email blunder exposed nearly 200 Church of England abuse survivors, shredding fragile trust and reigniting fears about privacy and stigma. Survivors are asking for concrete, survivor-led fixes—independent audits, better tech and trauma‑informed protections—if an apology is to mean anything.
cybersecurity legislation: Must-Have Rules, Risky Tradeoffs
A new CIISec poll shows most security professionals want tougher, clearer cybersecurity laws—urging policymakers to create practical, enforceable rules that boost defenses without stifling innovation. If lawmakers listen and invest in enforcement and workforce skills, stronger regulation could deliver real protection for businesses and citizens.
Commvault RCE: Critical Exploit – Patch Immediately
Could your backup system be a backdoor? Commvault patched four pre-auth vulnerabilities (notably CVE-2025-57788) in 11.36.60 that can be chained into remote code execution—update now or apply compensating controls to protect your backups and recovery.

SIM-swap attacks: Must-Have Urgent Defenses
A major breach exposing SIM identifiers makes SIM‑swap attacks a real and urgent risk — but you can protect yourself now by switching from SMS to app- or hardware-based MFA, adding a carrier PIN or passphrase, and watching your accounts for suspicious activity.

unauthenticated remote code execution: Critical Must-Have Patch
Commvault has released urgent patches after researchers published working exploits for two unauthenticated remote‑code‑execution chains—if you use Commvault, update now and audit your systems. This wake‑up call shows how critical backup infrastructure is and why quick patching, stronger access controls, and offline or immutable backups are essential to avoid catastrophic breaches.

Warlock ransomware: Exclusive Critical Threat to SharePoint
If your organization still runs on-premises SharePoint, Trend Micro’s findings are a wake-up call: attackers are using a ToolShell exploit to turn unpatched SharePoint instances into staging grounds for multi-stage Warlock ransomware campaigns that can steal data and cripple recovery. Patch promptly, lock down admin access, and treat collaboration platforms as critical assets before a trusted service becomes an easy path to extortion.
Allianz Life data breach: Stunning Risky Fallout
About 1.1 million Allianz Life customers may have had personal data exposed in a breach tied to the ShinyHunters group — here’s what to watch for and the quick steps you can take now to protect your identity and finances.
body-worn video Shocking Breach: Must-Have Fixes
When 96,000 body‑cam files disappeared during a system migration, the ICO’s rebuke laid bare how fragile trust in police video can be — and why stronger technical safeguards, clear retention rules and independent oversight aren’t optional but essential to restore confidence.

website after cyberattack: Risky Stunning Supply Outage
What do you do when the system that tells retailers what’s on the shelf goes dark? Stock in the Channel pulled its site after a cyberattack — saying customer data appear safe but providing no forensic report or timeline — leaving partners scrambling with manual checks, delayed orders and shaken trust.
manpower data breach: Exclusive Risky Impact Revealed
Manpower has disclosed a breach exposing personal data of nearly 145,000 registrants, putting jobseekers, contractors and clients at heightened risk of identity theft and fraud. If you applied for temp work, monitor your accounts and credit, be wary of recruitment scams, and ask Manpower what specific data was exposed.
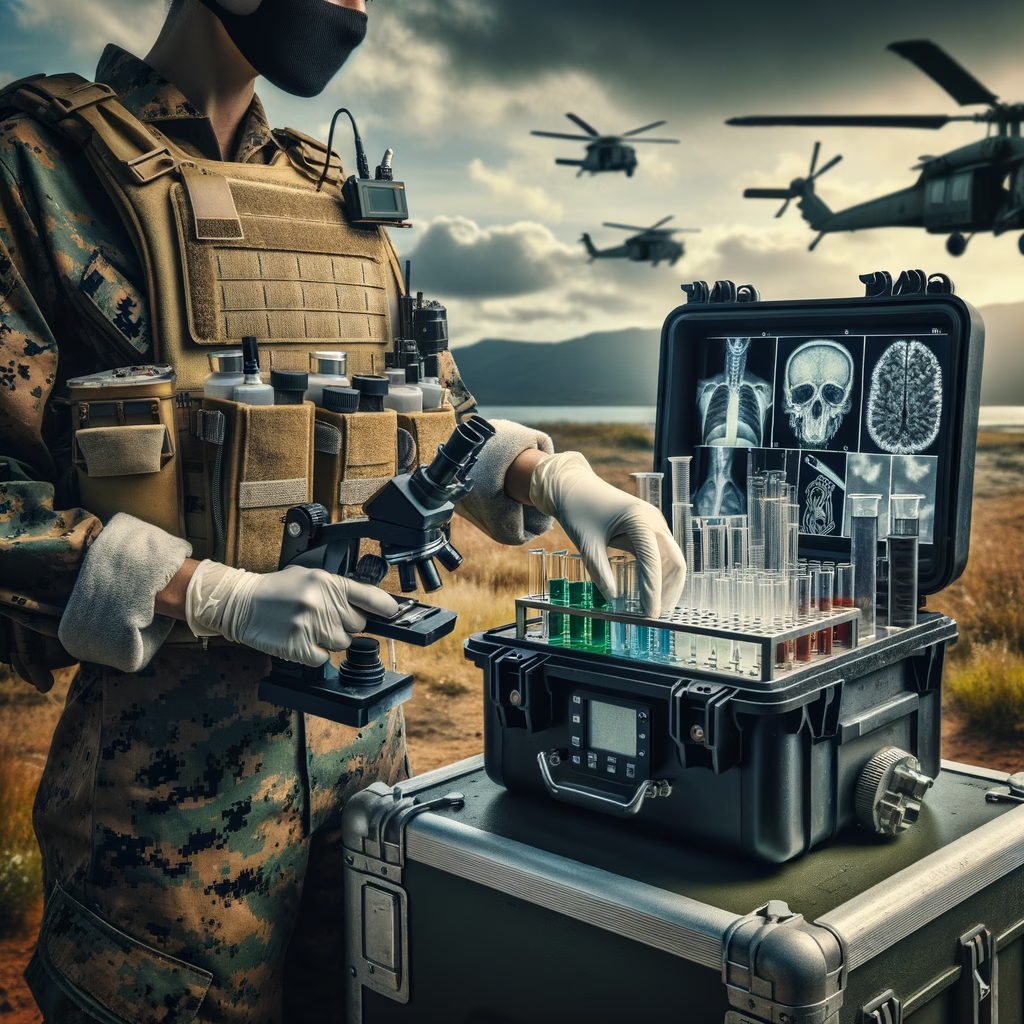
portable forensics labs: Must-Have, Game-Changing Upgrade
Imagine turning a scrap of blood or a smudge of a fingerprint into an ID in minutes, not days. The Marine Corps’ new portable forensics kits put lab-grade collection, analysis and secure reporting in warfighters’ hands to speed investigations, protect troops and sharpen intelligence—while calling for rigorous training, chain‑of‑custody rules and legal safeguards.

GDPR shoplifters photos Risky Warning — Must-Read
The U.K.’s ICO warns that sharing photos of suspected shoplifters can breach GDPR and unfairly tarnish people before guilt is proven. Retailers need to balance crime prevention with privacy rights and legal risk.

Shoplifters Photos GDPR: Exclusive Risky Warning
Think twice before sharing photos of suspected shoplifters: the ICO warns that public shaming—whether in-store or on social media—can breach GDPR and bring serious legal and reputational risks. As retailers hunt for deterrents, this reminder puts privacy, fairness and safer policing at the heart of the debate.

Click & Collect Must-Have Comeback Brings Relief
Good news — M&S has restored Click & Collect so shoppers can get back to the quick, convenient pickups they rely on; some online services remain down, but the retailer is working on fixes and stronger security.

KrebsOnSecurity Featured in HBO Max’s New ‘Most Wanted’ Series
Dive into the gripping world of cybercrime with HBO Maxs new series, featuring insights from KrebsOnSecurity, as it unravels the shocking case of hacker Julius Kivimäki and the critical need to safeguard our digital lives. Discover the chilling realities of data breaches and the urgent conversations around accountability that could reshape our future!

Insights from Security Leaders on the DaVita Data Breach
When a trusted healthcare giant like DaVita falls victim to a data breach affecting over 900,000 patients, it highlights the urgent need for robust cybersecurity in the digital age. Join us as we unravel the implications of this alarming incident and learn what experts are saying about safeguarding our most sensitive information.