Tag: cybercrime
870 articles
Ryuk Ransomware Operative Draws 2-Year Prison Term
An Armenian man has been sentenced to 2 years in prison and 3 years of supervised release for his role in a string of devastating Ryuk ransomware attacks on US companies. He was found guilty of hacking and encrypting systems, causing significant disruption and financial loss.
Microsoft Disrupts EvilTokens Phishing Service, Arrests Suspects
Microsoft swooped in to dismantle the EvilTokens phishing service, a sneaky AI-powered operation that had already compromised 12,000 email inboxes across 10,000 organizations worldwide. The service, which emerged in February, was sold as a phishing kit and came equipped with a clever AI chatbot that helped scammers identify and target high-value victims.
Microsoft Disrupts EvilTokens Phishing Service Targeting 12,000 Accounts
Microsoft's Digital Crimes Unit has struck a major blow against cybercrime, disrupting the EvilTokens phishing service that targeted over 12,000 accounts. Two suspected administrators were arrested in the UK as part of the operation.
North Korean Hackers Infect 30,000 Devices in Global Cyberattack
In a massive global cyberattack, North Korean hackers infected a staggering 30,000 devices across over 100 countries, siphoning off a whopping $10.7 million in cryptocurrency. The brazen heist, which ran from December 2025 to July 2026, also compromised over 7,000 cryptocurrency wallets.
North Korea Targets 30,000 Devices in Global Crypto Heist
North Korean hackers have launched a massive global crypto heist, compromising over 30,000 devices in more than 100 countries and stealing at least $10.71 million in cryptocurrency. This staggering cybercrime spree has been uncovered by a joint advisory from top cybersecurity agencies worldwide.
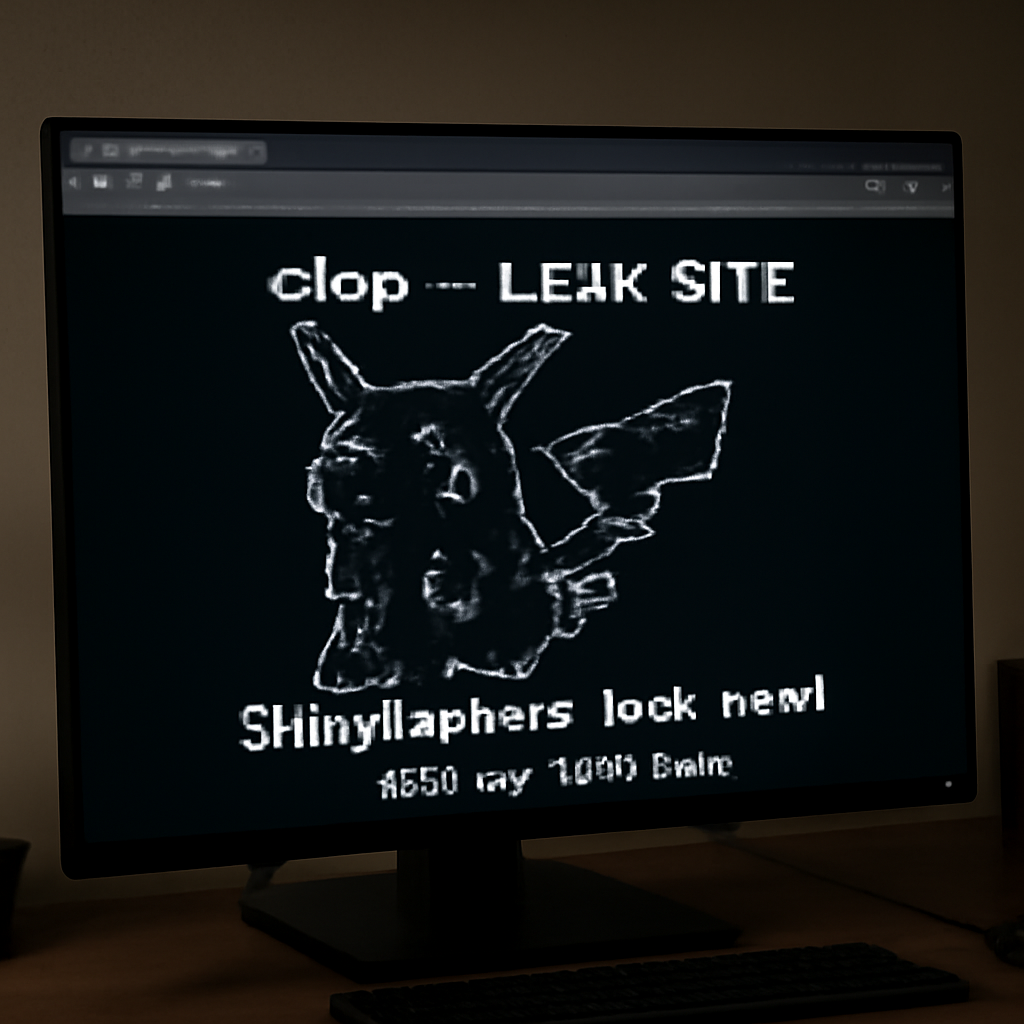
ShinyHunters Disrupts Clop Ransomware Gang's Operations
In a bold move, ShinyHunters infiltrated and defaced Clop's dark web leak site, claiming to have stolen sensitive private keys and server data that could dismantle the notorious ransomware gang's operations. This daring cyber heist has sent shockwaves through the ransomware underworld.
ShinyHunters Breaches Clop Ransomware Site, Threatens Extortion
In a stunning turn of events, the ShinyHunters group has breached the Clop ransomware gang's Tor leak site, leaving a cheeky message and ASCII art of Umbreon in its wake. The hackers boldly declared they'd been rooting the gang's systems since 2019.
Scattered Spider hacker pleads guilty to cybercrime spree
A 24-year-old Texas resident, Ahmed Hossam Eldin Elbadawy, has pleaded guilty to federal charges related to a cybercrime spree with the notorious Scattered Spider hacking group. The guilty plea, entered a year ago, has only now been made public as prosecutors seek to seize assets obtained through the crimes.
FBI Warns of $1.6B Hit from Impersonation Scams
Beware of scammers posing as law enforcement or government officials - they've already swindled over $1.6 billion from victims since January 2025, with the average loss per complaint topping $26,000. These impostors often use threatening tactics, like fake jury duty or "pay to remove charges" scams, to get their hands on your hard-earned cash.
US Authorities Disrupt NightmareStresser DDoS-for-Hire Service
In a major win for cybersecurity, US authorities have shut down NightmareStresser, a notorious DDoS-for-hire service that had been wreaking havoc globally. This coordinated takedown, dubbed Operation PowerOFF, marks a significant blow to cybercriminals who rely on these services to launch devastating attacks.
FBI Disrupts NightmareStresser DDoS-for-Hire Platform
The FBI has shut down NightmareStresser, a notorious DDoS-for-hire platform responsible for hundreds of thousands of attacks worldwide since 2022. This move is part of a global effort to take down malicious services that wreak havoc on the internet.
Swiss Court Sentences Ukrainian Ransomware Developer to 13 Years
A Swiss court has dealt a significant blow to cybercrime, sentencing a 52-year-old Ukrainian ransomware developer to nearly 13 years in prison. This landmark ruling sets a strong precedent for those who wreak havoc with malicious software.

Anthropic Exposes AI-Driven Cyber Threats
Cybercriminals and state-sponsored hackers have exploited AI tools for malicious activities like cyber attacks, propaganda, and mass surveillance, according to a report by Anthropic. The company's research uncovered dozens of alarming campaigns, revealing a new era of AI-driven threats.

Ukrainian Lawyer Turned Conti Coder Gets 4-Year Sentence
Meet Oleksii Oleksiyovych Lytvynenko, a Ukrainian lawyer-turned-ransomware coder who traded in his law books for a life of cybercrime as a key player in the notorious Conti operation, and ultimately paid the price with a four-year prison sentence. He was caught funneling thousands of dollars in cryptocurrency to his co-conspirators, including a $25,042 transfer that sealed his fate.

US Justice System Targets Conti Ransomware Operative with 4-Year Sentence
In a major win for cybersecurity, a Ukrainian national has been sentenced to four years in prison for his role in the notorious Conti ransomware attacks that hit 47 states and 31 countries, causing over $150 million in estimated damages. Oleksii Lytvynenko, 44, pleaded guilty to conspiracy to commit wire fraud and was extradited to the US to face justice.
FBI Unveils Cyber Strategy to Disrupt Threat Actors
The FBI is taking a bold stance against cyber threat actors with its first-ever Cyber Strategy, aiming to disrupt and hold accountable those who target the US. By taking decisive action and investing in cutting-edge tools, the agency promises to stay one step ahead of cyber threats.
US Sanctions Chinese Marketplace Xinbi Guarantee Over $24bn in Illicit Transactions
The US Treasury is cracking down on overseas scammers, sanctioning Chinese marketplace Xinbi Guarantee for facilitating over $24 billion in illicit transactions, and taking aim at two key service providers that helped it operate. This move is part of a broader effort to dismantle criminal enterprises that steal billions from American victims each year.
North Korea turbocharges cybercrime with AI-driven operations
North Korean hackers have turbocharged their cybercrime operations with AI-driven tactics, swiping a staggering $643 million in cryptocurrency in just the first half of 2026 - a whopping 66% of global crypto theft.
Microsoft 365 Phishing Op Exposes Thousands of Credentials
A recent phishing operation exposed a staggering 5,137 records from 461 organizations, including 1,032 plaintext passwords and 474 fully authenticated Microsoft 365 sessions that could be easily exploited. This massive haul highlights the alarming vulnerability of sensitive credentials to clever phishing tactics.
North Korea's Lazarus Fractures into Six Cyber Clusters
Meet the six distinct cyber clusters that now make up North Korea's notorious Lazarus group, each with its own unique tactics and targets. A single cryptocurrency theft of $62.5m highlights the alarming intersection of crime, statecraft, and corporate infiltration.
Outsider Phishing Kit Persists After Takedown Effort
Despite a major takedown effort that seized servers, domains, and $100,000 in payment wallets, the Outsider Phishing Kit is still up and running, with over 700 new phishing pages created within just a month. This alarming resurgence shows that threat actors are relentless in their pursuit of online deception.
Southeast Asia's Scam Factories Target Australians with AI-Driven Fraud
Australians lost a whopping $3 billion to scams in 2022, but the true figure is likely much higher. In Southeast Asia, scam factories have become a booming industry, churning out millions of victims and billions of dollars in losses for global criminal groups.
FBI Probes Massive Driver's License Breach Exposing 153 Million Records
A stolen cache of 153 million driver's licenses, containing sensitive info like birth dates, addresses, and ID numbers, has fallen into the wrong hands, putting millions at risk of identity theft. This breach is especially alarming since this type of data is often used to verify identities.
US-Led Operation Disrupts Sality P2P Botnet Infrastructure
A major international crackdown led by US law enforcement has successfully disrupted the notorious Sality P2P botnet, a malware network that has been wreaking havoc for over two decades. On August 31, authorities from Bulgaria, Hungary, Romania, and the US joined forces with Europol and private-sector partners to seize key domains and dismantle the botnet's infrastructure.