"Before I get my fingers on any system, I first walk the physical area that the system is located in — attackers do that when they're looking at a target too," Espinosa explained.
Christian Espinosa's walkthrough and the sticky note
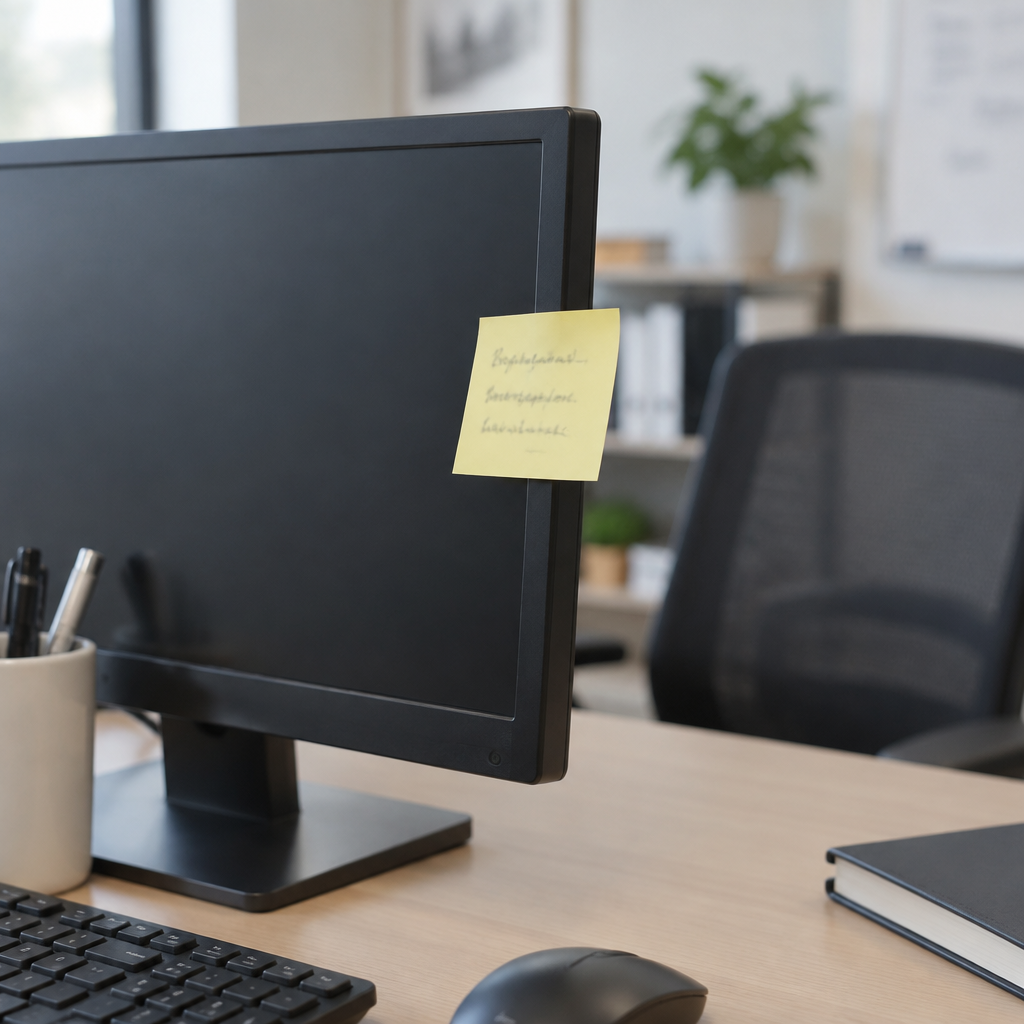
Christian Espinosa, a certified penetration tester and CEO of Blue Goat Cyber, discovered what he called a low-tech password manager: a sticky note taped to an employee's monitor. During a routine physical walkthrough of the client’s office, Espinosa photographed the sticky note, copied the password, and used it to try logging into that employee's account. The login worked.
From desk to VPN: how a single password escalated access
Espinosa then tried the very same password on the company's VPN — which the employee apparently maintained. Connecting to the VPN granted him full access to the company network and all shared drives. What began as a password on a monitor escalated, within moments, into an authenticated remote connection that exposed internal resources beyond a single desktop.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleHR and accounting: exposed PII, salary sheets, and vendor banking details
Once inside the network, Espinosa opened a shared drive the employee could access and found an HR folder containing personally identifiable information (PII). Files included home addresses, driver's licenses, and scanned W-4 forms, along with spreadsheets listing employee salaries. The employee account also linked to a document listing internal server names and the people in charge of each server — material Espinosa noted was "great for phishing." Another document contained instructions for logging into the accounting server.
The accounting server proved especially rich in sensitive data: a folder held vendor banking information, invoices, and payment records. Espinosa summarized the practical risk succinctly: "At that point, a password I had read from a sticky note during a walk-through had taken me from one desk to information that could have been used for payroll fraud, identity theft, or vendor-payment fraud."
Client response: disable the account, review logs, hunt for more sticky notes, tighten permissions
After the penetration test, Espinosa presented his findings to the client. The organization took immediate steps: they disabled the compromised account and began reviewing VPN access logs to determine whether others had accessed the network. They also conducted a physical search of the office to find any additional exposed passwords on sticky notes, and they tightened permissions on HR and accounting shares so only personnel who truly needed access could read those files.
What this means for technologists, procurement leaders, and employees
- Technologists and security teams: Espinosa’s observation that "physical security vulnerabilities are neglected much more often than technical security vulnerabilities" is the operative lesson. A technical perimeter such as a VPN or firewall can be nullified quickly if authentication secrets are left in view.
- Procurement leaders and managers: Espinosa highlighted a common disconnect — "firms invest in firewalls where a sticky note is placed 3 feet from the front door." Spending on network controls must be paired with controls on access, permissions, and basic physical security practices in the workplace.
- Employees and general staff: The operational risk is immediate and simple: do not expose your passwords. Espinosa warned of an especially plausible scenario — "Someone could have photographed that sticky note, walked out, connected to the VPN later that night, and started going through employee and financial records from somewhere else."
The episode is a compact demonstration of how a single human lapse can defeat multiple layers of protection. The client’s swift remediation — disabling the account, reviewing logs, searching the office, and restricting file-share permissions — addressed the immediate breach, but Espinosa’s parting image reminds us how trivial the initial vector was: a sticky note within view. That triviality is itself the warning: sophisticated controls can be undermined by the simplest human behaviors. Who could have photographed that note and acted afterward, and whether anyone already had, are questions the client’s log review sought to answer.