Vulnerability Management

Rows of computer servers and networking equipment in a brightly-lit server room with a subtle hint of a web server…

Apache HTTP Server Flaw Enables DoS and Potential RCE Attacks

A critical flaw in the Apache HTTP Server, known as CVE-2026-23918, can be exploited to launch devastating denial-of-service (DoS) and potential remote code execution (RCE) attacks, putting your online security at risk. This high-severity bug has been patched in Apache HTTP Server version 2.4.67, so updating is crucial to prevent attacks.

Analyst 207
Dimly lit storage room with scattered old computer equipment and faded labels, daylight peeking through grimy windows.

CVE Feeds Overlook End-of-Life Software Vulnerabilities

The blind spot in CVE feeds is leaving end-of-life software vulnerabilities flying under the radar, with a staggering 167,286 false negatives identified in 2025 alone. This oversight can have serious consequences, as outdated software can still be exploited, even if it's no longer receiving patches.

Analyst 207
Brightly-lit tech room with focused workstation, surrounded by screens and equipment.

NCSC Warns of Impending AI-Driven Patch Surge

Get ready for a surge of software updates, warns the National Cyber Security Centre's CTO, as AI-driven patching is set to uncover and fix long-standing vulnerabilities across your tech stack. Prioritise your external attack surfaces and prepare for a "patch wave" to stay ahead of the threat.

Analyst 207
Journalist sits at desk with laptop and papers, looking concerned in a neutral-colored room with a large window.

Polymarket Exposes Vulnerabilities in Event Verification Process

Polymarket's event verification process has exposed a glaring vulnerability, highlighting the risks of tying prediction market outcomes to fragile and easily manipulated sources of information. This weakness has even led to alarming threats against journalists, underscoring the urgent need for a more robust verification system.

Analyst 207
Rows of computer servers and equipment in a server room, with a single terminal's blank screen in the foreground.

Progress Patches MOVEit Automation Flaw Enabling Authentication Bypass

Progress Software has patched critical vulnerabilities in MOVEit Automation, including an authentication bypass flaw rated CVSS 9.8, that could allow hackers to gain unauthorized access and control. The update fixes CVE-2026-4670 and CVE-2026-5174, protecting users from potential data exposure and administrative takeover.

Analyst 207
Secure server room with prominent terminal display.

Progress Warns of MOVEit Automation Authentication Bypass Flaw

Progress Software has patched a critical authentication-bypass flaw in its MOVEit Automation product, and is strongly urging users to upgrade to the latest version to avoid low-complexity attacks by remote threat actors. Upgrading to version 2025.1.5, 2025.0.9, or 2024.1.8 and above will fix the vulnerability.

Analyst 207
Windows desktop with backup app open, surrounded by office furniture, and subtle hints of error in the background.

Microsoft Updates Disrupt Third-Party Backup Apps on Windows

Microsoft's latest Windows security update has caused disruptions to third-party backup apps, adding a vulnerable kernel driver to its blocklist to protect users from potential exploits. This change aims to prevent attackers from escalating privileges or executing arbitrary code, but has unfortunately caused failures in some backup products.

Analyst 207
Windows computer screen shows alert, person in background looks on with concern.

Microsoft Defender Flags DigiCert Certificates as Malware in False Positives

Microsoft Defender's recent signature update mistakenly flagged legitimate DigiCert root certificates as malware, causing widespread alerts and removal of the certificates, and even prompting some users to reinstall Windows. DigiCert quickly revoked the affected certificates within 24 hours of discovery, minimizing the impact.

Analyst 207
Modern tech facility with patch panel and computer screens, cables in background.

UK Cyber Agency Warns of Impending Patch Wave Fueled by AI

The UK's National Cyber Security Centre warns that AI is about to expose decades of technical shortcuts, demanding a massive and urgent patching effort - and organisations must prepare to patch quickly, frequently, and at scale. Get ready for a surge in fixes as buried technical debt is brought to the surface.

Analyst 207
Researcher working on a project with a large monitor displaying an abstract representation in a clean lab setting.

Anthropic Expands Claude Security Model to Cybersecurity Platforms

Anthropic's Claude Security Model just got a major upgrade, now helping cybersecurity platforms detect and fix software flaws faster than ever. With its advanced capabilities, Claude Security provides detailed vulnerability explanations, confidence rankings, and even generates step-by-step patch instructions.

Analyst 207
Government agency interior with industrial control system and technology infrastructure.

CISA's Zero Trust Guidance Falls Short on Cost, Implementation Details

While CISA's new zero trust guidance for operational technology is a step in the right direction, it leaves critical questions unanswered - namely, who foots the bill and how do organizations actually implement it? The guidance gets high marks for technical thinking, but falls short on practical details like funding, timelines, and automation.

Analyst 207
Server room with rows of equipment and a prominent control panel display.

Vulnerability Exploits Surge Against cPanel and WHM Software

A critical vulnerability, CVE-2026-41940, with a near-perfect severity score of 9.8, has been discovered in cPanel and WHM software, allowing hackers to bypass authentication and gain unauthorized access to your control panel. This flaw puts your online security at risk, so taking immediate action is crucial.

Analyst 207
Multi-monitor workstation with Remote Desktop security warnings on each screen.

Microsoft Fixes Remote Desktop Security Warning Display Flaw

Microsoft just dropped an optional update, KB5083631, to squash a bug that's been causing Remote Desktop security warnings to display incorrectly - a fix that's especially crucial for those using multiple monitors with different scaling settings. This targeted update is part of a larger release that includes 34 other changes to improve your Windows 11 experience.

Analyst 207
Modern workspace with laptop showing code editor and abstract codebase scan, cup of coffee and papers nearby.

Anthropic Unveils Claude Security for AI-Powered Vulnerability Scanning

Boost your organization's security with Claude Security, now in public beta, which scans codebases to detect and fix software vulnerabilities with just a few clicks. Say goodbye to tedious API integrations and custom agent builds - simply access the feature from the Claude.ai sidebar and start scanning today!

Analyst 207
Windows 11 laptop screen on a neutral surface with a blurred office background.

Microsoft Releases KB5083631 Update, Bolstering Windows 11 Security and Performance

Boost your Windows 11 security and performance with the latest optional update, KB5083631, which introduces a more secure processing mode for batch files and other quality improvements. Get ahead of the curve by installing this preview update now and be ready for the next Patch Tuesday release.

Analyst 207
A computer workstation with a blank laptop screen and scattered papers in a neutral background.

AI Agents Expose Identity Security Gaps

Imagine an AI agent that can uncover thousands of hidden security vulnerabilities, some of which have gone undetected for nearly 30 years - and the potential risks that come with it falling into the wrong hands. A single powerful AI agent can scan for weaknesses faster and more persistently than hundreds of human hackers, highlighting a pressing need for secure deployment.

Analyst 207
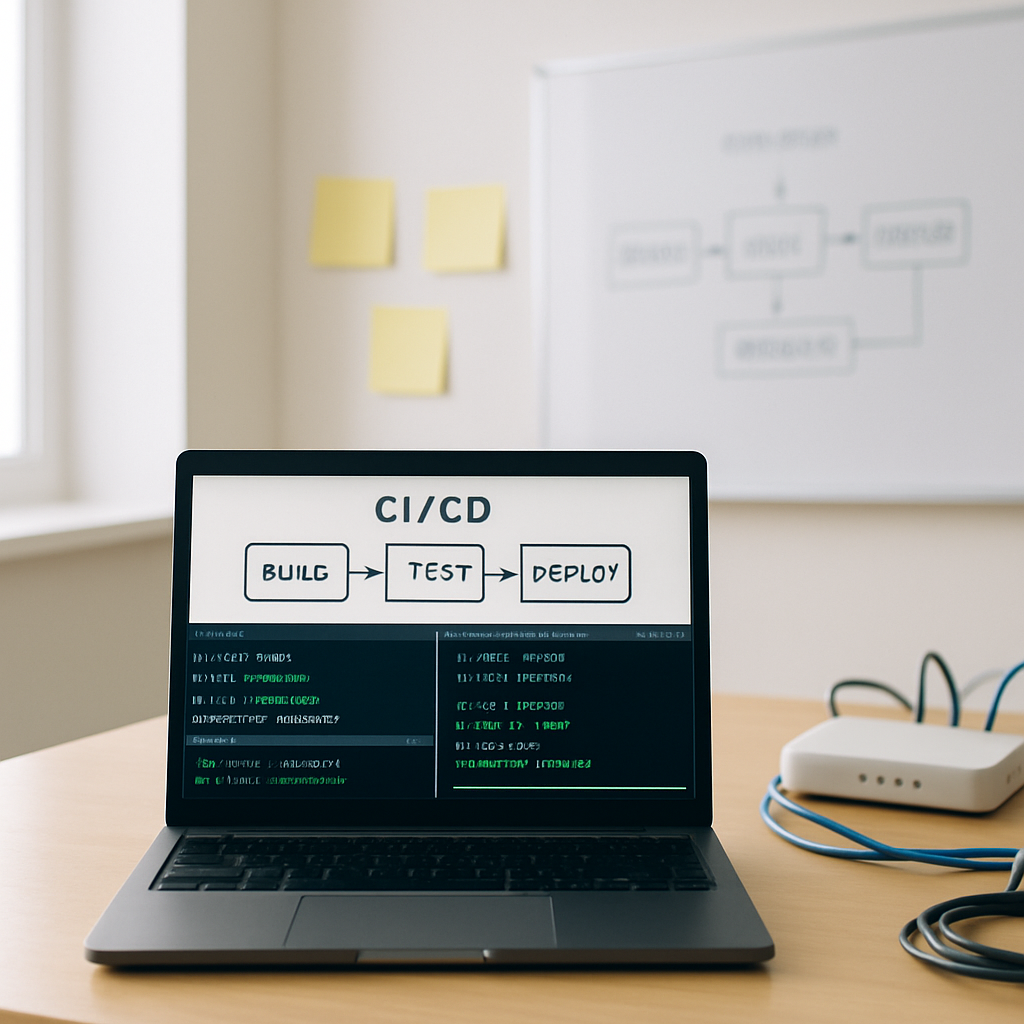
Google's Gemini CLI Fix Sparks CI/CD Pipeline Disruptions

Google's Gemini CLI Fix Sparks CI/CD Pipeline Disruptions

A recent patch for Google's Gemini CLI has sparked disruptions in CI/CD pipelines, ironically caused by a critical infrastructural flaw - not an AI quirk - that allowed remote code execution due to over-permissive workspace trust in headless mode. The fix, while swift, may trip automated pipelines that relied on the old settings.

Analyst 207
Dimly lit computer server room with equipment and an out-of-focus laptop in the foreground.

Linux Flaw Exposes Root-Level Access Across Major Distros

A newly discovered Linux flaw, nicknamed "Copy Fail," allows unprivileged users to gain root-level access to major distributions, putting countless systems at risk. This vulnerability, which involves a temporary write of just four bytes during a crypto operation, can be exploited by attackers to take full control of an operating system.

Analyst 207
Cluttered home office desk with Windows 11 laptop and backup software on screen.

Microsoft Update Disrupts Backup Software on Windows 11

Beware: the latest Windows 11 update, KB5083769, is causing backup software to fail on systems running versions 24H2 and 25H2 by triggering Volume Shadow Copy Service (VSS) timeouts. This disruption can lead to frustrating backup failures, affecting users of popular software like Acronis.

Analyst 207
Modern Linux workstation in a clean server room with natural daylight.

Linux Flaw Exposes Major Distros to Root Access

Meet CVE-2026-31431, aka "Copy Fail," a newly discovered Linux flaw that leaves major distros vulnerable to root access - and it's surprisingly easy to exploit, affecting a wide range of systems from 2017 to 2026.

Analyst 207
Rows of computer servers and racks in a dimly lit server room with exposed cables, conveying a sense of vulnerability.

cPanel Vulnerability Exposes Millions of Domains to Root Access Attacks

A critical cPanel vulnerability, rated 9.8 under CVSS, has been discovered, allowing attackers to craft a simple sequence of requests to bypass authentication and gain root access to servers, putting millions of domains at risk. Emergency patches are available to fix this gaping security flaw.

Analyst 207
Modern office workstation with laptop and papers, terminal screen and server room in background.

Linux Flaw Enables Unprivileged Root Access on Major Distributions

A newly discovered Linux flaw, dubbed "Copy Fail," allows unprivileged users to gain root access on major distributions by exploiting a logic error in the kernel's cryptographic subsystem. This high-severity vulnerability, tracked as CVE-2026-31431, poses a significant threat to Linux systems, enabling attackers to write controlled bytes into the page cache of readable files and escalate privileges.

Analyst 207
Sharp-focus laptop screen on a modern desk with blurred background.

Google Fixes Critical Gemini CLI Flaw Enabling Remote Code Execution

Google patched a critical flaw in Gemini CLI that allowed hackers to inject malicious code and take control of host systems, thanks to a report from Novee Security. The vulnerability, scoring a perfect 10.0 on the CVSS scale, has been fixed in recent updates to the @google/gemini-cli and google-github-actions/run-gemini-cli packages.

Analyst 207
University computer lab with student in background, blurred laptop screen displaying code in foreground.

Linux Flaw Enables Fast Root Access via Cryptographic Code

A newly discovered Linux flaw, dubbed Copy Fail, allows unprivileged users to gain root access by writing controlled bytes into the page cache of readable files, enabling a swift and stealthy privilege escalation. This vulnerability, tracked as CVE-2026-31431, poses a significant threat to Linux systems, putting them at risk of exploitation.

Analyst 207