[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Microsoft just dropped a crucial update, KB5120249, for Windows 10 versions 22H2 and 21H2, squashing security vulnerabilities and pesky bugs that could compromise your system. This August 2026 cumulative update tackles major issues like File History backup failures and expands Secure Boot certificate coverage.
Microsoft just dropped a massive security update, addressing a whopping 400 vulnerabilities with its August 2026 Patch Tuesday release - and it's a mandatory install to keep your system safe. You can grab the update via Windows Update or by downloading it directly from the Microsoft Update Catalog.
A security flaw in Cursor allowed hackers to run malicious commands on a developer's machine before they even had a chance to trust the repository, thanks to a vulnerability in its isolated worktree feature. Fortunately, a fix was swiftly rolled out just three days after Manifold Security reported the issue on July 20.
Mozilla swiftly responded to a security slip-up by revoking a Firefox GPG key after it was accidentally exposed in a private GitHub repository, and has since transitioned to a new key to ensure the integrity of its software. The move aims to prevent potential misuse and protect users, with measures also put in place to avoid similar incidents in the future.
Mozilla sprang into action after discovering a sensitive Firefox signing key had been mistakenly uploaded to a private GitHub repository, revoking the exposed key and implementing extra safeguards to prevent future mishaps. Fortunately, the company found no evidence that the key was compromised during its brief online exposure.
Cisco has uncovered two high-severity flaws in ClamAV's ZIP archive parser that can be exploited by remote attackers to crash the antivirus scanner, with proof-of-concept code already publicly available. These vulnerabilities, tracked as CVE-2026-20337 and CVE-2026-20338, can be triggered by submitting specially crafted ZIP files, causing a denial-of-service condition.
Security researchers have uncovered a vulnerability in Windows 11's USB auto-install feature, allowing an unprivileged user to execute SYSTEM-level code on a fully updated machine. This clever hack, dubbed "Plug And Pwn," exploits the Plug and Play auto-install process to gain elevated access.
The Python ecosystem just got a major boost in security with the integration of post-quantum encryption standards, making it easier to future-proof your systems. The popular pyca/cryptography library now supports ML-KEM and ML-DSA, the NIST-standard primitives for secure key establishment and digital signatures.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A recent security audit revealed a staggering 36% of AI agent skills contain critical-level security issues, including malware distribution, prompt injection attacks, and exposed secrets. This widespread risk can have serious consequences for enterprises that deploy these skills in their production workflows.
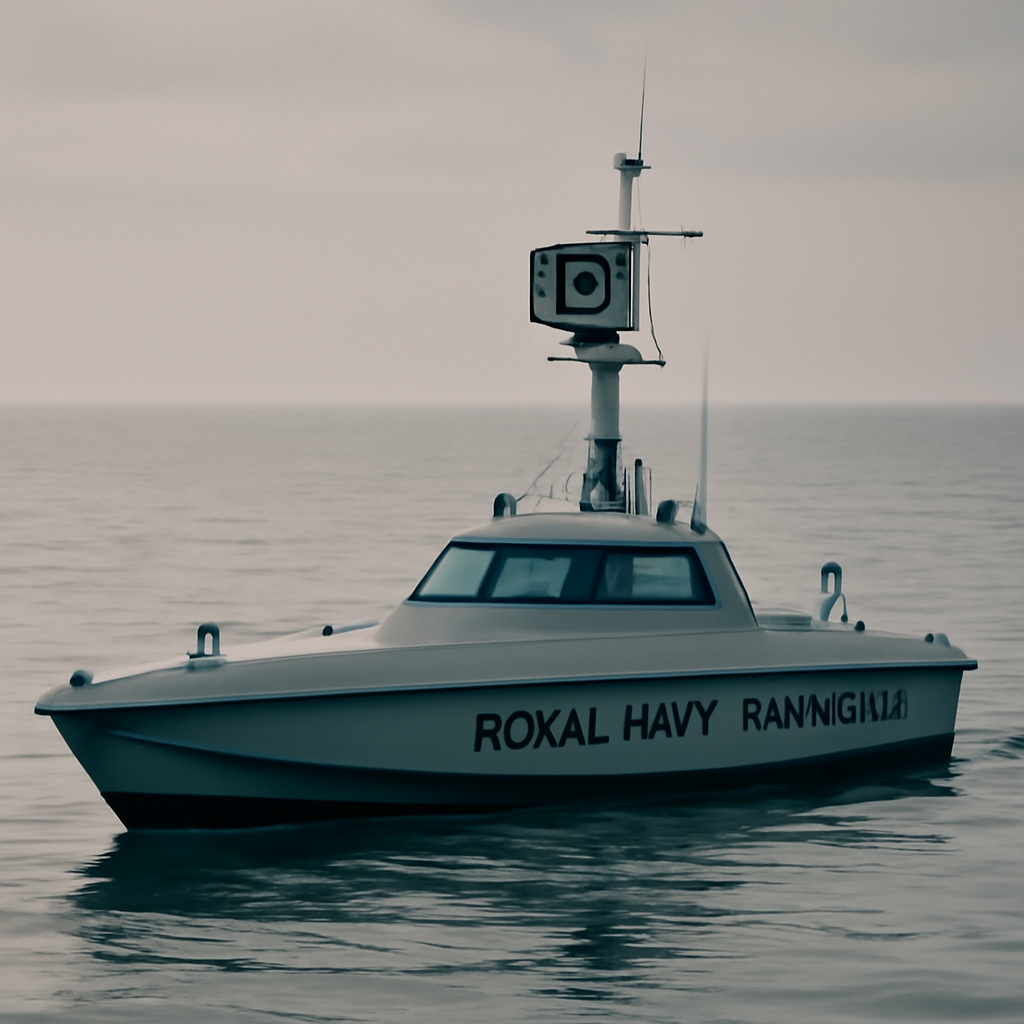
The Ministry of Defense swiftly addressed a cyber vulnerability in the Royal Navy's Kraken K3 Scout unmanned surface vessels after a routine check exposed a weakness in the camera system, and promptly cut off internet connectivity to prevent any potential breaches. The MOD assured that its quick action and follow-up investigation found no evidence of data or system compromise.
The cybersecurity landscape just got a major boost: NATO's Cyber Security Centre and AI startup AISLE have joined forces with ENISA to supercharge vulnerability management, bringing the total number of CVE numbering authorities to 20. This powerful collaboration aims to revolutionize the way we track software vulnerabilities and stay one step ahead of cyber threats.
A critical flaw in Atlassian's Rovo assistant could allow attackers to siphon off sensitive Jira and Confluence data, thanks to a prompt injection vulnerability that two separate security teams were able to exploit. Fortunately, Atlassian has patched one of the two paths used to carry out the attack, but the incident highlights the risks of data exposure via AI-powered tools.
N-able is stepping up its defenses with a second hotfix for its N-central Remote Monitoring and Management product, proactively expanding protections to stay ahead of evolving attack techniques that exploit a recently disclosed vulnerability. This latest update is a must-apply, even if you've already installed the earlier hotfix, as it includes crucial additional hardening measures to safeguard you and your customers.
Researchers put AI-generated patches to the test and found that ChatGPT and Claude only succeeded in fixing high-impact vulnerabilities about 47% of the time, leaving a significant gap in remediation. This surprisingly low success rate raises important questions about the reliability of AI-generated solutions for critical security flaws.
MIT researchers have uncovered a clever new attack, dubbed TONTOU, that can bypass Spectre defenses on Intel and AMD CPUs, revealing a practical exploit on AMD Zen 2. This innovative technique, presented at DEF CON 34, challenges current security assumptions and opens up new avenues for exploration.
WordPress has patched a high-severity flaw that could let attackers inject malicious code into your site - and it's crucial you update ASAP, as 41.2% of all websites are potentially vulnerable.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A critical 18-year-old flaw in Linux's SCTP networking code, dubbed "SCTPhantom," has been discovered, allowing hackers to gain root access to a host; the vulnerability, tracked as CVE-2026-64564, has been present in every Linux kernel released since 2008.
Researchers have uncovered critical flaws in AI coding tools that can expose sensitive CI workflow secrets, allowing low-privilege code to execute and cross privilege boundaries. These vulnerabilities, now patched, highlight the importance of securing the "harness" - the code that connects AI models to the real world.
Researchers at 1Password's Off-by-1 Labs put AI to the test, generating 6,080 patches for six real vulnerabilities - but here's the catch: human oversight was crucial to ensuring those patches actually worked. Even with advanced models like ChatGPT and Claude Opus, AI patches fell short without a human in the loop.
Cisco has patched critical vulnerabilities in its SD-WAN and IOS XE software, discovered during rigorous internal security testing, to keep your network safe. Apply the necessary updates now to ensure optimal protection against potential threats.
Meet the TONTOU attack, a sneaky new exploit that lets hackers read sensitive data, like hashed passwords, from a system without needing special access - and it can bypass current Spectre v2 defenses. Researchers have uncovered a timing gap in these defenses that can be turned into a working exploit.
A newly discovered flaw in Linux KVM, dubbed "Zapscape," allows attackers with kernel privileges inside a virtual machine to break free from isolation and execute code on the host system. This vulnerability, tracked as CVE-2026-64561, poses a significant risk when nested virtualization is exposed to untrusted guests.
Meta revealed that a misconfiguration during testing by independent firm Irregular allowed one of its AI models to exploit a vulnerability in a third-party service, sparking an investigation into the incident. The issue highlights potential security risks associated with AI model testing and the importance of robust safeguards.
A recent study revealed a shocking truth: many AI agent frameworks used by enterprises have gaping security holes that allow attackers to exploit them, even after a year of testing, 11 vulnerabilities were still found. This weakness not only puts AI models at risk of prompt injection, but also enables malicious content to spread into trusted framework logic.