[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The insider risk landscape has become a complex and critical security challenge, evolving beyond the traditional disgruntled worker to include emerging threats like shadow AI, synthetic identities, and ideologically motivated sabotage. Today's insider risk requires a predictive, intelligence-driven approach to safeguard against data leaks, infiltration, and rapid exfiltration.
To uncover the sneaky tactics used by employment scammers, a team of researchers took a bold approach: they created a fake company to study these scams firsthand. By doing so, they gained valuable insights into the methods scammers use to deceive job seekers.
Insiders pose a uniquely potent threat because they already have the keys to the kingdom - and traditional defenses often miss the mark by relying on alerts that don't account for the devastating impact of trusted accounts gone rogue. To stay ahead, defenders must validate their readiness against insider threats by asking tough questions about access, escalation, and lateral movement.
Join our weekend open discussion, a relaxed space to chat about anything that caught your attention this week - from the news we didn't cover to topics that are on your mind. Share your thoughts, ask questions, and engage with our community in a friendly and respectful conversation.
Meet Scam Alert, WhatsApp's new on-device AI feature that helps you spot potential scam messages - and take action to protect yourself. This optional feature flags suspicious messages from unknown senders, giving you the power to block, report, or ignore them.
Google Chrome just dealt a major blow to scammers, blocking over 7 billion unwanted Android notifications daily in the first quarter of 2026. This massive reduction was made possible by Chrome's enhanced anti-abuse systems and notification controls.
Justin Swaddle, a 20-year-old UK man, has been sentenced to two years in prison for terrorizing 117 vulnerable victims worldwide with online abuse, forcing them to perform shocking acts of self-harm and sexual activity for his own twisted online popularity. He must also register as a sex offender.
Some designers are now creating clothing with patterns specifically designed to confuse facial recognition systems, but experts warn that these products may not work as promised. These so-called adversarial garments are being marketed as a way to throw algorithms off track, but their effectiveness remains untested.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment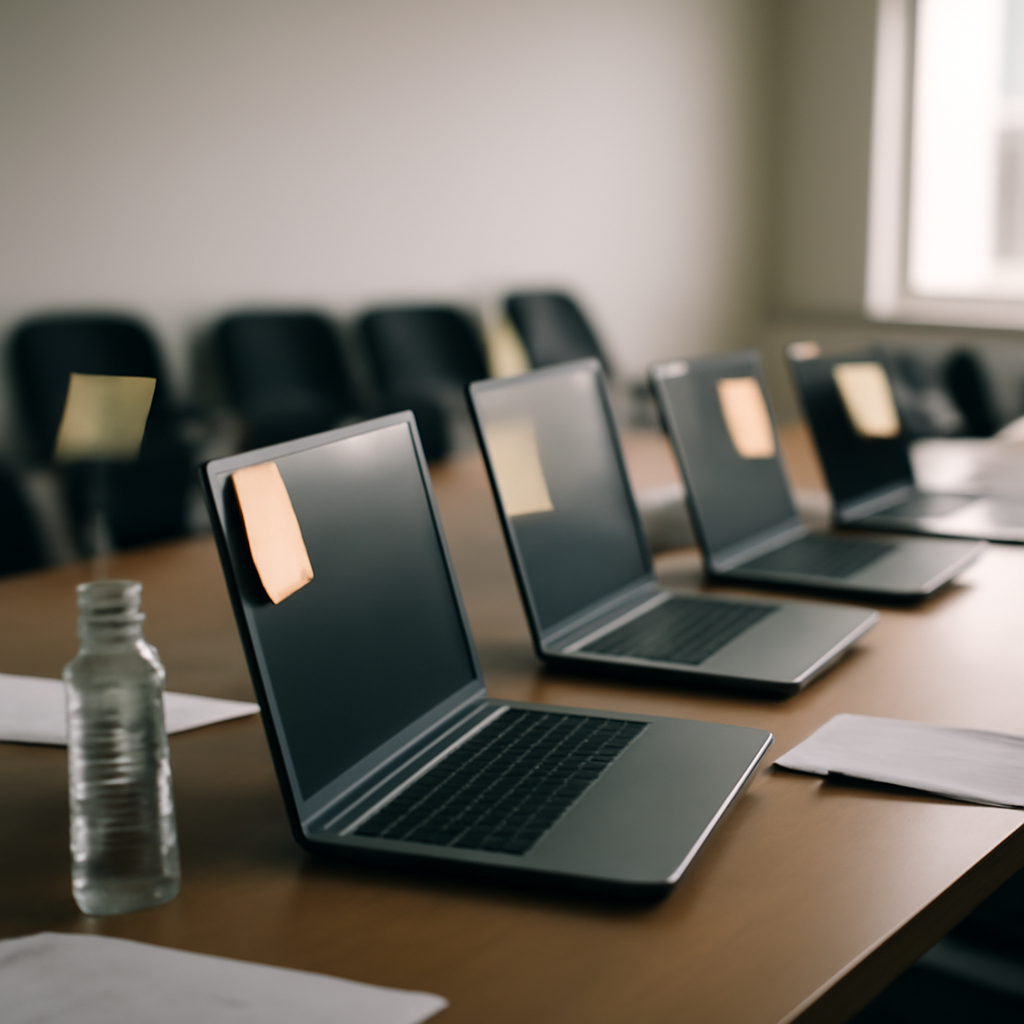
A shocking security slip-up occurred when a contractor stumbled upon login credentials scribbled on sticky notes attached to laptops in a conference room, which were then photographed and used to access sensitive proprietary documents. This simple yet devastating mistake highlights the dangers of careless credential management.
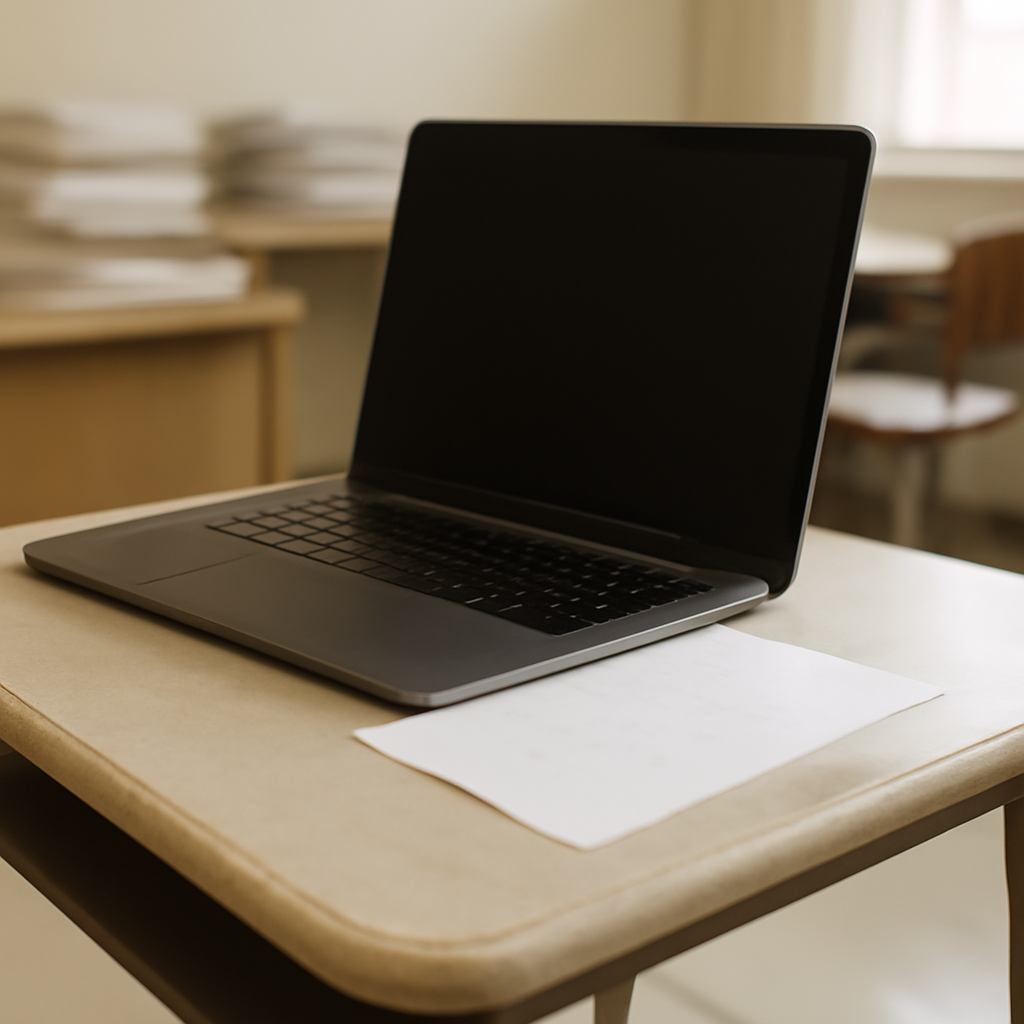
Imagine a cybercriminal stumbling upon a sticky note with a school's most sensitive login credentials - literally stuck to the bottom of the headteacher's laptop - and gaining instant access to pupils' personal info, emails, and confidential files. This shocking discovery highlights a glaring lack of basic cybersecurity practices in schools.
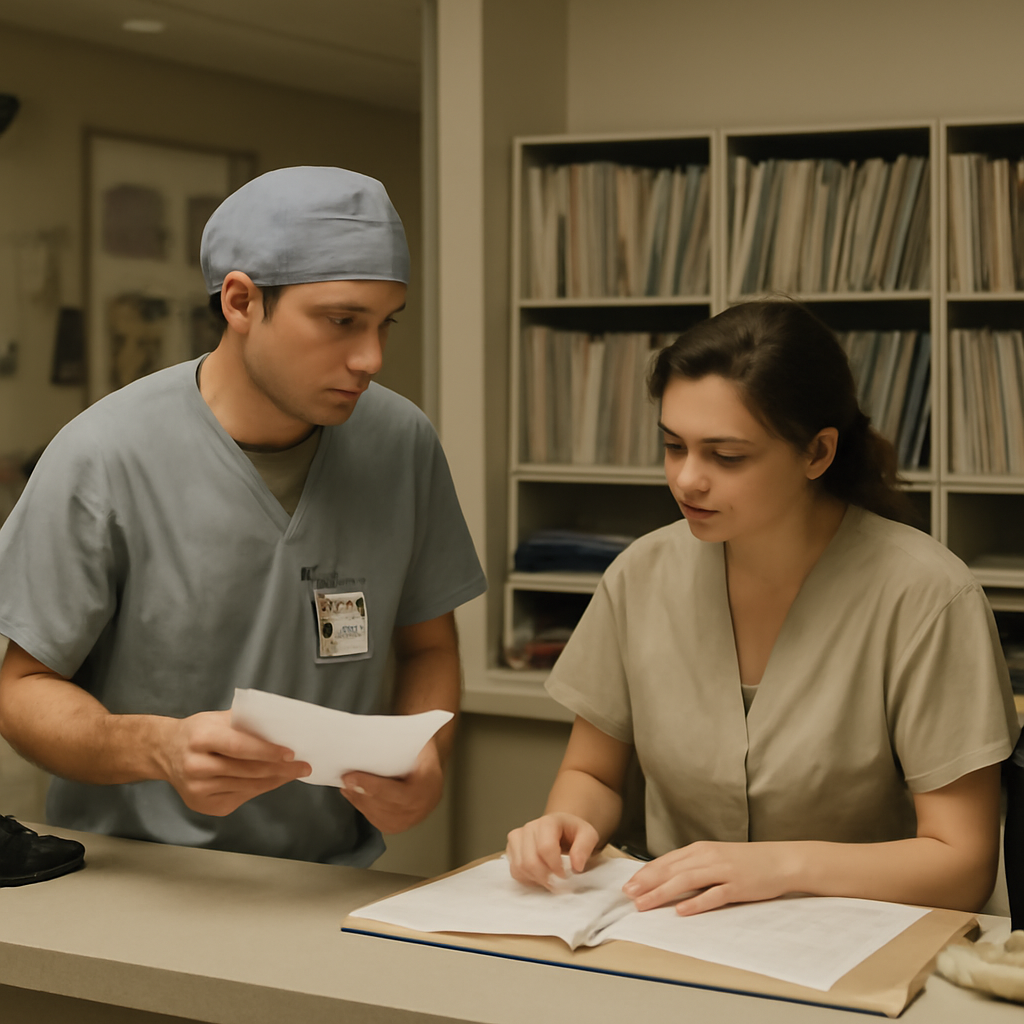
Meet Dahvid Schloss, a red teamer who pulled off a daring heist at a hospital by exploiting a surprisingly simple vulnerability: human nature. By donning scrubs, sporting a fake badge, and spinning a convincing tale, Schloss was able to sweet-talk his way past a nurse and retrieve a sensitive file.
With AI tools like writing assistants and coding copilots now used by 76% of employees, security leaders are recognizing the need for proactive governance to stay ahead of the curve. Traditional blocking methods are no match for the speed of workarounds, which often take just minutes to find, versus official approval routes that can take weeks.
Beware of scammers on social media pretending to be FBI agents - the Internet Crime Complaint Center (IC3) will never contact you directly through social media, email, or phone to investigate cybercrimes or recover lost funds. If someone claims to be from IC3 on social media, they're likely a scammer.
A whopping 78% of CISOs believe their board-level decision makers are in the dark about employee-driven cyber risks, leaving companies vulnerable to attacks. The disconnect is alarming, especially as AI-powered scams and social engineering attacks become increasingly sophisticated.
Leaving multi-factor authentication optional has left countless bank accounts vulnerable to theft, with devastating consequences - just ask the 84-year-old victim who lost nearly $30,000 when thieves exploited this security gap. By making MFA optional, banks are inadvertently rolling out the red carpet for thieves.
Opera's new Paste Protect feature helps keep you safe from sneaky ClickFix attacks by automatically blocking suspicious copy actions that could land malware on your device. This clever tool outsmarts scammers who try to trick you into pasting malicious commands, protecting you from unwanted surprises.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Newfoundland and Labrador Health Services is hitting the brakes on a well-intentioned but misguided phishing test that left staff feeling frustrated and burnt out. The healthcare organization has apologized and pledged to review its approach after sending employees a fake email offering an extra paid day off.
As cybercriminals shift their focus from email to other trusted channels, a glaring gap in non-email threat detection has emerged, leaving organizations vulnerable to attacks on messaging and social platforms. A recent survey of cybersecurity pros reveals that while 60% of attacks now target non-email channels, half of respondents admit their organizations lack confidence in detecting these threats.
With women making up only 17 percent of Australia's cybersecurity workforce, the industry's glaring gender gap leaves us vulnerable to AI-driven threats and puts women at greater risk of online harms. Closing this gap is crucial to bolstering our digital protection and ensuring a safer online world for all.
Join the conversation, but first, a friendly reminder: let's keep it civil and respectful in Bunker Talk, even when politics heat up - no name-calling, no personal attacks, and stick to the facts. By following these simple rules, we're building the best commenting crew on the net.
Researchers put an AI agent named Pinchy to the test with classic phishing simulations, and the results were alarming: sometimes it fell for the bait, spilling sensitive data, and other times it successfully blocked the attacks. The experiment revealed a stark vulnerability - AI agents can be tricked into exposing confidential information.

Google's new fake call detection feature sends a silent signal to verify the caller, instantly warning you if a scammer tries to impersonate someone you know. If the signal is missing, your device double-checks with the caller's actual phone to keep you safe.

Bayer is revolutionizing its security training to combat AI-driven threats by ditching traditional checklist-driven advice for a psychology-first approach that outsmarts increasingly realistic social engineering tactics. This bold move aims to empower staff and suppliers to safely harness the power of generative AI.

Imagine being called in to help a CEO recover deleted files, only to discover a shocking secret: a treasure trove of explicit content stored on a company file share that's accessible to anyone. The awkward moment that followed will leave you cringing - and wondering how something so sensitive could be so carelessly exposed.