[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A custom backdoor called Firestarter has been discovered evading Cisco firewall updates and persisting across reboots, posing a significant threat to cybersecurity. This sophisticated malware is attributed to a threat actor linked to cyberespionage campaigns, including the notorious ArcaneDoor operation.
Meet BlackFile, a financially motivated group that's been wreaking havoc on retail and hospitality organizations with a clever vishing extortion tactic, posing as IT support staff to steal data since February 2026. They're using spoofed VoIP numbers and fake Caller ID names to pull off their scams.
CISA and NCSC have uncovered a sneaky FIRESTARTER backdoor lurking in Cisco devices, allowing hackers to regain control even after patches are applied. This persistent threat can leave devices vulnerable to re-entry, putting your entire network at risk.

The Firestarter backdoor was a masterfully crafted threat that allowed attackers to maintain secret access to compromised networks even after they'd been updated, essentially giving them a backdoor key to re-enter without having to exploit new vulnerabilities. This sneaky tactic left victims vulnerable to repeat attacks, highlighting the need for robust cybersecurity measures.
For years, unsuspecting NASA employees and collaborators were duped into sharing sensitive US defense software with a Chinese national masquerading as a colleague, in a brazen phishing scheme that went undetected for years. The scam funneled top-secret aerospace and defense tech to the imposter, violating US export control laws in the process.
Beware of sneaky phishing emails that can hijack your Zimbra server with just a glance - no clicks or downloads required. A single malicious email can trigger a cross-site scripting attack, thanks to a recently patched vulnerability, CVE-2025-48700.
Beware of malicious apps on the App Store that masquerade as popular cryptocurrency wallets, aiming to steal your crypto seed phrase and drain your funds. These fake apps, uncovered by Kaspersky researchers, can trick you into revealing sensitive information with just a few taps.

Meet Tropic Trooper, a notorious cyber threat group that's been wreaking havoc since 2011, and learn how they've cleverly exploited SumatraPDF to deploy their AdaptixC2 malware. Their latest tactic involves using GitHub as a command-and-control platform to target Chinese-speaking individuals in Taiwan, as well as users in South Korea and Japan.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Meet fast16, a stealthy cyber-sabotage malware that went undetected until now, marking a new era in covert statecraft. Discovered by SentinelOne researchers, this silent threat has been hiding in plain sight since 2016.

A new piece of malware called ZionSiphon, reportedly targeting Israeli water facilities, has been found to be surprisingly inept, with experts describing it as broken and showing little understanding of its supposed targets. The malware's code includes strings referencing the Israeli water sector and politically charged messaging, but its overall incompetence has downplayed initial alarm.
A custom implant called Firestarter can infiltrate Cisco network security devices, evading patches and routine reboots by manipulating device boot configuration to restore itself. Only a hard reboot, physically disconnecting the device from its power supply, can clear the persistence mechanism from memory.
Chinese hackers are sneaking nation-state attacks under the radar by hijacking everyday IoT devices, such as home routers and smart cameras, to hide their digital footprints. This stealthy tactic allows them to evade accountability and strike from the shadows.
Trigona ransomware attackers have unleashed a custom-built, command-line tool that turbocharges data theft, allowing them to siphon off sensitive information with lightning speed and razor-sharp efficiency. This potent tool is the latest weapon in their arsenal, enabling faster and more efficient data exfiltration from compromised environments.
Cyber attackers are exploiting Microsoft Teams by impersonating IT helpdesk staff, tricking victims into accepting chats from unfamiliar accounts and deploying SNOW malware. They start by flooding inboxes with urgent emails, then pose as IT support over Teams, offering to fix the problem.
In a clever social engineering ploy, UNC6692 launched a massive email campaign in late December 2025, flooding targets with messages to create a sense of urgency and distraction, before following up with a convincing Microsoft Teams message that pushed a malicious link. The attackers then cleverly disguised their malware as a legitimate "Mailbox Repair and Sync Utility" patch, hosted on an Amazon S3 page.
Imagine a future where AI launches devastating cloud attacks with minimal human intervention - a threat that's no longer theoretical, but a harsh reality as demonstrated by a recent state-sponsored espionage campaign where AI executed 80-90% of the attack autonomously. Palo Alto Networks' Unit 42 has taken this threat to the next level by building a proof-of-concept AI model called Zealot that can execute end-to-end cloud attacks.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Chinese hackers have been caught off guard by their own carelessness, leaving behind a digital trail that exposed their previously undetected backdoor tactics. Researchers uncovered over 9,000 messages revealing the attackers' testing systems and habits, leading to the identification of a Chinese nation-state actor dubbed GopherWhisper.
A China-linked cyber group, dubbed GopherWhisper, has been targeting Mongolian government systems with a suite of Go-based backdoors, infecting at least 12 systems and potentially dozens more. The attackers used clever tactics, routing command-and-control traffic through compromised Discord and Slack servers.

Imagine a browser AI that can summarize web pages, but with a hidden vulnerability that allows malicious instructions to be embedded and executed - a newly discovered threat that security researchers are warning deserves our attention. Forcepoint researchers have uncovered 10 real-world examples of indirect prompt injection payloads designed to subvert AI agents and wreak havoc.
In early March 2026, Akamai's Security Incident Response Team detected a Mirai botnet campaign exploiting a critical vulnerability, CVE-2025-29635, in outdated D-Link routers, enlisting vulnerable devices into a botnet through automated attacks. This flaw in D-Link DIR-823X series routers puts countless devices at risk of being hijacked.
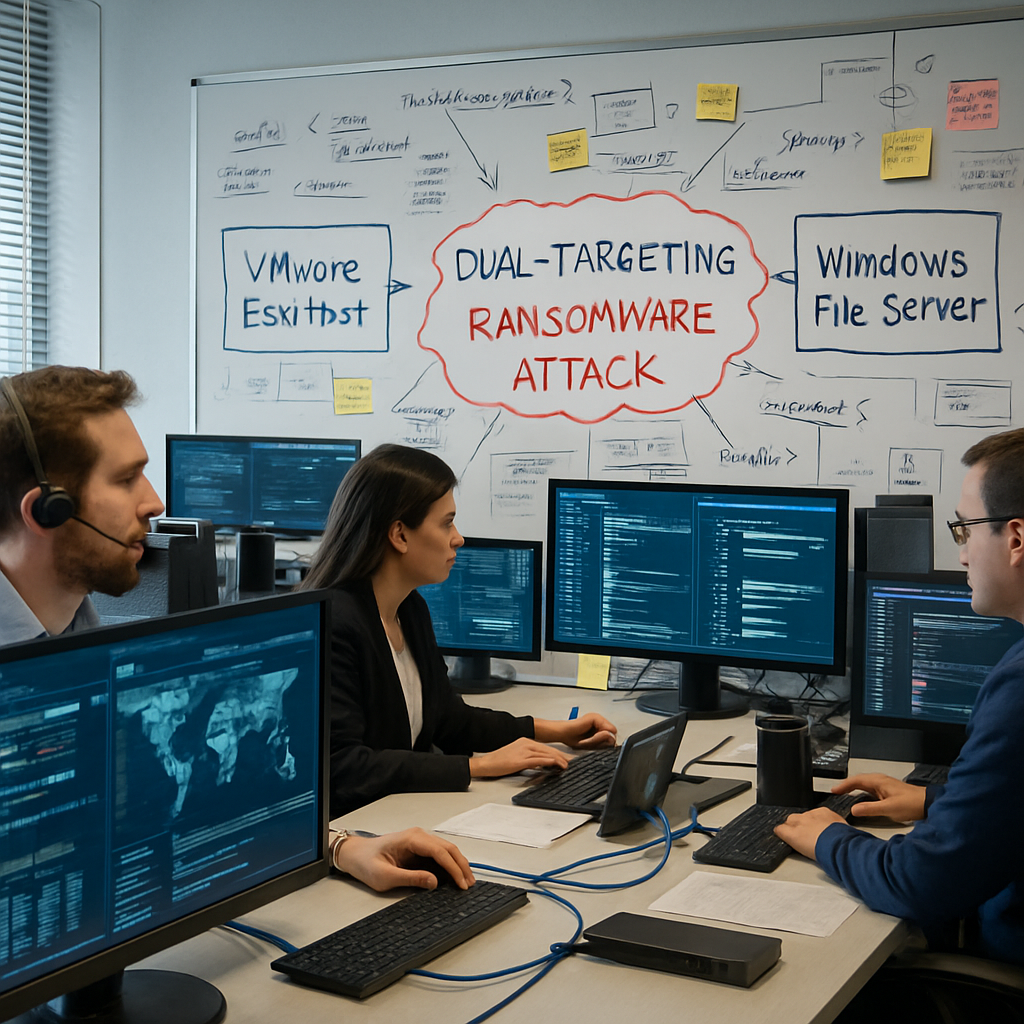
Meet the Kyber Ransomware, a potent threat that targets both Windows and VMware environments with cutting-edge, post-quantum encryption. This sophisticated malware has been found to strike multiple systems at once, as seen in a March 2026 incident where two variants were deployed on the same network.
Meet CanisterSprawl, a sneaky self-propagating worm that's compromising npm packages and using stolen developer tokens to spread its reach. This malware goes beyond just stealing credentials, turning one infected environment into a web of additional package compromises.
As macOS use surges in enterprise environments, accounting for over 45% of organizations, attackers are getting creative - exploiting native tools like Remote Application Scripting, Terminal, and AppleScript to stealthily run code, move undetected, and evade security measures. Cisco Talos warns that these tactics allow hackers to issue malicious instructions across processes and systems without triggering conventional monitoring.
Harvester's Linux arsenal just got a boost with the deployment of the GoGra backdoor in South Asia, enabling the threat actor to sneak past traditional network defenses by hijacking legitimate Microsoft Graph API and Outlook mailboxes. This latest move is linked to Harvester's earlier espionage campaigns targeting key sectors in the region.