[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Kaspersky's analysis uncovered a sneaky malware attack on PyPI, where OceanLotus hackers uploaded fake packages that looked like harmless libraries, tricking users into installing the ZiChatBot malware. The malicious packages, uploaded in July 2025, masqueraded as legitimate tools like uuid32-utils, colorinal, and termncolor.

MuddyWater, an Iran-linked APT group, has been caught exploiting a ransomware disguise to secretly infiltrate systems, using interactive tactics to harvest credentials and gain internal access. By masquerading as a Chaos ransomware affiliate, the group aimed to throw off detectives and cover its espionage tracks.
MuddyWater hackers have cleverly used Chaos ransomware as a decoy to mask their true intentions - and it's not about making a quick buck. Instead, their tactics suggest a more sinister goal, blurring the lines between state-sponsored espionage and cybercrime.

Cushman & Wakefield, a real estate giant, has confirmed a vishing incident at the hands of notorious threat actors ShinyHunters and Qilin Gang, highlighting the growing threat of social engineering attacks. This recent breach serves as a stark reminder of the importance of robust security measures.
Attackers are already exploiting a newly discovered Linux flaw called CopyFail to line their pockets, and it's essential to stay informed about this developing threat. The vulnerability has been identified, and malicious actors are capitalizing on it - but details on affected systems and patches are still emerging.
Cyber attackers have cleverly exploited the Microsoft Phone Link feature to steal sensitive credentials and one-time passwords, all without needing to infect mobile devices with malware. By targeting this built-in Windows application, hackers can access synced phone data and extract valuable information.
Palo Alto Networks firewalls are under attack by zero-day exploits targeting a vulnerability in the User-ID Authentication Portal, allowing hackers to execute malicious code with root privileges. This buffer overflow flaw, tracked as CVE-2026-0300, poses a significant risk to organizations with Internet-exposed firewalls.
Meet DarkSword, a sneaky malware that's been targeting iOS devices with a sophisticated exploit chain, leveraging six different vulnerabilities to deploy its final-stage payloads across iOS versions 18.4 through 18.7. Google Threat Intelligence Group has tracked its use back to November 2025, with multiple actors - from commercial vendors to suspected state-sponsored operators - employing it to compromise devices.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Meet Quasar Linux, a sneaky new malware targeting developers with a potent blend of stealth, persistence, and credential theft capabilities that can compromise software supply chains. This Linux implant is quietly infiltrating dev and DevOps environments, putting cloud toolchains at risk.
In just 48 hours, a massive phishing campaign hit over 35,000 users across 13,000 organizations in 26 countries, with nearly 1 in 5 targets in the healthcare and life sciences sector. The alarming attack highlights the speed and scale of modern phishing operations.
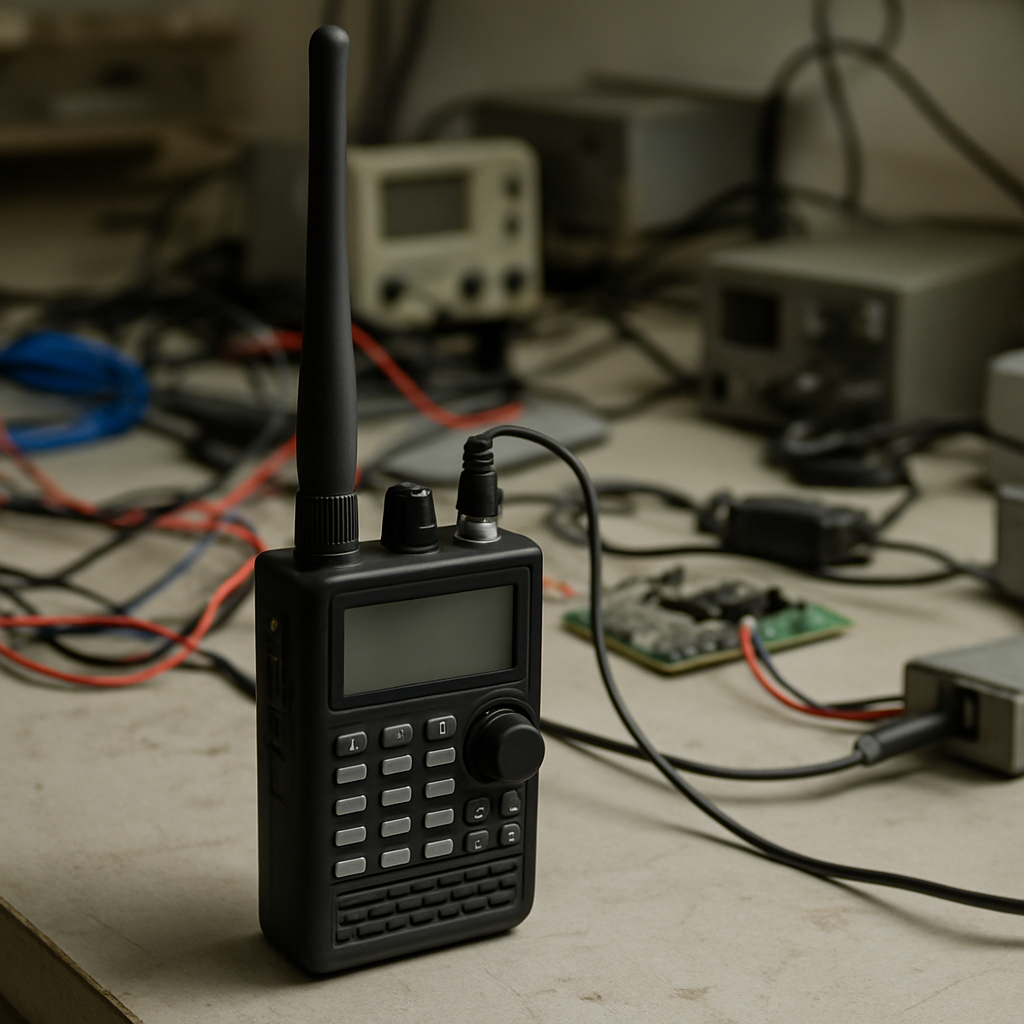
A clever 23-year-old hacker brought Taiwan's high-speed rail to a standstill for 48 minutes by exploiting a shocking weakness in the TETRA system, used to coordinate critical communications. Using just a few pieces of easily-bought equipment, the attacker sent a fake "General Alarm" signal that was treated as the real deal.
A Latvian hacker has been sentenced to 8.5 years in federal prison for his role in a massive ransomware extortion scheme that targeted over 54 companies, causing hundreds of millions of dollars in losses. Deniss Zolotarjovs, 35, helped former Conti leaders extort payments from victims over a two-year period.
In just 48 hours, a massive phishing campaign targeted over 35,000 users across 13,000 organizations in 26 countries, using convincing fake compliance emails to steal login credentials. The sophisticated attack, detected by Microsoft's Defender Research team, hit US firms hard, but its global reach was widespread.

Cushman & Wakefield recently fell victim to a vishing incident, but swift action was taken to contain the breach and protect its systems. The company has confirmed that its operations remain normal and it's working closely with experts to investigate and respond to the incident.
A long-running phishing campaign has compromised over 80 US organizations by using legitimately signed remote monitoring software to install silent, persistent backdoors, according to Securonix research. The attack begins with a clever email impersonating the US Social Security Administration, tricking victims into downloading malicious payloads.
Unmanaged OAuth grants are a ticking time bomb in enterprise workspaces, with 80% of security leaders recognizing them as a critical or significant risk. A recent attack by threat actor UNC6395 exploited valid OAuth refresh tokens to breach Salesforce environments of over 700 organizations, highlighting the devastating consequences of neglecting OAuth security.
Full SOC coverage without building one. Nubivance deploys and manages Rapid7 InsightIDR and MDR for organizations that need detection and response, not another dashboard.
Get coverage
Beware: CloudZ malware is exploiting Microsoft's Phone Link feature to intercept SMS and OTPs, putting your sensitive info at risk. This sneaky attack uses a plugin called Pheno to tap into your Phone Link activity and steal your private messages.

Meet Deniss Zolotarjovs, a Latvian national who helped his ransomware gang extort dozens of companies - and even a government entity with a crippled 911 system - by leveraging stolen sensitive data, including children's health information. He's now facing 8.5 years in prison for his role in the Karakurt extortion operation.
ScarCruft hackers have launched a sneaky attack on a popular video game platform, infecting both Windows and Android users with a new backdoor called BirdCall. The multi-platform threat has been targeting ethnic Koreans in China since late 2024, allowing hackers to gain unauthorized access.
Security researchers at Eset stumbled upon a sneaky plot by North Korean hackers, who infiltrated popular Android games to spy on defectors by hiding a backdoor called BirdCall in the apps. The malicious code was cleverly disguised in game files available for download on a regional gaming platform's official website.
North Korean hackers APT37, also known as ScarCruft, have cleverly expanded their BirdCall malware to target Android devices, adapting their Windows backdoor to spy on mobile users. They even used a popular gaming platform to sneak the malware onto unsuspecting devices.
A massive phishing campaign targeting over 35,000 users worldwide has been uncovered, using sophisticated email templates that convincingly masquerade as legitimate internal communications. The highly convincing lures successfully hit organizations across 26 countries, with a staggering 92% of targets based in the US.

The shutdown of Grinex, a Kyrgyzstan-registered cryptocurrency exchange, highlights the cat-and-mouse game of sanctions evasion, where experts warn that the ecosystem's fragmentation will only make it harder to track illicit activity. As Kaitlin Martin, a senior intelligence analyst at Chainalysis, notes, a fractured ecosystem makes it increasingly difficult to target evasive maneuvers.
A massive 108-gigabyte data trove allegedly stolen from Liberty Mutual has been exposed by ransomware gang Everest Group, containing sensitive policyholder information including names, addresses, and financial details. The group claims to have published the data after the insurance company failed to respond to its demands.