Malware & Ransomware

Dimly lit server room with technicians in background, large screen display in foreground.

Ransomware Actors Exploit Active Directory Group Policy

In a clever twist, hackers used Active Directory Group Policy to spread ransomware across an entire domain without installing a single malicious file on individual computers. By exploiting this native tool, they were able to hijack wallpapers, lock screens, and even disable admin accounts, all with just a few clicks.

Analyst 207
Typical office workstation with laptop and papers on a blurred background.

PowerShell Backdoor TASK#STOMP Exfiltrates Sensitive Data in Stealthy Campaign

Meet TASK#STOMP, a sneaky PowerShell backdoor that's quietly harvesting sensitive business data, including documents, Wi-Fi passwords, and clipboard contents, while also taking screenshots and allowing remote control. This stealthy campaign uses a clever VBS-driven framework to evade detection and keep its operators informed.

Analyst 207
Network device on a rack with cables and wires against a neutral-colored wall.

Cisco Zero-Day Exploited in Active Attacks

Cisco is warning of a critical zero-day flaw in its Identity Services Engine (ISE) that's being actively exploited, allowing attackers to bypass authentication and gain unauthorized access with just a crafted request. This severe vulnerability, tracked as CVE-2026-76460, has been assigned a maximum CVSS score of 10.0.

Analyst 207
Laptop screen shows WordPress dashboard amidst cluttered workspace and blurred online marketplace.

Exvicy Malware Framework Exploits Rival Code to Target WordPress Sites

Malware operators are sounding the alarm: detections of the Exvicy Malware Framework are on the rise, with one seller warning that daily detections are making their service less effective. The Russian-speaking actor behind Exvicy is now charging $2,000 a month for the malware-as-a-service framework, up from $1,200 just a few months ago.

Analyst 207
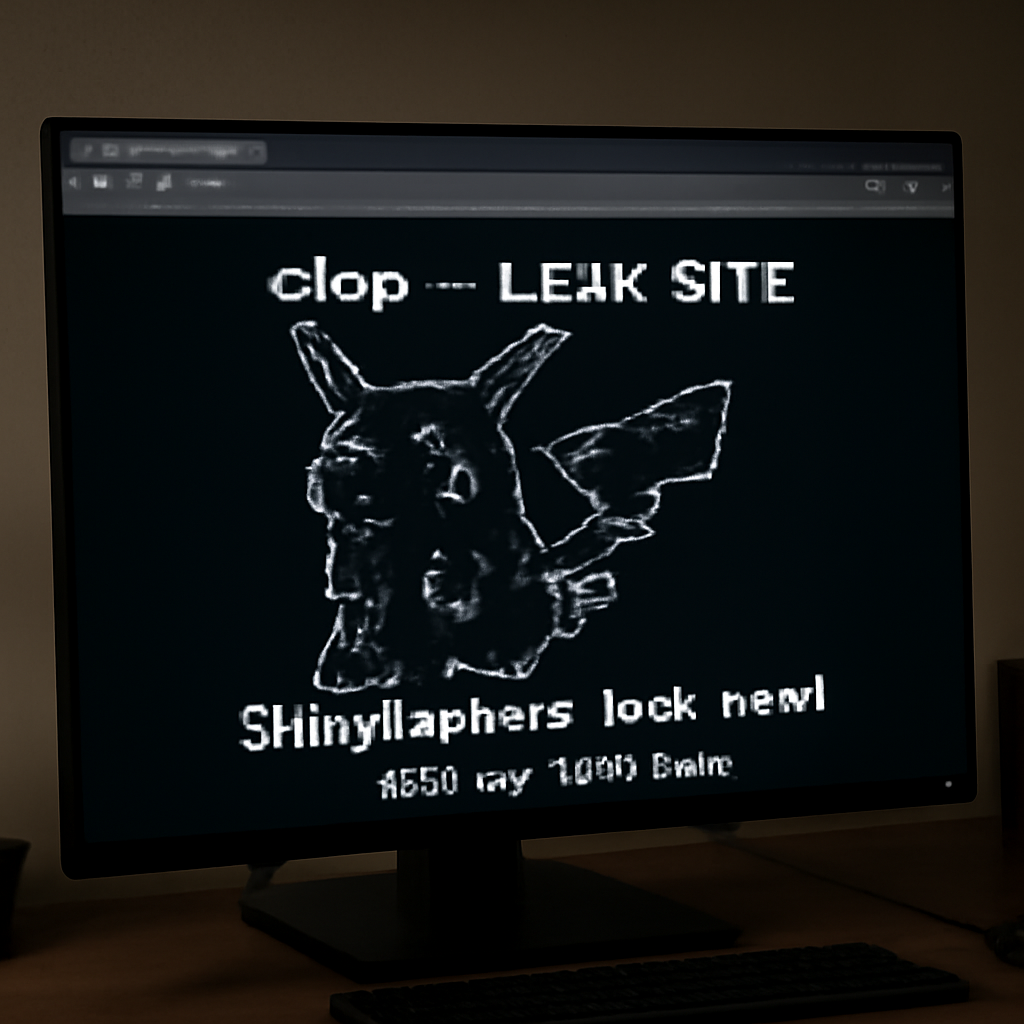
Dark web leak site on a computer screen displays defaced Clop ransomware page with Pokémon ASCII art and a message claiming…

ShinyHunters Disrupts Clop Ransomware Gang's Operations

In a bold move, ShinyHunters infiltrated and defaced Clop's dark web leak site, claiming to have stolen sensitive private keys and server data that could dismantle the notorious ransomware gang's operations. This daring cyber heist has sent shockwaves through the ransomware underworld.

Analyst 207
Dark-web setting with defaced webpage and seized domain banner on screen.

Rivals Hijack Clop's Leak Site, Demand Eight-Figure Payout

A rival hacking crew, ShinyHunters, has hijacked Clop's dark-web leak site, posting a bold takeover message and demanding an eight-figure payout in a shocking display of cyber power. The group claimed to have exploited a vulnerability in Clop's software to seize control of the site.

Analyst 207
Person sitting at computer with concerned expression, surrounded by office items.

Rust Project Warns of Fake Job Interviews Used to Spread Malware

Scammers are tricking people into installing malware or executing malicious commands by posing as potential employers or clients on video calls, often under the guise of a job interview or contract opportunity. They set up fake company profiles and LinkedIn pages to make their ruse appear legitimate.

Analyst 207
Person looks concerned at smartphone with laptop nearby, text message conversation visible.

Revolut Phishing Attacks Surge After Data Breach

Hackers are taking advantage of a recent data breach at Revolut to ramp up phishing attacks, with scammers sending convincing smishing messages to customers in an attempt to harvest more account information. These attacks are getting more sophisticated, with scammers even collecting selfies or videos to fuel further identity fraud or scams.

Analyst 207
Laptop screen showing social media platform on a desk in a corporate office.

Malware Campaigns Exploit ClickFix to Deploy RATs via Blockchain Infrastructure

Malicious ads masqueraded as legitimate software, spreading malware like ChainScript RAT through blockchain infrastructure via ClickFix lures, targeting both macOS and Windows users. Security researchers uncovered 108 fake ads from a hijacked Reddit account that seeded multiple malware families over just 48 hours.

Analyst 207
Rows of computer workstations and servers in a brightly-lit Indian IT services office.

Jade Sleet Targets Indian IT Provider with FLATROOF and ROOFDECK Backdoors

North Korean-aligned threat actor Jade Sleet has launched a targeted attack on an Indian IT provider, using FLATROOF and ROOFDECK backdoors to gain long-term access to high-value targets by exploiting developer workflows and supply-chain tooling. The attack, detected as early as March 18, 2026, is part of a persistent campaign that highlights the group's evolving tactics.

Analyst 207
Travelers walk near a public area in a brightly-lit airport terminal, conveying global connectivity and vulnerability.

North Korean Hackers Infect 30,000 Devices in Global Campaign

North Korean hackers have pulled off a massive global cyberattack, infecting 30,000 devices in over 100 countries and making off with millions in cryptocurrency. The financially motivated gang, known as WaterPlum, has been siphoning funds and account credentials from over 7,000 cryptocurrency wallets since December 2025.

Analyst 207

ShinyHunters Breaches Clop Ransomware Site, Threatens Extortion

In a stunning turn of events, the ShinyHunters group has breached the Clop ransomware gang's Tor leak site, leaving a cheeky message and ASCII art of Umbreon in its wake. The hackers boldly declared they'd been rooting the gang's systems since 2019.

Analyst 207
A brightly-lit computer workstation in a neutral setting with a blurred image on the monitor.

AI Model Exploits Chained Flaws to Breach OpenAI Staff Accounts

In just 72 hours, researchers exploited a chain of flaws - starting with a bug in image-processing software - to breach several OpenAI staff accounts and gain access to an internal code repository. The surprising attack began with a vulnerability in a library used to parse HEIC and HEIF images, highlighting the potential for unexpected entry points.

Analyst 207
Technicians monitor a network operations center with a central server surrounded by equipment and cables.

Orkes Conductor Flaw Exploited in Wild, Fortinet Warns

A critical flaw in Orkes Conductor is being exploited in the wild, allowing attackers to execute malicious code remotely without authentication. Fortinet has reported blocking 1,290 attack attempts in just 24 hours, a 132% surge in malicious activity.

Analyst 207
Modern office space with people in background and empty laptop screen in foreground.

North Korean Hackers Exploit Job Seekers to Steal Crypto and Data Worldwide

North Korean hackers are posing as dream employers to trick software developers and IT pros into handing over sensitive data and cryptocurrency - all under the guise of a job offer that's too good to be true. They're using fake job opportunities to get close to their targets, with AI, cryptocurrency, and NFT firms in their sights.

Analyst 207
People work in a brightly-lit office setting with laptops and papers scattered around.

North Korea Exploits Job Seekers to Infect 30,000 Devices

North Korean hackers have compromised over 30,000 devices by posing as recruiters, targeting unsuspecting job seekers with a clever ruse that steals sensitive information and cryptocurrency. By exploiting stolen IDs, these cybercriminals can impersonate victims and generate foreign currency, ultimately funding the regime.

Analyst 207
Cluttered desk with laptop, papers, and office supplies, cup of coffee in sharp focus.

Transparent Tribe Exploits GitHub for Rust Backdoor Deployment

Meet RUSTYSHADE, a sneaky Rust-based backdoor that's being used by Transparent Tribe to target government and defense organizations in India and Afghanistan, leveraging private GitHub repositories for covert communication. This latest tactic is part of a broader campaign, dubbed Operation RapidRust, aimed at infiltrating sensitive targets.

Analyst 207
Laptop on cluttered desk with search results on screen and GitHub repositories blurred in background.

Malware Campaign Targets LastPass Users with Rapuncel Infostealer

Beware of a sneaky malware campaign targeting LastPass users with the Rapuncel Infostealer - hackers are using fake GitHub repositories and search engine tricks to steal your info. Victims who search for popular software like LastPass Authenticator may unknowingly download the malware.

Analyst 207
Server room with rack-mounted servers and cables, laptop screen in foreground shows blurry browser alert.

Browser Alerts Expose Rogue Scripts in Thousands of Sites

Thousands of websites, repositories, and documentation pages are unwittingly exposing users to rogue scripts, thanks to a long-abandoned content delivery network domain that was re-registered by a malicious actor. This simple domain hack has opened the door to a massive security vulnerability.

Analyst 207
Retail store interior with a checkout counter in the foreground and blurred shopping areas in the background.

Settra Ransomware Targets Retail, Manufacturing with Advanced Tactics

Meet Settra, a sneaky new ransomware variant that's targeting retail and manufacturing firms with clever tactics, leaving a trail of chaos in its wake. First spotted in June, this malicious software has already been linked to two separate attacks, one in July and another in September.

Analyst 207
Laptop and code editor on a minimalist desk with npm package docs nearby.

npm Packages Deliver WeaselBiscuit Stealer to Harvest Chrome Data

Meet WeaselBiscuit, a sneaky new malware that's small but packs a punch, stealing Chrome data by masquerading as harmless npm packages. This stripped-down stealer is designed to evade detection, and it's being spread through 13 infected npm packages.

Analyst 207
Blurred laptop screen on a desk in a brightly-lit office with rows of workstations in the background.

Threat Actor Exploits LLM to Craft PhantomRaven npm Stealer

Meet PhantomRaven, a sneaky JavaScript information stealer crafted by a financially motivated actor - and likely created with the help of a large language model, a cutting-edge AI tool. The surprising twist? The malware's code reveals telltale signs of AI involvement, including verbose comments and placeholder code.

Analyst 207
Factory control panel with blurred computer screen in background.

Ransomware Attacks Surge in Manufacturing Sector

Ransomware attacks on manufacturing organizations are surging, with a staggering 22% of all victims coming from this sector over the past year, making it the most targeted industry for the fifth year in a row. This alarming trend shows a steady rise in attacks since 2022, with a significant spike in early 2026.

Analyst 207
Smartphone on cluttered desk with blank screen and nearby laptop.

RatHat Malware Exploits ADB to Maintain Shell Access on Android Devices

Meet RatHat, a sneaky Android malware that uses Accessibility tricks and ADB exploits to break free from the sandbox and gain shell-level control on your device. By combining these tactics, RatHat can secretly pair with your device and run malicious daemons with elevated privileges.

Analyst 207