[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Developer Charles Jones was hit with a whopping $11,089.77 in Google Cloud charges after his account was hijacked, despite reporting the compromise and revoking the implicated keys. The unexpected charges, largely linked to Gemini image-generation models, left him stunned as his business doesn't even use such technology.
Want to make life harder for hackers? The National Cyber Security Centre teamed up with penetration testers to share practical tips on building secure systems from the ground up.
Meet Kristopher Johnson and Michael, two expert red teamers who walked into a company's office through an unlocked maintenance door, posing as new IT employees, and gained access to the building by simply offering to help shovel ice. Their easy entry exposed a shocking truth: physical security lapses can give hackers an open invitation to wreak havoc on your network.
Infosec pros are ditching automated pentesting tools as they fail to detect AI-driven vulnerabilities, with 78% of practitioners experiencing critical false negatives. Humans are needed to outsmart AI-era flaws that automated scanners miss.
Nearly two-thirds of AI chatbot apps for iPhone, that's 282 out of 444 tested, are leaking sensitive API keys, leaving users' data vulnerable to exposure through open AI proxy access. This alarming discovery highlights a critical security gap in many popular iOS AI apps.
Researchers at Adversa AI have uncovered a shocking weakness, dubbed GuardFall, that lets advanced open-source coding agents slip past safety filters and execute destructive shell commands, exposing them to shell injection risks. This gap between text-based checks and shell execution leaves a trail of vulnerability wide open to exploitation.
Microsoft's new Teams admin policy gives you more control over third-party bots in meetings, allowing you to block unwanted guests and require explicit approval for external bots to join. This enhanced security feature can be easily managed for individual users or specific groups through the Teams Admin Center.
Microsoft is stepping up its Teams security game with enhanced bot protections, allowing admins to block third-party bots from joining meetings without approval. This new policy gives organizations greater control over who can access their meetings, helping to prevent malicious apps and unwanted disruptions.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Millions of devices are vulnerable to local attacks due to flaws in popular sharing services like AirDrop and Samsung Quick Share, discovered by researchers Arash Ale Ebrahim and Nils Ole Tippenhauer. They found six distinct flaws that can be exploited by nearby attackers to crash services or bypass security checks.
Kali Linux just got a major boost with its latest release, packing 9 new tools to supercharge your cybersecurity arsenal. This update slashes boot time by nearly 3x and trims down the initrd to just 60 MB for VM users.
Microsoft is stepping up its game to protect Teams meetings from unwanted bot intrusions by introducing a virtual bouncer that keeps automated accounts at bay. This new defensive measure is a significant boost to Microsoft Teams security.
A popular Chrome ad blocker with over 10 million installs, Adblock for YouTube, has been found to have a shocking vulnerability that could allow hackers to inject malicious JavaScript into any website, all with just a single server-side tweak. This means users could be exposed to serious security risks without even realizing anything has changed.
A 17-year-old student gained unrestricted access to a UK school's network, discovering sensitive leadership documents and being able to reset passwords, delete accounts, and even wipe the entire network. The alarming vulnerability was uncovered when the student connected their laptop to the school's Active Directory domain, which surprisingly required no administrator authentication.
Imagine a simple game trick that could convince AI-powered browsers to hand over your login credentials - a vulnerability researchers have now exposed, leaving users at risk. By creating a malicious web page that changes an AI agent's sense of reality, hackers can bypass safety guardrails and gain access to sensitive information.
In a shocking experiment, a security firm created a fake AI skill that evaded detection by security scanners and reached a staggering 26,000 agents, including those on corporate accounts. The skill, designed to be harmless, was able to bypass every scanner it was tested on, raising serious concerns about the safety of AI marketplaces.
GitHub is stepping up its game to protect your code by blocking common attack patterns on pull requests, helping to prevent security vulnerabilities from untrusted code. As of June 18, 2026, its actions/checkout v7 will refuse risky fork checkouts by default, keeping your workflows safer from attacker-controlled code.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Cloudflare is teaming up with top browsers to launch Private Access Tokens, a game-changing protocol that helps websites tell humans from bots, filtering out abusive traffic while keeping user data safe. This innovative solution is a major step forward in tackling AI-powered traffic and ensuring a smoother online experience.
The traditional cybersecurity certification approach is no longer enough - we need a culture of lifelong learning where professionals continually upskill and reskill to stay ahead of evolving threats. Dan Magnotta, Senior Federal Business Development Manager at Hack The Box, is leading the charge towards an active-readiness revolution.
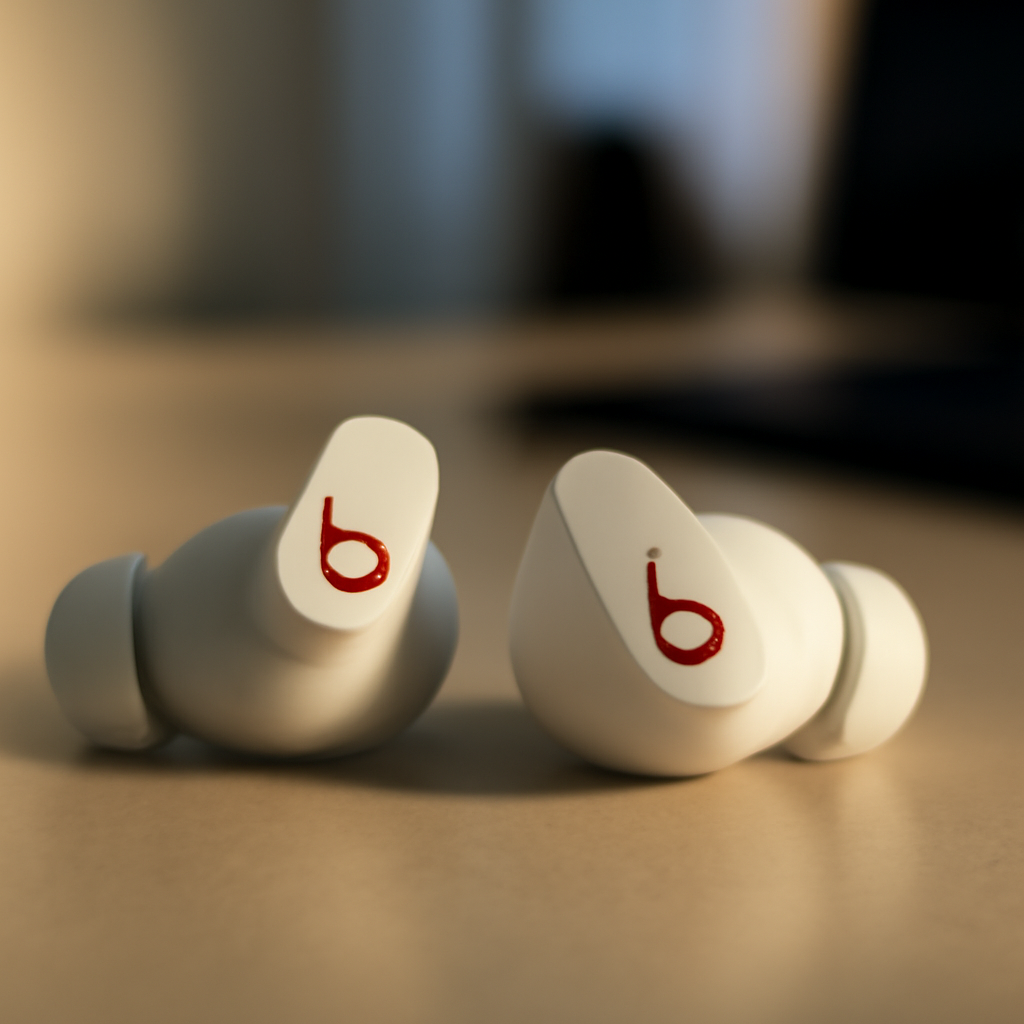
Apple just released a crucial update, Firmware 1B211, to fix a major flaw in Beats Studio Buds that let hackers eavesdrop on you through the earbuds' microphone - even if they're not paired with your device. This security patch protects you from unwanted listeners lurking within Bluetooth range.
Cybercriminals are getting anxious about the impact of AI tools on their illicit trade, and experts warn that now is the time for organizations to step up their cyber hygiene game with measures like timely patching, multifactor authentication, and passkey use. By prioritizing these defenses, businesses can stay ahead of emerging threats, including AI-assisted attacks.
When Roman Imankulov analyzed a suspicious Python project with his AI agent, it quickly flagged a malicious backdoor, saving him from a potentially disastrous mistake. The AI code review proved to be a crucial safeguard, alerting Imankulov to walk away from the tainted code.
Malware creators have found a sneaky way to evade detection by using NTFS junctions, a feature that's normally used to connect directories, to create hidden paths that can bypass security defenses like Microsoft Defender. By exploiting this vulnerability, attackers can cleverly disguise their malware's true location, making it harder to detect.
A researcher discovered that a simple code prompt to "fix this code" sparked a surprisingly swift and alarmed reaction from federal authorities regarding the Fable 5 model. However, the researcher disputes that this incident constituted a jailbreak, downplaying its significance.
Meet Johannes Link, a self-proclaimed AI skeptic who's taking a stand against AI-powered coding agents by weaponizing his own code - specifically, the Java property-testing tool jqwik - to disrupt their operations. His latest software update includes a clever anti-AI clause designed to throw a wrench in the works.