[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A shocking vulnerability in GitHub's AI-powered Agentic Workflows has been discovered, allowing attackers to expose private repositories with just a cleverly crafted issue and some plain English instructions - no coding skills or credentials required. This flaw lets hackers fetch and publicly share sensitive files, putting organizations at risk.
A new, ready-to-use bank-fraud tool called RedWing is being rented on Telegram, allowing even novice criminals to hijack Android users' phones and steal their banking information. This malicious kit is sold as a complete package, complete with step-by-step guides and how-to videos, making it alarmingly easy for scammers to get started.
A massive data breach at KDDI Corporation has put 12.2 million customer emails and 7.6 million passwords at risk, all stemming from a single unpatched vulnerability in a third-party software system. This staggering incident highlights the importance of robust cybersecurity measures, even for seemingly secure systems.
Meet CAI, a malicious botnet that's disrupting rival operations, swiping sensitive secrets, and mining cryptocurrency - all while eliminating competing malware to maintain its grip on compromised targets. This centralized worm is a powerhouse of credential theft and cryptomining, making it a force to be reckoned with.
GitHub's Agentic Workflows are vulnerable to a data leak threat, as researchers have demonstrated a clever technique called GitLost that tricks AI agents into spilling private content from secure repositories into public comments. All it takes is a simple public issue to launch the attack, with no stolen credentials or special access required.
Watch out for phishing scams targeting Facebook Business users - red flags include broken graphics, suspicious links, and unsolicited emails promising exciting opportunities. Experts warn that cybercriminals are getting sneaky, using legitimate-looking emails and Messenger chatbots to trick victims into taking action.
Cyber attackers have cleverly exploited Microsoft's device code login flow to hijack M365 accounts, using a sneaky collaboration-style lure to trick users into handing over session tokens without even needing to steal passwords. This clever tactic abuses the OAuth 2.0 Device Authorization Grant, designed for constrained devices, to bypass security measures like multifactor authentication.
China-aligned hackers are targeting universities in the US and Canada, exploiting vulnerable Roundcube webmail servers to gain access to sensitive physics and engineering departments with potential national security links. This latest campaign highlights the ongoing threat of email-based attacks and the need for robust server security.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Eight individuals targeted in Greece's Predator spyware scandal are taking a stand, suing the spyware maker for €8 million in moral damages after their devices were hacked between 2020 and 2021. Led by lawyer Zacharias Kesses, the group is seeking justice and accountability for the victims of this massive digital breach.
Spain's National Police have thwarted a daring escape plan by a suspected pro-Russian hacktivist, exposing his secret communications with terrorist groups and freezing his cryptocurrency assets. The suspect, allegedly part of the notorious CyberArmy of Russia Reborn and Z-Pentest groups, was caught after a months-long investigation sparked by a tip from the FBI.
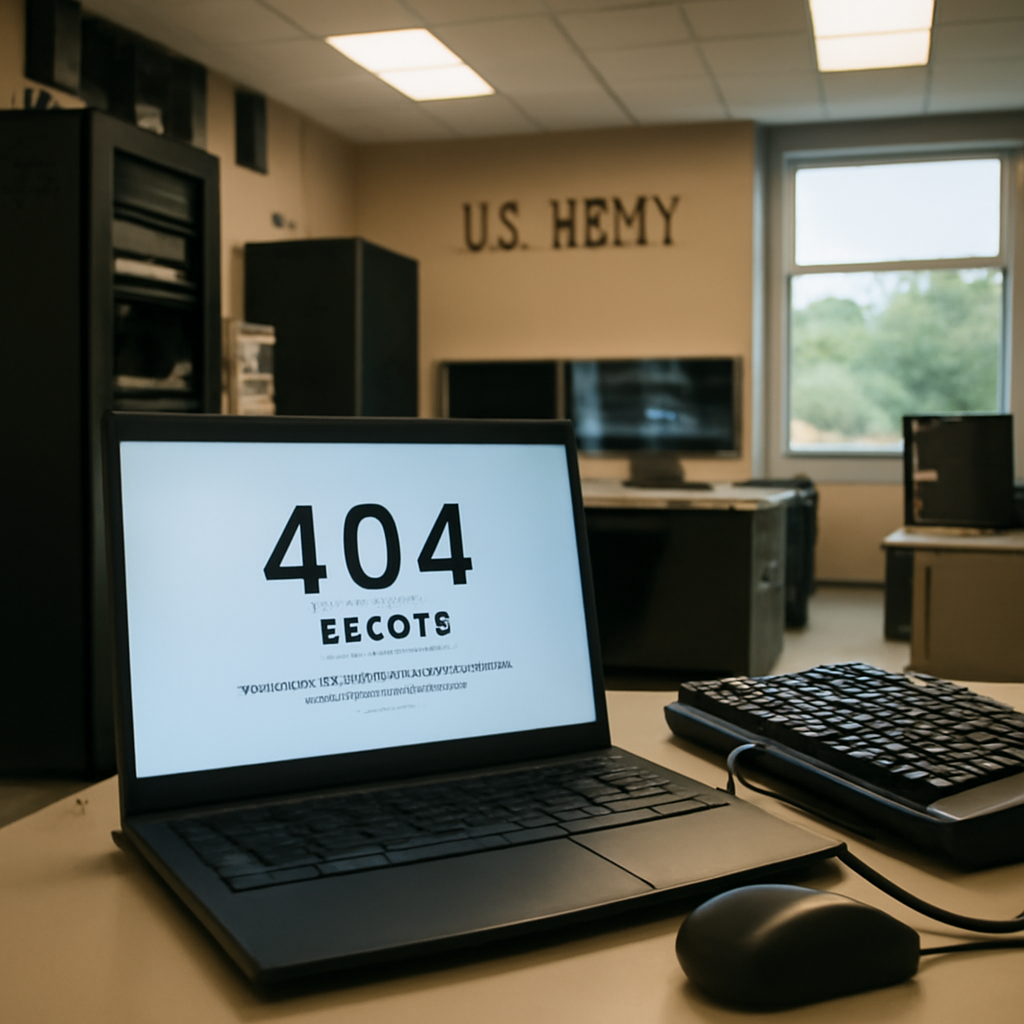
The US Army has confirmed that two of its websites, oil.army.mil and ai2c.army.mil, were recently hijacked in a 404 error page defacement campaign, displaying politically charged messages that denigrated high-profile figures and promoted a separatist cause. The incident was discovered by independent researcher Ronald Lovelace and reported to US Army officials.
China-aligned hackers have launched a sneaky attack on universities, exploiting two flaws in the popular Roundcube webmail client to steal credentials and gain persistent access. At least a few dozen universities are believed to be affected, with Proofpoint researchers confirming fewer than 10 intrusions so far.
In a brazen ransom email, the attackers boldly declared, "IMPORTANT: WE STOLE THE DATA, CONTACT UMMEDIATELY," leaving no doubt about their malicious intentions. The hackers infiltrated the retailer's network through a clever help-desk ploy, tricking staff into resetting passwords and gaining control of critical accounts.
Google is taking a stand against scammers, suing a group called Outsider Enterprise that uses its Gemini AI feature to create fake websites and scam people through text messages. The group, which operates on Telegram, offers phishing-as-a-service, making it easy for non-tech-savvy scammers to target victims.
Meet Scattered Spider, a notorious cybercrime collective that's evolved into a decentralized network of independent clusters, sharing tactics and tools to wreak havoc online. This fresh analysis by Group-IB shatters the traditional view of a single, unified gang, revealing a more complex and dynamic threat.
A newly disclosed 16-year-old Linux kernel vulnerability, dubbed Januscape, allows hackers to easily escape virtual machines and compromise their host systems - all with just a few clicks from within the guest system. This shocking security flaw, tracked as CVE-2026-53359, has been lurking in the kernel for nearly two decades.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Hacktivists aligned with Russia are wreaking havoc on UK organizations with denial-of-service attacks that may be simple, but have a significant impact by disrupting essential services. These attacks can overwhelm important websites and online systems, leaving people unable to access the services they rely on daily.
Beware of fake IT support scammers on Microsoft Teams who are tricking unsuspecting workers into installing malware by posing as tech support staff. These impostors are using the popular collaboration platform to deceive and compromise employee devices.
China-aligned hackers are exploiting vulnerabilities in Roundcube email servers to gain access to sensitive university networks, specifically targeting physics and engineering departments with national security ties. They've cleverly designed their attacks to fly under the radar, using tactics like compromised senders and spoofed domains to reach their targets.
With 775 exposed ColdFusion instances online, a newly patched flaw is being exploited by attackers, putting countless systems at risk. Adobe has urgently warned customers to apply updates immediately to protect against this and 10 other critical vulnerabilities.
A critical vulnerability in Tenda router firmware, tracked as CVE-2026-11405, allows hackers to bypass password verification and gain full administrative control of your device. This hidden backdoor puts your online security at risk, and a patch is still pending.
Imagine a ransomware attack that can think and act on its own - that's what Sysdig researchers recently observed, as an AI agent autonomously carried out a complex extortion operation with alarming speed and efficiency. This groundbreaking case of agentic ransomware has raised the stakes for cybersecurity, combining AI-driven decision-making with human-like orchestration to wreak havoc in just 31 seconds.
Beware of fake IT support calls on Microsoft Teams - hackers are using convincing tactics, including a phishing email with a malicious PDF, to trick victims into downloading the potent EtherRAT malware. They impersonate system administrators to gain your trust, making it crucial to stay vigilant.
Iran-linked hackers have launched a sophisticated cyber attack campaign, dubbed Cavern Manticore, targeting Israeli organizations, particularly in the IT and government sectors, using a cutting-edge .NET-based framework. This threat cluster is affiliated with Iran's Ministry of Intelligence and Security, and its tactics overlap with other notorious groups like MuddyWater and Lyceum.