[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
NHS Forth Valley is taking immediate action to investigate a data breach that exposed the personal details of around 150 women who used local maternity services, after a staff member accidentally sent the information to a personal email account. The breach has been contained, with the staff member confirming they've deleted the data, but an internal probe is underway to ensure no further risk.
A ransomware negotiator turned double agent, Angelo Martino, has been sentenced to 70 months in prison for betraying his clients and working with BlackCat to drive up ransoms for personal gain. Martino's shocking deceit involved selling out his clients' confidential negotiating positions to the very cybercriminals he was hired to thwart.
A single coordinated attack exploited the Ill Bloom flaw on May 27, draining a staggering $3.1 million from 431 wallets in a single day. This shocking theft was made possible by a weak random-number generator in certain wallet software that created easily guessable recovery phrases.
A former ransomware negotiator, Angelo Martino, has been sentenced to 70 months in prison for his role in a string of BlackCat ransomware attacks that targeted multiple victims between 2023 and 2025. Martino's guilty plea brings to justice a key player in the notorious ALPHV ransomware gang.
In a major crackdown on global cybercrime, Interpol's Operation First Light has led to the arrest of 5,800 individuals and the seizure of $293 million, highlighting the power of international cooperation in the fight against online scams. This huge success shows that when countries work together, they can make a real difference in keeping people safe from cyber threats.
A trusted ransomware negotiator turned double agent, Angelo Martino betrayed his clients, funneling their confidential info to BlackCat affiliates and lining his pockets with a share of their ransoms, leaving a trail of devastated businesses in his wake. His deceit raked in $75.3 million for him and his co-conspirators.
A US county recently made a shocking decision to pay $1 million to cyber extortionists, despite lacking concrete proof that the hackers had deleted the stolen data, after a month-long negotiation that began with a hefty demand of $3 million. The extortion group, Kairos, had threatened to leak sensitive information, prompting the county to make a counteroffer that was ultimately outweighed by the threat.
Davide Beatrici, a leading developer of the Mumble app, has denied allegations of sabotage against the OpenMandriva Linux Project, claiming his actions were deliberate but not malicious. He admitted to deleting key repositories and pushing a package, but insists his moves were targeted, not hurtful.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A malicious npm package, downloaded a staggering 50,000 times weekly, was briefly infected with code that stole cryptocurrency wallet private keys and sensitive seed phrases, putting countless developers at risk. The attack was launched after a contributor's GitHub account was compromised, allowing the hackers to spread the poisoned code across multiple projects.
Microsoft has uncovered a highly destructive backdoor, dubbed GigaWiper, which poses a triple threat to Windows systems, allowing attackers to silently spy and destroy machines in three different ways. This multi-purpose threat doesn't just crash systems - it gives attackers the power to choose how and when to render a machine irrecoverable.
Cyber attackers are using sneaky tactics, leveraging old or compromised GitHub accounts, to secretly map out corporate organizations and steal sensitive data. They're exploiting loopholes with automated tools and stolen tokens to quietly gather intel from GitHub APIs.
In a major global sting operation, INTERPOL's Operation First Light 2026 led to the arrest of 5,811 individuals and the seizure of $293 million in illicit assets, highlighting the growing threat of transnational social engineering and money-laundering schemes. This coordinated effort involved 97 countries and territories, and resulted in the identification of over 142,000 victims and 15,606 suspects.
Helix Group hackers are using clever voice phishing tactics, often impersonating managers, to trick victims into handing over account access. They use a simple yet effective playbook, starting with a convincing phone call that sets the stage for a device-code phishing scheme.
Meet Forg365, a sneaky new phishing platform that uses AI to make it easy for hackers to target Microsoft 365 accounts and steal sensitive info. This phishing-as-a-service operation offers a range of tools, including AI-generated lures, to help cybercriminals launch convincing attacks.
Criminals are now leveraging AI to create malicious software, as seen in a recent case where an attacker used an AI-assisted PowerShell script to infiltrate an Active Directory environment. This emerging threat, dubbed "vibe coding," allows attackers to generate software by simply prompting a large language model in plain language.
Cyberattacks surge by 40% during holiday periods, with summer being a prime target due to lighter staffing and slower business operations that create the perfect storm for cybercriminals to exploit. When teams are on vacation, attackers see an opportunity to probe for vulnerabilities and test response times.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Ransomware attackers have taken a disturbing new tactic, using a malicious kernel driver signed by Microsoft to disable endpoint defenses and wreak havoc on systems. The PoisonX driver, identified as g11.sys, is a game-changer in ransomware operations, making it harder for security teams to detect and respond to threats.
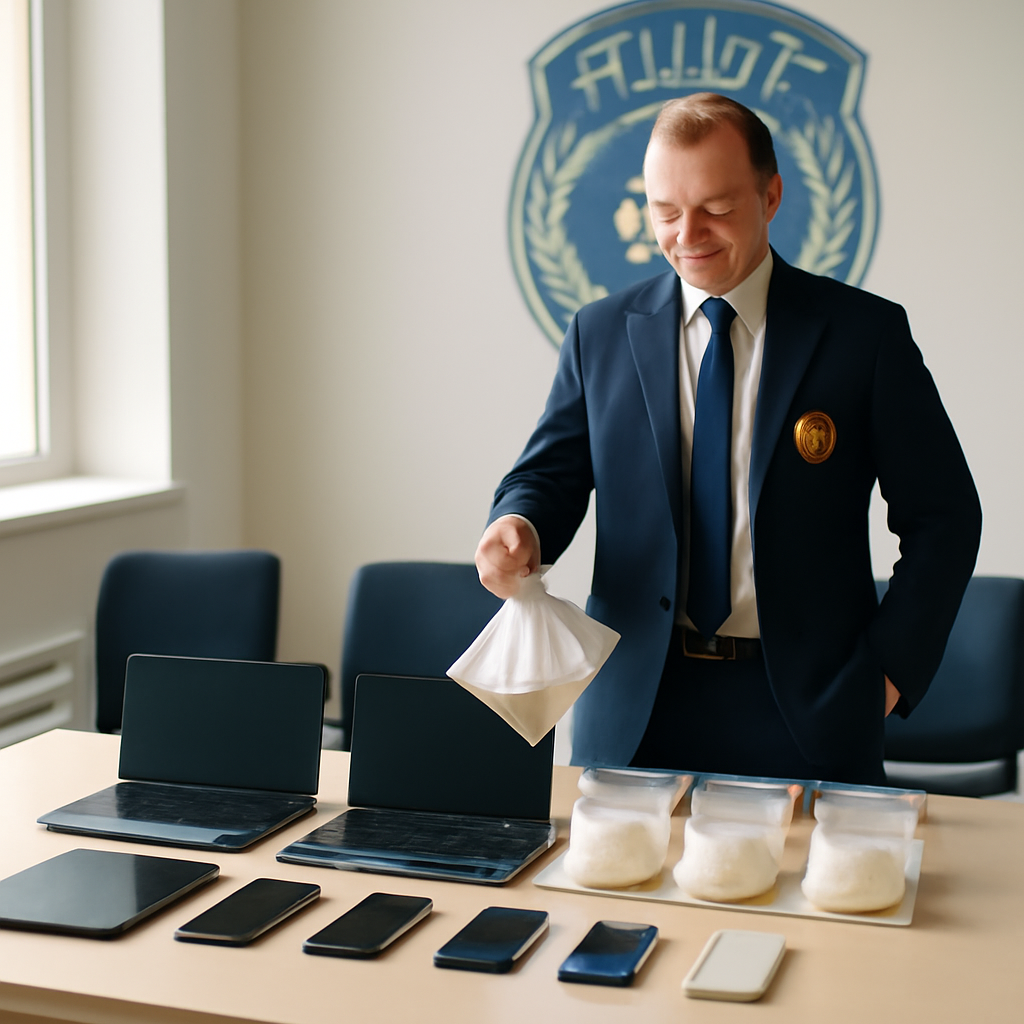
In a major global sting operation, authorities in Eswatini seized 240 electronic devices, foreign currency, and a stunning replica of a Brazilian police station - complete with fake uniforms and equipment - as part of Interpol's Operation First Light 2026, which has led to 5,800 arrests worldwide. This massive crackdown on cybercrime was made possible through collaboration between 97 countries and territories, with support from Europol, Aseanapol, and GGCPol.
A recent ESET study uncovered a staggering number of malicious AI agents hiding in plain sight within open-source repositories, with tens of thousands of suspicious instances and thousands more flagged as outright malicious. This alarming trend suggests a rapidly escalating threat landscape, with cyber attackers leveraging AI to plan, execute, and scale their attacks.
On March 17, 2026, AssuranceAmerica detected a security breach that put 6.9 million driver records at risk, allegedly caused by a malicious attack on one of its employees on March 16, 2026. The company has begun notifying affected individuals about the breach.
A shocking 773,087 unique IP addresses linked to SmartProxy were found in a public IP dataset, hinting at a massive residential proxy botnet. This staggering overlap raises serious concerns about the scope of a malicious operation dubbed Lurking Lizard.
A recent series of university server breaches, attributed to a group called UNK_MassTraction, has exposed vulnerabilities in North American higher-education institutions, with potentially dozens more affected. The breach, linked to a flaw in Roundcube, is believed to be an ongoing campaign.
Mount Royal University recently fell victim to a cyberattack that compromised sensitive data, with hackers accessing and stealing files from the university's network before deleting them. The breach, which occurred on June 17, has disrupted multiple university systems and may take weeks to fully recover from.
Beware of malicious software development kits (SDKs) masquerading as legitimate Paysafe, Skrill, and Neteller tools, designed to secretly steal your credentials. Researchers uncovered 17 fake packages on popular platforms, putting users at risk of credential theft.