[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Citrix has just revealed a third critical NetScaler zero-day vulnerability, CVE-2026-88779, which can cause a denial of service in SAML-enabled deployments, and security experts warn it's painfully easy to trigger. This high-severity defect is the latest in a string of actively exploited NetScaler vulnerabilities.
A recent Pentagon breach left a staggering 3 million people vulnerable after highly sensitive data was exposed for months due to undetected unauthorized access. This alarming incident serves as a stark reminder of the importance of robust data security measures.
Citrix NetScaler is under active attack, with hackers exploiting a newly discovered vulnerability that can cause denial of service with just a single specially crafted request. The flaw, known as CVE-2026-88779, affects certain NetScaler deployments configured for single sign-on authentication.
Hackers are on the hunt for Rejetto HFS servers with a critical flaw that lets them forge sessions, take over accounts, and execute remote code - and it's crucial to update to version 3.2.1 ASAP to avoid falling victim. This vulnerability, known as CVE-2026-61500, was patched in July, but attackers are actively scanning for affected servers.
The FBI has scored a major win in the fight against cybercrime, arresting multiple suspects linked to the notorious ShinyHunters hack, and vowing to leave no stone unturned in bringing all responsible individuals to justice. The operation is ongoing, with the bureau working closely with law enforcement partners to crack down on the group.
US water systems are under siege by cyber threats from hostile nations like China, Russia, Iran, and North Korea, as well as ransomware groups, putting our critical infrastructure at risk of a nationwide public-health crisis. This summer's alarming attacks on water systems in 12 states by Iranian hackers exposed the vulnerability of our water infrastructure to foreign adversaries.
A major security flaw in Bromcom's legacy single sign-on system has led to a significant data breach, exposing email addresses of users across the UK's education sector. The incident, identified on September 6, affected a legacy registration mechanism still in use despite being superseded.
A massive data breach has hit Denmark's Central Population Register, compromising sensitive personal info for a whopping 8.8 million people - that's nearly 80% of the country's population! Names, addresses, dates of birth, and more are now at risk.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Researchers have uncovered a new Spectre v2 variant, called Branch Target Reuse (BTR), which can extract sensitive data, including root password hashes, from Intel machines running Linux in just minutes. This attack leverages a clever exploit that takes advantage of a desynchronization in modern CPUs.
Malicious backdoors are sneaking into telecom systems by masquerading as regular email traffic, making them nearly undetectable. Researchers at Rapid7 uncovered an implant family called AVERAT that cleverly disguises itself as legitimate mail activity on TCP port 25 and SMTP.
South Korea's financial sector is reeling after a string of devastating data breaches at major banks, including Shinhan Bank and Kookmin Bank, which compromised the sensitive information of over 144,000 customers. The alarming incidents have triggered an emergency response from the Financial Services Commission, with officials launching urgent on-site investigations and sharing critical intelligence to contain the damage.
Meet ClingSTUN, a sneaky Linux proxy backdoor that's exploiting known flaws in unpatched IoT devices to turn them into remotely controlled proxy nodes, allowing hackers to hijack your network. FortiGuard Labs has tracked 24 vulnerabilities so far, and it's crucial to stay ahead of this threat.
Malware operators have seized on a critical flaw in the Realtek Jungle SDK (CVE-2021-35394) to spread the Cling botnet, exploiting the vulnerability to infect devices and turn them into unwitting accomplices. By cleverly hijacking the ordinary STUN protocol, Cling creates a stealthy command-and-control channel to issue instructions and disguise its malicious activities.
Citrix is warning of targeted attacks exploiting a newly discovered zero-day flaw, CVE-2026-88779, a high-severity memory buffer issue that could disrupt services for vulnerable NetScaler ADC and NetScaler Gateway customers. The company has urged affected users to act quickly to protect themselves from potential denial-of-service attacks.
A major breakthrough in the fight against cybercrime: US authorities have arrested Anibal Alexander Canelon Aguirre, the alleged mastermind behind the notorious Ploutus ATM malware that drained over $5.4 million from banks and credit unions nationwide. The suspect, also known as "Prometheus" and "The Engineer," was added to the FBI's Most Wanted list in 2026 and now faces charges of conspiracy to commit bank fraud.
A recent breach at Frontline Education, a leading provider of K-12 administration software, exposed sensitive staff data after a vulnerability in a third-party software product was exploited, allowing unauthorized access to part of its environment. The breach was discovered nearly two months after it occurred, and Frontline Education quickly sprang into action to investigate and remediate the issue with the help of a cybersecurity firm.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
A critical zero-day vulnerability, CVE-2026-88779, has been exploited in targeted attacks, causing concern for Citrix NetScaler ADC and Gateway users. This memory overflow flaw can lead to denial-of-service attacks when specific deployment conditions are met.
Citrix has rolled out emergency patches to shield NetScaler from zero-day attacks that can cause Denial of Service chaos, and you should update ASAP to avoid getting caught in the crossfire. The newly discovered vulnerability, CVE-2026-88779, has already been exploited in targeted attacks, earning a scary CVSS score of 8.7.
Meet TA419, a China-aligned group with a keen interest in U.S. AI policy, targeting experts at think tanks, universities, and law firms with clever phishing scams. Their tactics include impersonating prominent economists, policymakers, and even an Anthropic employee to get the intel they want.
The detention of Saif al-Din Khader, a suspected member of the notorious ShinyHunters extortion group, has given the FBI a crucial breakthrough in their international probe, with his cooperation expected to help track down other hackers. Khader, who goes by the online aliases "Rey" and "ReyXBF", was taken into custody in Jordan and is now working with authorities to bring down the group.
A Jordanian suspect, known online as Rey, has been detained and is cooperating with the FBI in a significant breakthrough against the notorious ShinyHunters extortion operation. This development could be a major blow to the hackers, with the suspect's cooperation potentially leading to the arrest of others involved.
Warlock, a suspected China-linked threat actor, has launched targeted ransomware attacks on at least four organizations, including critical infrastructure operators, via exploited flaws in on-premises Microsoft SharePoint Server deployments. The victims, located in Portuguese- and Spanish-speaking countries, span across Europe, Africa, and Latin America.
The Technical University of Denmark is investigating a serious data breach that may have compromised the personal info of 200,000 users, sparking concern and uncertainty for those affected. University Director Bjarke Bak Christensen expressed deep regret, saying it's a significant attack that's causing worry for those whose data may be at risk.
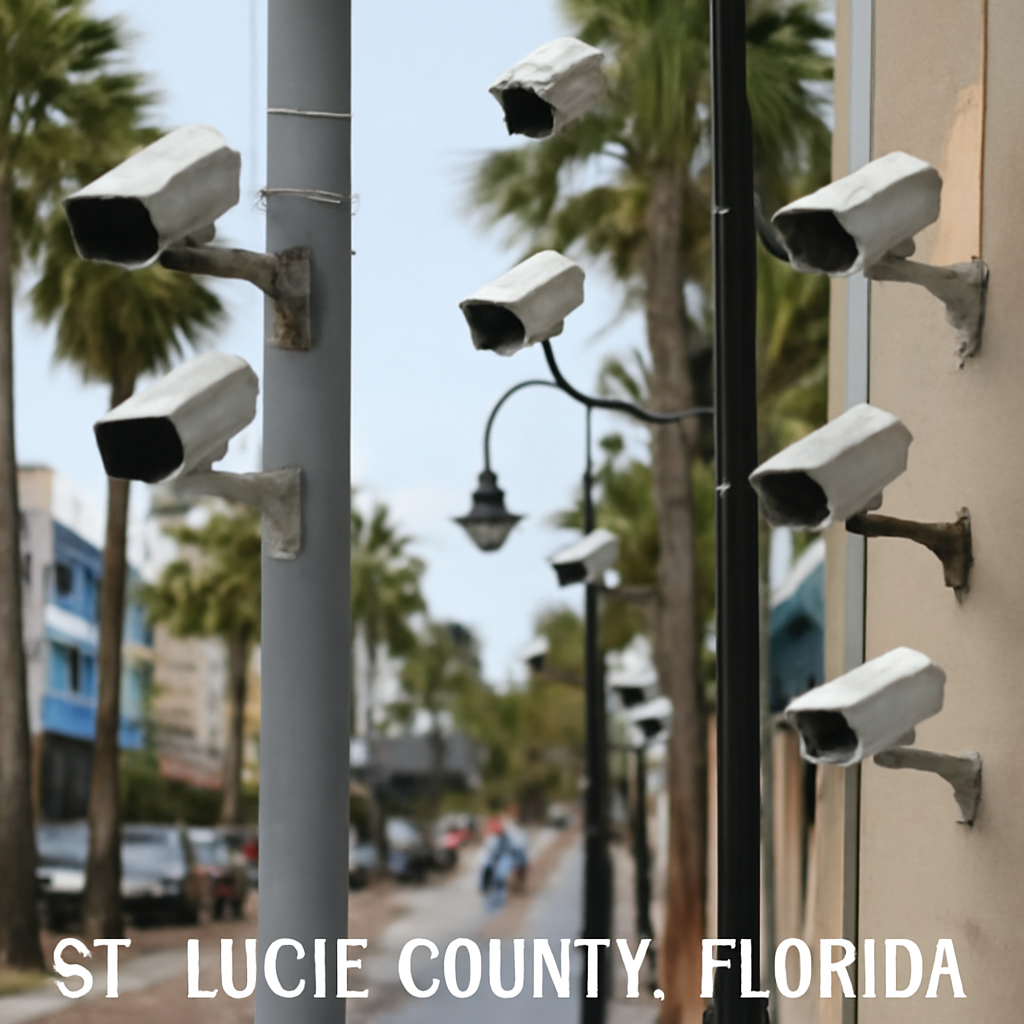
In a bizarre discovery, St. Lucie County officials stumbled upon a dozen rogue surveillance cameras with no clear owner or permit - a concerning mystery in public spaces. The unknown cameras have raised questions about accountability and safety.