[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Imagine the lights going out at your local hospital or your commute being held hostage — a new U.S. indictment alleges 19‑year‑old Thalha Jubair is a core member of Scattered Spider tied to at least $115 million in ransoms that hit hospitals, transit and retailers. The case shows how low‑tech tricks like SIM swaps and social engineering let agile, global criminal crews cause massive, real‑world harm.
Boyd Gaming has confirmed an unauthorized actor removed data from its systems — a worrying development for employees and guests that raises urgent questions about what types of information were exposed and how many people were affected. The company says it’s working with forensic experts and law enforcement, but clearer, timely disclosures and concrete protections will be crucial to restore trust.
European police dismantled an alleged €100 million crypto fraud ring this week, arresting five suspects and shutting down fake platforms, token launches and wallets that duped investors. The case shows how cross-border forensics can stop big scams — and why you should always verify platforms and be wary of returns that sound too good to be true.

Kaspersky warns that RevengeHotels has resurfaced, now using AI to churn out highly convincing fake booking pages and tailored phishing messages that quietly steal card details. Travelers and hotels should double-check booking links, vet payment workflows, and monitor transactions closely to avoid getting burned.

A stealthy, Iran-linked cyber actor called Nimbus Manticore is quietly shifting from remote spying to targeting European aerospace, telecom and defense suppliers — and its patient, surgical intrusions threaten intellectual property, supply chains and national security unless industry and governments boost defenses and share threats quickly.
Jaguar Land Rover’s extended shutdown has left thousands of workers and local businesses nervously counting the cost — not just idle factories but paychecks and holiday plans at risk. With no restart date, families and suppliers face mounting uncertainty as analysts warn the disruption could hit the company and regional economies hard.

Think that job email was real? Researchers warn Iran‑linked hackers are using fake recruitment pages to deliver MiniJunk backdoors and MiniBrowse stealers to European aerospace and related sectors, so organizations and applicants should harden hiring workflows and treat unsolicited offers with caution.
Stellantis warns a third‑party supplier may have exposed customer personal data, leaving millions wondering what may actually means. Customers deserve clear answers about who was affected, what was leaked, and what protections will be offered.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Jaguar Land Rover’s production pause — now extended to October 1 — lays bare how fragile global supply chains can halt both everyday SUVs and luxury icons, snarling deliveries and unsettling local jobs. As the industry scrambles for fixes from regional suppliers to chip investments, this pause is a wake-up call to rethink how cars are built in an age of electrification and scarce parts.

Stellantis says a third-party vendor hack exposed some customer names and email addresses—no financial or vehicle data—but the breach still leaves customers and regulators wondering whether outsourcing kept their information safe. Even seemingly low-risk leaks can fuel phishing and fraud, underscoring the need for stronger vendor security and clearer accountability.
President Trump says Michael Dell is part of a consortium — reportedly including Larry Ellison and the Murdochs — aiming to buy TikTok’s U.S. operations, reigniting a high-stakes debate over data security and who controls a platform used by tens of millions every day.

When ransomware knocked a French museum offline and thieves made off with $705,000 in gold, it became painfully clear that cyberattacks can enable real‑world heists — a wake‑up call for museums and small institutions to protect both their networks and their treasures.
New research shows Russian state-linked groups Gamaredon and Turla are sharing malware and techniques to scale espionage against Ukrainian government, military and aid organizations — a troubling coordination that widens Moscow’s reach while making defense and attribution much harder.

About 194,000 people were affected when the New York Blood Center disclosed a breach exposing Social Security numbers, IDs, bank details and in some cases health information — a stark reminder that even trusted health organizations can become targets. If you were notified, enroll in offered monitoring, watch your accounts closely, and tighten passwords and fraud protections now.

SonicWall revealed threat actors accessed cloud-stored firewall preference files for about 5% of its devices — a small slice but a big risk, since exposed configurations act like blueprints that can speed and stealth targeted attacks. Now’s the time to audit vendor backups, rotate credentials, and enforce customer-controlled encryption to limit fallout.
Cybersecurity researchers found two malicious PyPI packages that delivered the SilentSync RAT to Windows machines, enabling remote command execution, file theft and screen capture. Treat your dependency tree like an attack surface—audit packages, pin versions and lock down CI to stop supply-chain intrusions.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Insight Partners says a ransomware attack exposed personal data for more than 12,000 people — employees, former staff and limited partners — sparking urgent questions about investor privacy and the safeguards venture firms must have in place. This breach is a wake-up call: clearer disclosure, stronger cyber defenses and tougher due diligence are now essential for investors, founders and funds alike.

A former Florida deputy is reportedly at the center of a sprawling Russian-backed fake-news operation that’s launched 200+ phony local sites, using AI-aided copy and clever localization to spread lies and sway voters ahead of 2024.

A newly unsealed court filing alleges a TaskUs employee sold Coinbase customer records for about $200 each, potentially linking a vendor insider to the 2023–24 breach and raising urgent questions about third‑party trust. If true, it’s a stark reminder that outsourcing can turn a single insider into a major security risk.
A court reversed an earlier plea deal and sentenced Conor Fitzpatrick, founder of BreachForums, to three years — a decision prosecutors say holds platform operators accountable after the site turned stolen data into a lucrative hub that harmed thousands.
Conor “Pompompurin” Fitzpatrick, the 22‑year‑old former admin of BreachForums, was resentenced to three years in prison after pleading guilty to access‑device conspiracy and possession of CSAM. The sentence signals that law enforcement can reach the digital underground — but it also highlights how much work remains to shut down the markets that fuel identity theft and abuse.
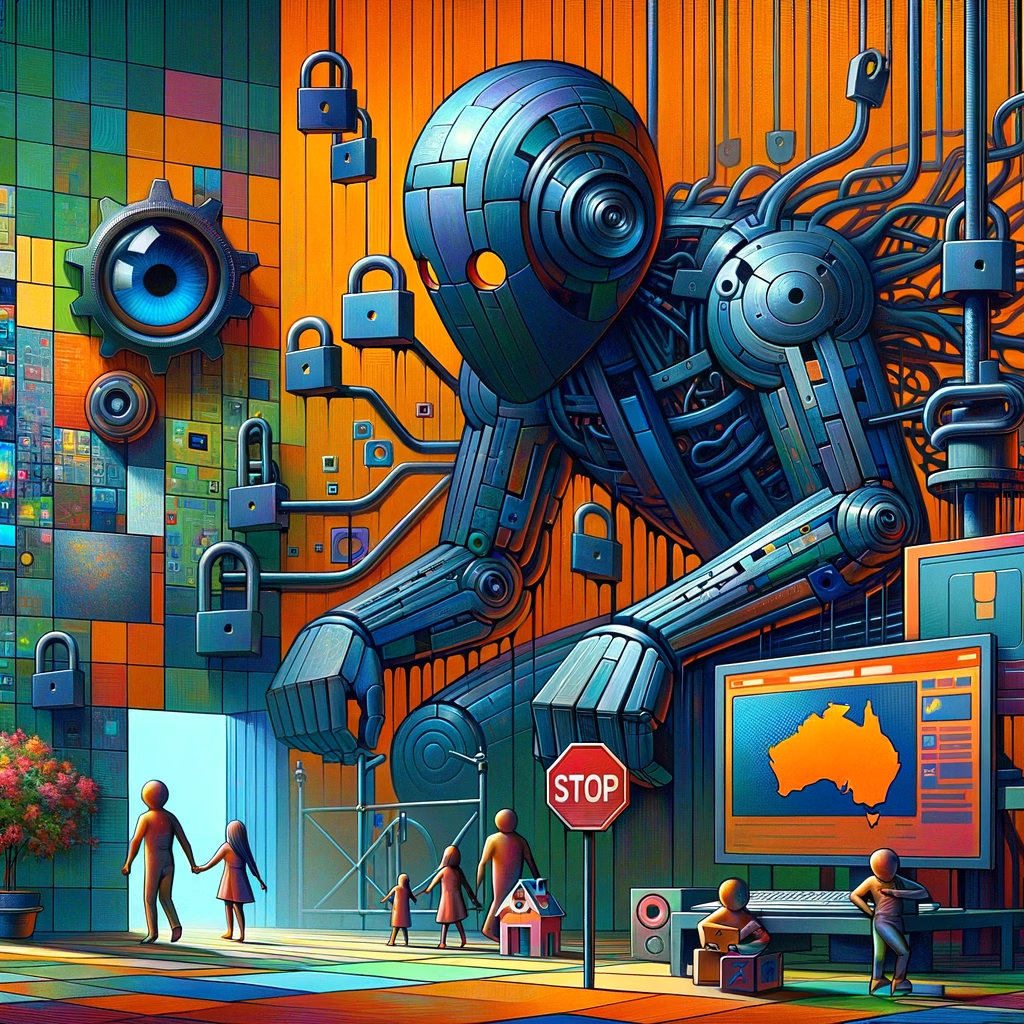
Australia has handed Big Tech a thorny challenge: prove users are 16+ using layered age checks without turning signups into surveillance. Expect a scramble of tech experiments, policy fights and messy trade‑offs as platforms race to balance child safety, privacy and practicality before the December 10 deadline.
Fifteen ransomware gangs publicly claimed retirement on BreachForums — dramatic, but experts say it may be more theater than farewell. Don’t relax: rebrands, affiliate migrations and exit scams are common, so keep backups, MFA, segmentation and solid incident‑response readiness.
Luxury shoppers were jolted this week after a reported breach tied to ShinyHunters exposed millions of email addresses linked to Gucci and Alexander McQueen. Change your passwords, enable MFA, and watch for phishing while the brands investigate and disclose what was taken.