[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
UK higher education institutions are under cyber attack, with a staggering 98% reporting breaches in the past year - a sharp jump from 91% the year before. This near-universal vulnerability raises serious concerns about the sector's online security.
Meet DEEP#DOOR, a sneaky Python-based backdoor framework that's harvesting browser and cloud credentials by exploiting a tunneling service, and learn how it infiltrates systems through a clever sequence of stealthy steps. This sophisticated threat starts with a simple batch script that disables Windows security controls and ends with a fully featured Remote Access Trojan (RAT).
Phishing attacks remain a major threat, with nearly half of UK businesses falling victim to these scams in the past year, and a staggering 85% of breaches involving phishing as the primary entry point. These attacks often rely on human error, using tactics like impersonation emails and fake logins to trick staff into handing over sensitive information.
A cPanel bug, tracked as CVE-2026-41940, was exploited in the wild as a zero-day vulnerability before a patch was released, with attackers making execution attempts as early as February 23, 2026. The flaw forced vendors and hosting providers into emergency mitigation, with cPanel finally releasing a fix on April 28, 2026.
In a major crackdown on crypto scams, a global operation led by Dubai Police has arrested 276 suspects and shut down nine fraudulent investment centers, dealing a significant blow to scammers who thought they were safe from law enforcement. This coordinated effort with US, Chinese, and Thai authorities has brought global justice to victims of these crimes.

A recent investigation by TrendAI has uncovered a concerning China-linked espionage campaign, with a novel spy group infiltrating over a dozen critical networks across Poland and Asia, leaving behind a lingering threat that's experts' biggest worry. The threat group, tracked as Shadow-Earth-053, has been actively compromising networks since December 2024.

A fintech firm's most sensitive secrets were left exposed in a shared spreadsheet, with a password that was embarrassingly simple - literally a combination of the company's name and the year. The shocking discovery was made by Stanislav Kazanov during a routine compliance audit, when he stumbled upon a widely accessible SharePoint folder containing a file ominously titled Prod_DB_Root_Creds_DO_NOT_SHARE.xlsx.
Security researchers have uncovered a supply-chain attack that compromised four official SAP npm packages, allowing attackers to extract sensitive secrets from CI runner memory. The affected packages, which support SAP's Cloud Applications, have been deprecated on NPM and users are urged to update to secure versions.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
In a massive global crackdown, US and international authorities have dismantled a notorious network of cryptocurrency scam centers, arresting at least 276 individuals across the Middle East and Southeast Asia. This historic operation marks one of the largest US-assisted enforcement efforts against transnational cybercrime networks to date.
A shocking security vulnerability has been uncovered in a popular WordPress plugin, leaving over 70,000 sites open to backdoor attacks that can inject malicious code on demand. The issue was discovered in the Quick Page/Post Redirect plugin, which was infected with a hidden backdoor five years ago.
Hackers are taking advantage of two major flaws in the Qinglong open-source task scheduler, CVE-2026-3965 and CVE-2026-4047, which can be combined to gain remote control of vulnerable systems. These authentication-bypass vulnerabilities affect Qinglong versions 2.20.1 and older, and have been exploited for cryptomining deployments.
UK Biobank data was mysteriously listed for sale on Alibaba, but thankfully, the listings were swiftly removed with the help of the UK and Chinese governments, and no sales were made. The sensitive data, which includes genomic information, health records, and medical imaging, had been shared with researchers but was de-identified to protect participants' identities.

Microsoft's latest patch isn't enough to stop Russian spies from exploiting a Windows flaw, leaving sensitive information vulnerable to exposure. The incomplete fix is linked to a previously patched vulnerability from February, highlighting the urgent need for a more robust solution.
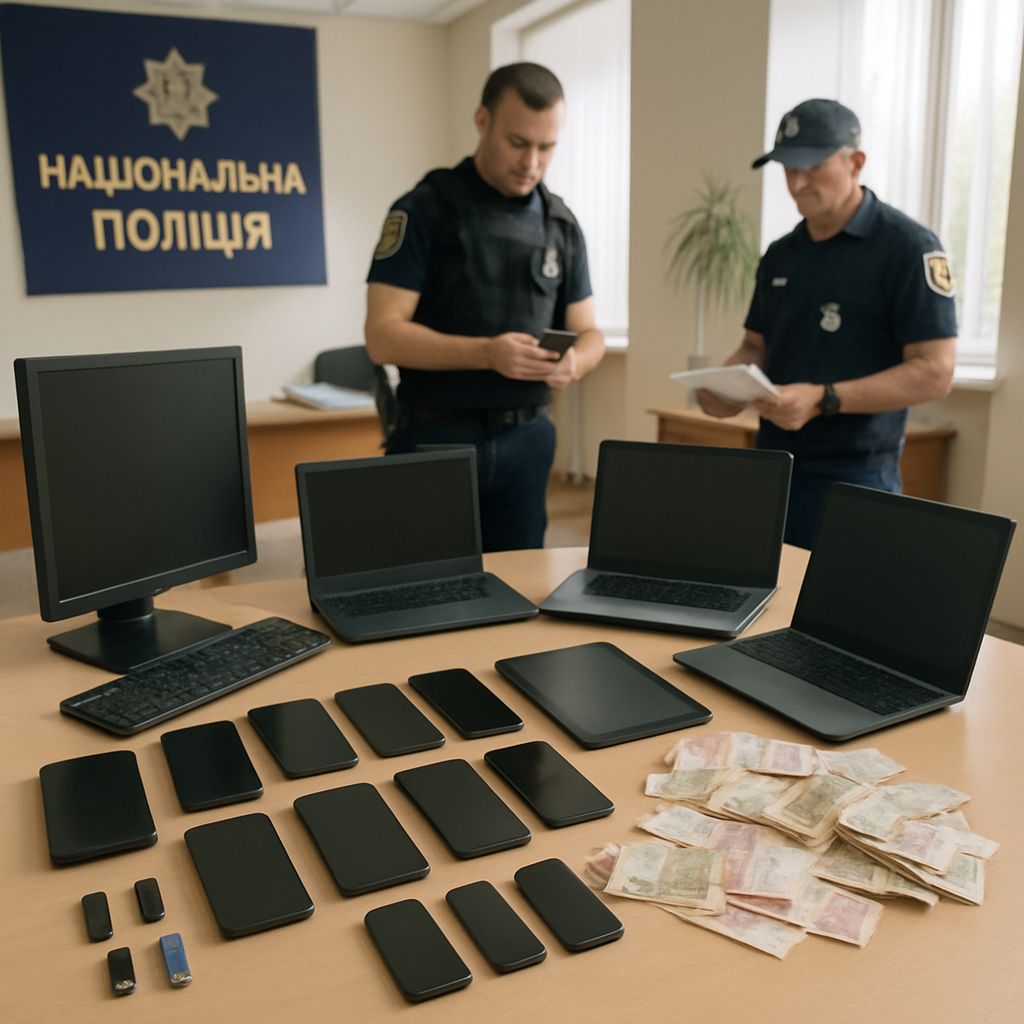
Ukrainian police have cracked down on a massive Roblox account hacking ring, arresting three suspects who hijacked over 610,000 accounts and resold them for a staggering $225,000 profit. The bust in Lviv also yielded a haul of $35,000 in cash and dozens of digital devices.
A new supply-chain attack campaign, dubbed mini Shai-Hulud, is targeting SAP-related npm packages, delivering credential-stealing malware that threatens JavaScript and cloud applications. This sneaky attack puts sensitive data at risk, and experts are warning of a potentially massive impact.
Security researchers have uncovered a sneaky malware campaign targeting developers, involving a malicious npm package called @validate-sdk/v2 that's designed to steal sensitive secrets, including crypto-wallet credentials. This tainted package, linked to a North Korean threat actor, was cleverly disguised as a utility SDK for legitimate tasks like hashing and validation.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Ransomware is wreaking havoc on the manufacturing sector, responsible for a staggering 90% of total cyber losses - despite accounting for just a small fraction of claims. When ransomware strikes, the financial blow is severe, highlighting the urgent need for robust security measures.
A massive €50 million crypto investment fraud ring has been dismantled thanks to a joint investigation by Austrian and Albanian authorities, supported by Europol and Eurojust, resulting in the arrest of 10 suspects and the seizure of cash and electronic devices. The alleged scammers, operating from call centres in Albania, left a trail of financial devastation across Italy, Germany, Greece, Spain, Canada, and the UK.
Researchers have uncovered a sneaky malicious npm campaign, dubbed PromptMink, linked to North Korean hackers Famous Chollima, which targets crypto developers with fake utility packages that secretly steal sensitive info and funds. The campaign's clever tactics even involve an AI-assisted code commit to fly under the radar.

A single misstep with a trial AI tool led to a major breach: a Vercel employee's casual OAuth grant to Context.ai created a lasting vulnerability that attackers exploited when Context.ai was compromised. This incident highlights the alarming ease with which AI-driven tools can become enterprise security weak spots.
Imagine 2.9 billion personal login details floating around in the dark corners of the internet, vulnerable to exploitation by cybercriminals - that's the staggering reality revealed by a recent threat intelligence analysis. This massive cache of compromised credentials, tracked globally in 2025, is a goldmine for hackers leveraging stolen logins, malware, and AI to wreak havoc.
Researchers uncovered a critical flaw in Vect Ransomware that unexpectedly turns it into a data-destroying wiper, permanently destroying files over 128KB instead of encrypting them. This shocking misfire stems from a faulty ChaCha20‑IETF implementation that strips away crucial security protections.
A shocking security breach occurred when a 27-year-old domain was transferred from a GoDaddy account to another customer without any authentication checks, putting a non-profit at risk. The alarming transfer was completed in just four minutes, raising serious concerns about GoDaddy's domain transfer process.

The US Cybersecurity and Infrastructure Security Agency (CISA) has flagged two major vulnerabilities, including a critical flaw in ConnectWise ScreenConnect and a Microsoft Windows Shell bug, as actively exploited by hackers. These flaws could allow attackers to execute remote code, access confidential data, and compromise critical systems.