Emerging Threats

Brightly-lit office workstation with browser showing redirect chain and cup.

Google DoubleClick Exploited in Malspam Campaign Delivering DesckVB RAT

Cyber attackers are cleverly using Google's DoubleClick to disguise malicious emails, routing victims through a legitimate domain that often flies under the radar of security tools. By exploiting this trusted platform, hackers can easily trick people into downloading the DesckVB RAT malware.

Analyst 207
Smartphone with notification on screen, surrounded by everyday objects.

Google Gemini on Android Exposed to Notification-Based Hijacking

Researchers have uncovered a vulnerability in Google Gemini on Android that allows hackers to hijack the assistant using a single hostile notification, no malicious app required. This shocking exploit lets anyone able to push a notification to a device deliver a payload and take control.

Analyst 207
Industrial setting with fuel storage tanks and an automatic tank gauge system.

Hackers Target Fuel Tank Monitoring Systems with Cyberattacks

Cyber attackers are launching targeted strikes on internet-exposed fuel tank monitoring systems, allowing them to modify and manipulate critical infrastructure. These compromised systems, known as automatic tank gauges, remotely track fuel levels, temperatures, and leaks, making them a prime target for malicious actors.

Analyst 207
Rows of computer servers and networking equipment in a brightly lit server room, conveying disruption and vulnerability.

HTTP/2 Bomb Attack Disrupts Web Servers in Seconds

A home computer on a typical 100Mbps connection can cripple a vulnerable server in mere seconds using a new technique called the HTTP/2 Bomb, which cleverly combines two known weaknesses in HTTP/2 server configurations. This potent attack can be unleashed quickly, leaving servers inaccessible.

Analyst 207
Smartphone on a neutral surface with blurred background.

CISA Warns of Active Exploits Targeting Android, Linux Flaws

A high-severity Android flaw, CVE-2025-48595, is being actively exploited in targeted attacks, allowing hackers to gain increased privileges without needing any user interaction. This critical vulnerability affects Android 14-16 and has prompted CISA to add it to its list of Known Exploited Vulnerabilities.

Analyst 207
Cluttered computer desk with laptop, gaming accessories, and scattered game CDs in a dimly lit home gaming room.

Malware Hidden in Hentai Games Exposes Users to Full System Compromise

Beware of hentai games that seem too good to be true - a new malware campaign has been discovered that hides in these games and can fully compromise your system. Hundreds of users, mainly in Russia, Brazil, Germany, and Vietnam, have already fallen victim to this threat, dubbed Argamal.

Analyst 207
Developer scrutinizes code with concern in a well-lit lab setting.

GitHub Dev Attack Exploits OAuth Tokens

A single click can be all it takes for an attacker to swipe a GitHub token, giving them free rein to read and write to your private repos. Security researcher Ammar Askar warns that a clever exploit in GitHub.dev's web-based editor can turn a harmless link into a token-stealing threat.

Analyst 207
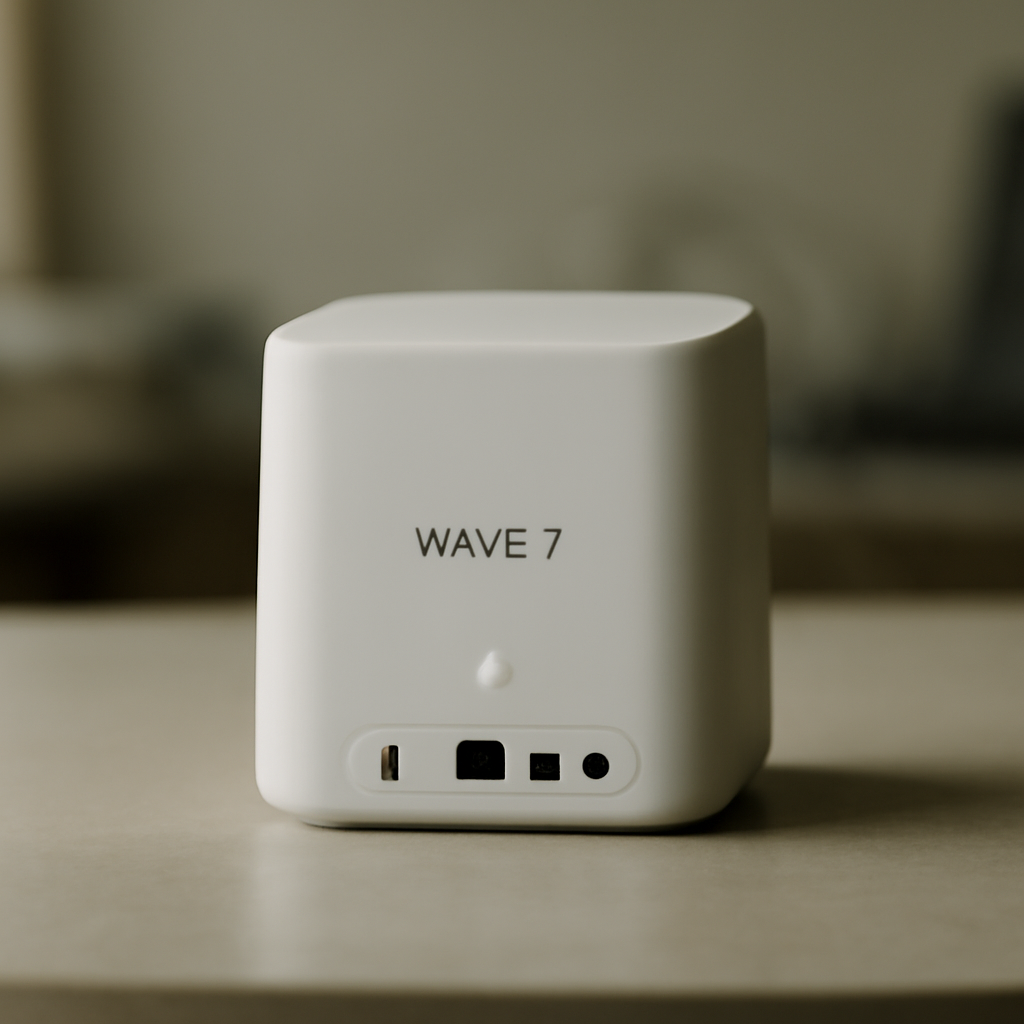
A Wave 7 mesh router centered on a neutral surface with a blurred background.

Acer Rushes to Patch Zero-Days in Wave 7 Routers

Acer is urgently patching a critical vulnerability in its Wave 7 routers that allowed hackers to easily access sensitive login credentials, putting your entire network at risk. This flaw let attackers remotely tap into plaintext passwords stored in log archives, no authentication required.

Analyst 207
Dark web marketplace setup with laptop and papers in dimly lit room.

AI-Powered Cybercrime Tools Flood Dark Web Marketplaces

The dark web has seen a staggering 3,810% surge in AI-powered cybercrime tools, with posts skyrocketing from 38 in December to 1,486 in February, signaling a new wave of threats. This alarming trend has experts like Cynthia Kaiser, SVP of the Ransomware Research Center at Halcyon, warning that cyber threats have become the "national security challenge of our lifetime."

Analyst 207
Crowded gaming center with gamers playing, some showing concern on their faces.

Malware Campaigns Target Gamers, 86K Infected by CountLoader

A shocking 86,000 gamers have fallen victim to CountLoader, a sneaky malware campaign that's been targeting players since January 2026, and the masterminds behind it are making it easy for others to join the malicious party with their free, user-friendly malware service.

Analyst 207
Developer workstation with VS Code on laptop and GitHub page on nearby device.

VS Code Zero-Day Vulnerability Exposes GitHub Tokens to Theft

A security researcher just revealed a shocking VS Code zero-day vulnerability that lets attackers swipe your GitHub authentication tokens with just one click, exposing your online projects to potential theft. This exploit cleverly abuses VS Code's system to run malicious code and extract sensitive tokens.

Analyst 207
Minecraft game setup on a laptop on a cluttered desk with a smartphone and tablet nearby.

WeedHack Malware Targets 116,000 Minecraft Systems Worldwide

Over 116,000 Minecraft systems worldwide have fallen victim to the WeedHack malware campaign since January, with an alarming rate of 2,000 to 3,000 infections daily. This massive operation has spread its reach across the US, Germany, India, and the UK, affecting a staggering number of users.

Analyst 207
A sleek, brightly-lit tech company headquarters with a hint of tension in its modern architecture.

Australia Seeks to Leverage Stability in AI Infrastructure Race

In a concerning escalation, cyberattacks against Israeli targets skyrocketed by 700 percent over just two days following the June 2025 strikes, with Israel accounting for 12.2 percent of all geopolitically motivated cyberattacks worldwide in 2025. This alarming surge highlights the growing threat of cyber warfare in the region.

Analyst 207
Ransomware workspace with Russian map and computer screens in dim light.

Ransomware Operator Flouts Unwritten Rule, Hits Russia

A shocking move by a ransomware operator has sent shockwaves through the cybercrime underworld: they've brazenly targeted Russia, flouting an unwritten rule that's long been observed by hackers. This bold - and some might say, boneheaded - decision has left many in the cybersecurity community scratching their heads.

Analyst 207
Child's bedroom with Minecraft bedspread and gaming setup, laptop screen showing blurred game environment.

WeedHack Malware Infects 116,000 Minecraft Systems Worldwide

A massive malware campaign, dubbed WeedHack, has infected a staggering 116,464 Minecraft systems worldwide since January, with a whopping 2,000 to 3,000 new infections occurring daily. The widespread attack has hit the US, Germany, India, and the UK the hardest.

Analyst 207
Smartphone on a lab surface surrounded by blurred testing tools near a window.

Google Patches Actively Exploited Android Flaw Amid June Update

Google just dropped a crucial security update for Android, fixing 124 vulnerabilities, including a high-severity flaw that's being actively exploited - don't wait, patch up your device now! This critical fix tackles a privilege escalation bug that can be triggered without any user interaction, putting your data at risk.

Analyst 207
Blurred laptop screen and documents on a desk in a typical office setting.

AI-Built Ransomware Toolkit Evades EDR Solutions with Automated Attacks

Sophos researchers uncovered a sophisticated AI-built ransomware toolkit that cleverly evades detection by automated security solutions, triggering alerts only after it had already compromised a customer system. The toolkit's sinister purpose was revealed through investigation, which found references to a ransom note and a list of targeted organizations on a dark web leak site.

Analyst 207
Server equipment on a rack in a brightly-lit government agency setting.

CISA Flags Oracle WebLogic Flaw as Actively Exploited

The US Cybersecurity and Infrastructure Security Agency (CISA) has flagged a high-severity Oracle WebLogic flaw, CVE-2024-21182, as actively exploited, prompting federal agencies to apply fixes by June 4, 2026. This critical vulnerability, rated 7.5 by CVSS, was added to CISA's Known Exploited Vulnerabilities Catalog after evidence of active exploitation was confirmed.

Analyst 207
Cluttered office desk with laptop, router, and papers, softly glowing in a cityscape-lit room.

Gamaredon Exploits WinRAR Flaw to Deliver GammaWorm, GammaSteel Malware

Cyber attackers have cleverly exploited a WinRAR flaw to unleash a potent malware duo, GammaWorm and GammaSteel, with the goal of taking control of infected systems and executing malicious scripts. This sneaky tactic, spotted by French cybersecurity firm Sekoia, allows hackers to fingerprint host systems, manipulate network settings, and fetch additional payloads from command and control servers.

Analyst 207
Dimly lit office workspace with computer displaying email error message.

Microsoft Exchange Online Disrupts Email Services Across North America, Germany

Microsoft Exchange Online is currently experiencing a widespread outage, causing significant delays in sending and receiving emails across North America and Germany, with some messages remaining undelivered for over an hour. The issue was detected at 10:33 a.m. EDT and is being actively investigated by the company.

Analyst 207
Laptop screen shows a browser window with a webpage, set against a blurred office or city background.

Browser Becomes Front Line in AI Security Battle

The battle for AI security is heating up, and the browser has become the front line - with security teams facing a double threat of AI-powered attacks converging in this critical space. Attackers are leveraging AI to supercharge phishing techniques, including device code phishing kits that have surged 18x in just one year.

Analyst 207

Meta AI Exploited to Hijack High-Value Instagram Accounts

A shocking security breach has hit Instagram, where hackers exploited Meta's AI-powered support system to hijack high-value accounts, leaving users helpless and zero humans in the loop to fix the issue. Attackers cleverly tricked Meta's AI into thinking they were the legitimate owners by using an AI-generated video, bypassing automated checks and taking control of rare or valuable accounts.

Analyst 207
Smartphone with chatbot interface on screen, conveying vulnerability.

Hackers Exploit Instagram AI Chatbot to Hijack User Accounts

Hackers recently tricked Instagram's AI chatbot into handing over account controls, highlighting a critical vulnerability in AI agent authorization - a problem that's proving tougher to crack than authentication. By falsifying user locations and manipulating the chatbot, attackers were able to change account email addresses and passwords.

Analyst 207
Dimly lit computer workstation with code on laptop screen, surrounded by computer hardware and security research books.

Microsoft Threatens Security Researcher Over Windows Exploits

A mysterious security researcher known as "Nightmare Eclipse" has unleashed a string of powerful Windows exploits, including one that can bypass BitLocker, leaving Microsoft scrambling to respond. The bold move has sparked a tense standoff between the researcher and the tech giant.

Analyst 207
