[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Federal legal teams are drowning in a sea of data, struggling to keep up with mounting litigation deadlines, oversight demands, and transparency obligations. As staff departures drain expertise, new hires are left to navigate cumbersome, paper-heavy workflows that slow them down and increase the risk of costly errors.

General Motors has been hit with a record $12.75 million penalty for selling California drivers' data without their consent, despite promising to protect their privacy. This landmark case marks a major victory for data protection, with California's Attorney General Rob Bonta leading the charge.

Big changes are coming for Kochava, a data broker that allegedly sold precise location data from hundreds of millions of smartphones without consent - under a proposed FTC settlement, they'll need to get explicit permission from consumers before sharing their sensitive info. This move could mark a major shift in how companies handle location data sales.
The Federal Trade Commission is taking a stand against Kochava, proposing an order that would require the company to obtain explicit consent from Americans before selling their precise location data, and only use it for services they directly requested. This move aims to put an end to the sale of sensitive location information without users' knowledge or consent.
The European Commission's recent findings have revealed that Meta failed to protect minors, with a staggering 12% of European children under 13 reportedly accessing Facebook or Instagram, sparking concerns over online safety. This has led to a push for mandatory online age verification, despite security risks.
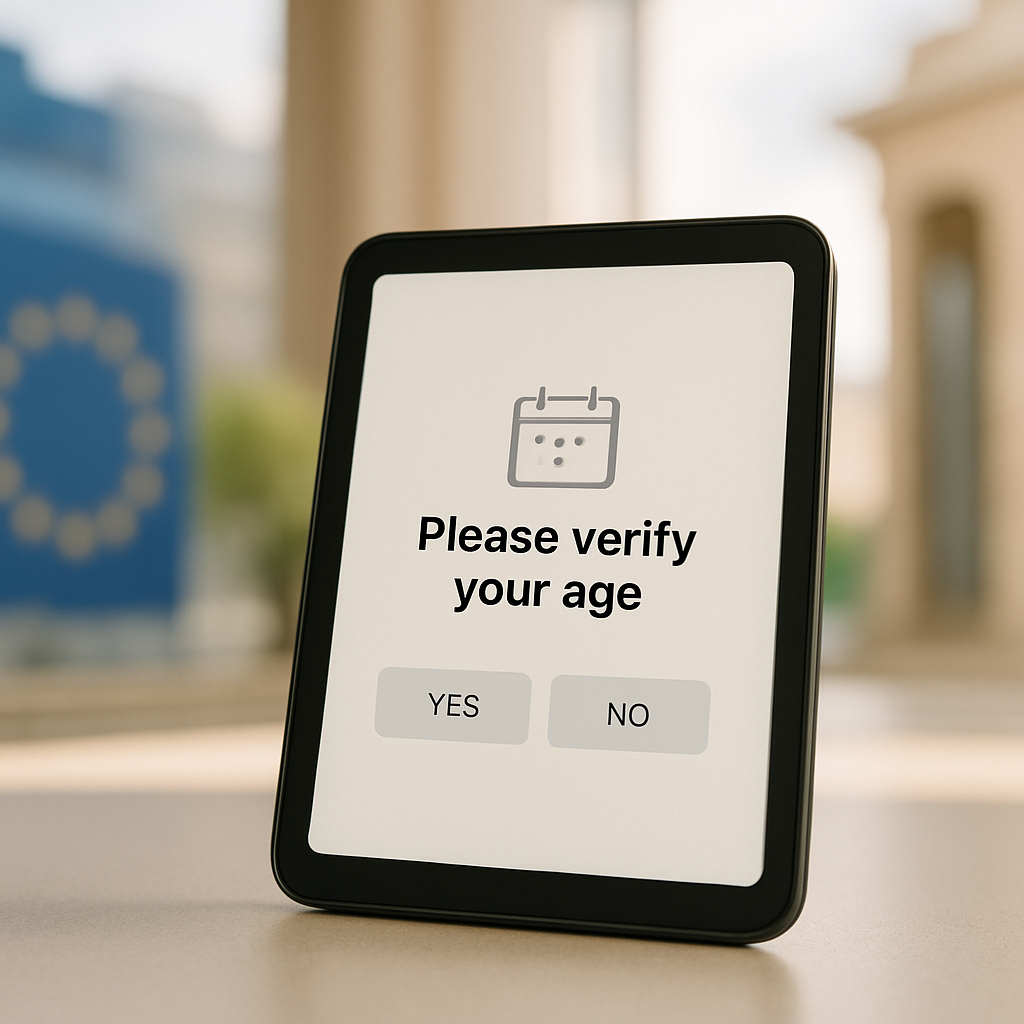
The European Commission is taking a major step to safeguard minors online, recommending that EU member states adopt an open-source age verification tool that's easy for online platforms to implement. This move aims to shield kids from harmful content, building on the Digital Markets Act and Digital Services Act to hold big tech accountable.
US companies are facing a record-breaking $3.45 billion in privacy fines, a staggering amount that surpasses the total fines issued over the past five years combined, as regulators shift from education to full-scale enforcement. This surge in fines is driven by stronger state laws, coordinated interstate efforts, and increased scrutiny of AI and automation practices.
UK's top data watchdog, John Edwards, has temporarily stepped down from his role amid an independent workplace investigation, cooperating fully with the probe. He made the announcement via LinkedIn, confirming his voluntary leave of duties as head of the Information Commissioner's Office.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
The consequences of neglecting HIPAA risk analysis are steep: four entities recently paid a total of $1.7 million in fines for failing to conduct accurate, timely, and thorough assessments, exposing sensitive health information of nearly 427,000 individuals to hacking and ransomware threats.

Germany's government is pushing for a new law that would require internet service providers to store customer connection data for three months to help combat online crimes, sparking concerns about privacy. The proposed mandate, justified as a way to keep the digital space safe from criminals, has been approved by the national cabinet and now awaits parliamentary approval.

House Republicans have introduced the Secure Data Act, a groundbreaking national data privacy bill that puts Americans in control of their personal data and holds companies accountable for keeping it safe. The proposed law would give consumers the power to opt out of data collection for targeted ads, third-party sales, and automated decision-making.
The UK's communications regulator, Ofcom, has launched a crucial investigation into Telegram over concerns that the platform is being used to share child sexual abuse material, sparking a delicate balance between regulation and user protection. This probe also extends to teen chat sites, raising important questions about moderation, oversight, and the safety of young users.

A health AI company is facing a federal lawsuit in Chicago, accused of using and selling millions of people's DNA data without their consent. The plaintiffs claim that genetic information can't be fully anonymized, putting sensitive personal data at risk.

When regulations remain steady, but your identity landscape evolves rapidly, what gives? The real question is, how will your organization adapt to the shifting identity verification landscape while staying compliant with unchanged regulations?

In today's high-risk digital landscape, effective risk management is no longer a choice - it's a necessity for protecting your organization's information systems and sensitive data. By adopting a comprehensive risk management approach, you can ensure the confidentiality, integrity, and availability of your data and stay ahead of evolving cyber threats.

The National Institute of Standards and Technology (NIST) has just unveiled a groundbreaking identity verification standard to safeguard the identities of federal workers and contractors, addressing the growing threat of identity theft and cybersecurity breaches. This critical new standard is a major step forward in protecting sensitive information and preventing unauthorized access.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The Department of Defense has proposed a new rule requiring government contractors to provide critical privacy training to their staff, taking a proactive stance to safeguard sensitive citizen information in an era of escalating cyber threats. This move marks a significant step forward in bolstering security and protecting personal data.

The Information Commissioner's Office has hit Birmingham-based scammers TMAC with a £100,000 fine for making over 4.2 million unwanted calls to UK residents, a move aimed at putting a stop to the nuisance. But will this hefty penalty be enough to deter others from following in their footsteps?

Reddit faces a £14m ICO fine over alleged unlawful processing of children’s information, thrusting age assurance into the spotlight and exposing the uneasy trade‑offs between privacy, safety and practical moderation. With Reddit weighing an appeal, regulators are using enforcement to push platforms toward safer, more privacy‑protective design.
The UK data watchdog just hit Reddit with a £14.47M fine for retaining and using young users data without a clear lawful purpose. Reddit plans to appeal, but the ruling makes plain that public conversation isn’t a get-out-of-jail-free card for sweeping up personal information.

Data discovery isnt just paperwork—its a high-stakes security challenge that can jeopardize careers and public trust. Federal teams must pair legal discovery obligations with tight controls—inventory, classification, and rapid detection—to keep sensitive records safe.

State agencies sit on mountains of untapped data, but fractured systems and privacy concerns keep those insights locked away. This data sharing roadmap shows how the right governance, modern tech, and trained teams can unlock faster services, smarter policy and safer outcomes.

State agencies sit on vast, untapped data that too often remains locked behind silos and legacy systems. This must-have data sharing guide shows how to align governance, technology and people to unlock value for faster services, smarter policy and safer AI use.
State agencies are sitting on mountains of untapped data—and a practical data playbook can turn those silos into faster services, smarter spending, and clearer outcomes across health, transportation, and workforce programs. Learn how centralized platforms, strong governance, and CDO leadership unlock real wins—and what to fix when trust, legal hurdles, and fragmented systems get in the way.