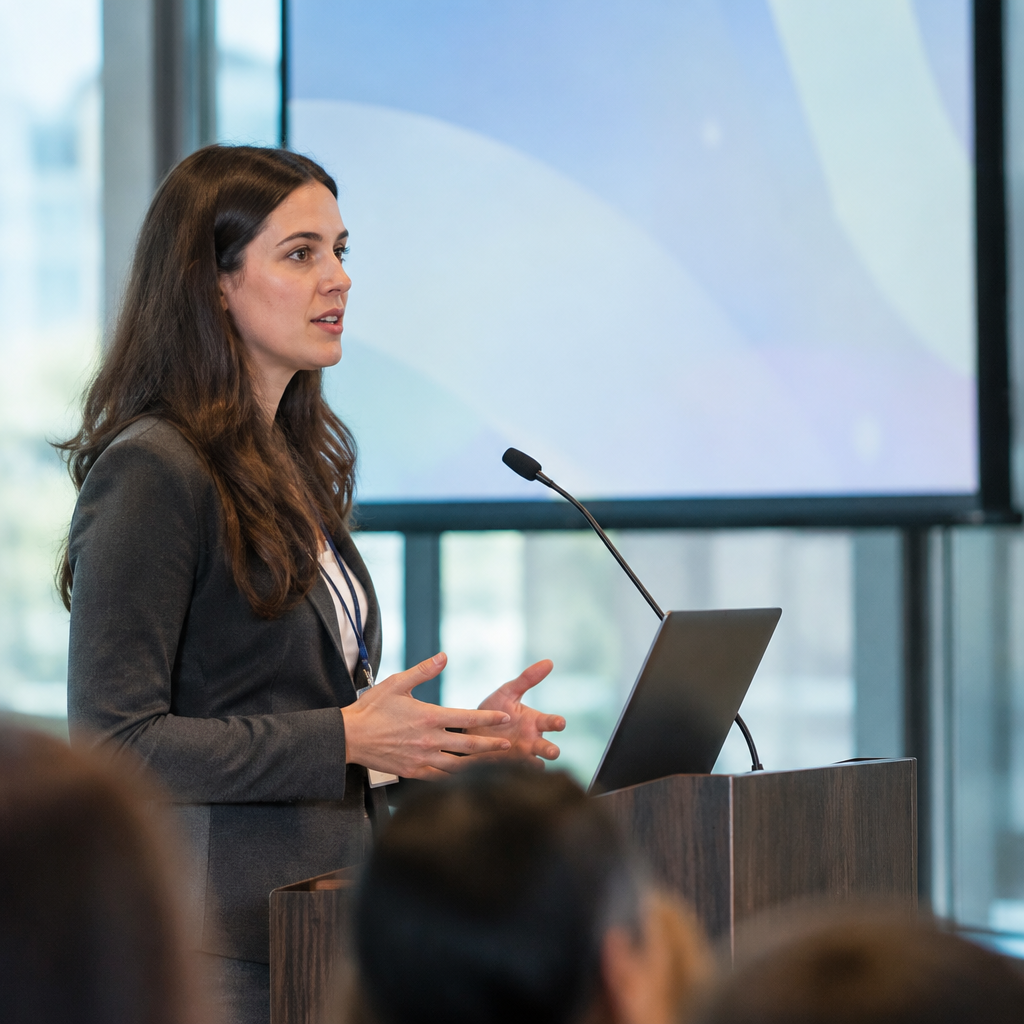
"We’ve all been told since 2023 that AI will make attackers better, faster and stronger…" — Selena Larson at IRISSCON 2026
“We’ve all been told since 2023 that AI will make attackers better, faster and stronger. That they’ll have access to the same tools and resources as the best developers, security professionals and vulnerability researchers in the world, and will automatically become better at hacking. This is marketing nonsense, the data just doesn’t back up this assertion,” Selena Larson, principal threat researcher at Proofpoint, told attendees at IRISSCON 2026 in Dublin, Ireland, on November 11.
Larson’s central claim: while AI has increased the speed and scale of some malicious activity, widespread reliance on AI has introduced new, often glaring errors that reduce the effectiveness of many attacks.
AI “slop” in malware: broken code and mismatched intent
Proofpoint used the term “AI slop” to describe the pattern of mistakes emerging when threat actors lean on automated tools. Larson said researchers “frequently run into malware where the code doesn’t actually work, there’s comments which want to do one thing, but the malware is doing something completely different.”
That mismatch—comments or design intent that do not align with executable behaviour—creates overt failures and more observable noise for defenders. Larson framed AI as a productivity tool that is “only as good as its operator” and warned it can “lead to more sloppy mistakes.”

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildTA4903: AI-driven phishing that reads like a template
Proofpoint tracked a specific example in phishing and business email compromise (BEC) activity: a group identified as TA4903. Historically, Larson said, TA4903 impersonated US government entities with sophisticated lures targeting organizations across a range of sectors.
Since adopting AI tools in their attack chain, Larson reported, the group’s lures have “really gone downhill.” AI-generated emails sometimes do not match subjects or attachments and, in some cases, leave the body of the message blank. Phishing websites produced with AI coding tools tend to be simplistic and share similar colours and formatting—making them easier for targets to spot.
Larson also pointed to an ironic contrast: the use of AI to craft region-specific grammar and spelling can make lures less believable. “Human beings often don’t know how to spell, they often are bad at grammar, people aren’t trying to be overly polished. So, I think that’s actually a bit of a detriment to some of these actors,” she said.
BlueMoon (August 2026): LLM-written exploits that generate noise
Larson described another domain where AI has produced mixed results: vulnerability exploitation. She cited the exploit chain known as “BlueMoon,” first observed in August 2026, which chained together three Microsoft Chrome browser vulnerabilities.
Threat actors used large language models (LLMs) to write exploits using information in patch release notes, but the resulting exploit “was highly flawed, often not behaving as intended and generating significant noise,” Larson said. That noise made attempts readily identifiable by defenders, undermining the stealth required for successful exploitation.
How technologists, policymakers, and enterprises should respond
- Technologists and security teams: Larson’s message for defenders is practical: “Attacks are attacks and AI generally doesn’t really matter. Whatever you’re defending against, defense is going to remain the same.” Teams should continue prioritizing established defensive measures while paying attention to faster, higher-volume attempts to exploit long‑known vulnerabilities.
- Policymakers and regulators: The central shift Larson identified is speed—AI can make it faster and easier for attackers to exploit vulnerabilities cybersecurity professionals have been aware of for a long time. Regulators tracking risk should note that increased exploitation cadence, rather than new attack paradigms, is the primary change described.
- Affected enterprises and procurement leaders: Organizations that face BEC and phishing—TA4903’s historical targets include a range of sectors—should watch for low-effort, templated phishing messages and simplistic, similarly styled phishing sites. Those signs, Larson argued, may indicate AI-assisted but less sophisticated campaigns that remain dangerous chiefly because of volume and speed.
Larson’s central thesis is blunt and consequential for defenders: AI has not, by itself, raised the bar for threat sophistication. It has enabled faster, larger campaigns and introduced new failure modes—faulty malware, mismatched phishing lures, and noisy, LLM‑crafted exploits like BlueMoon—that can make attacks easier to detect. “AI is only as good as its operator,” she said, and “it can lead to more sloppy mistakes.”
Her final admonition at IRISSCON 2026 was a reminder to practitioners that the fundamentals of defense remain the same: patch known vulnerabilities, scrutinize email and web lures, and treat increases in attack tempo as the central operational risk posed by AI-assisted adversaries. “Attacks are attacks and AI generally doesn’t really matter. Whatever you’re defending against, defense is going to remain the same,” Larson concluded.