[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
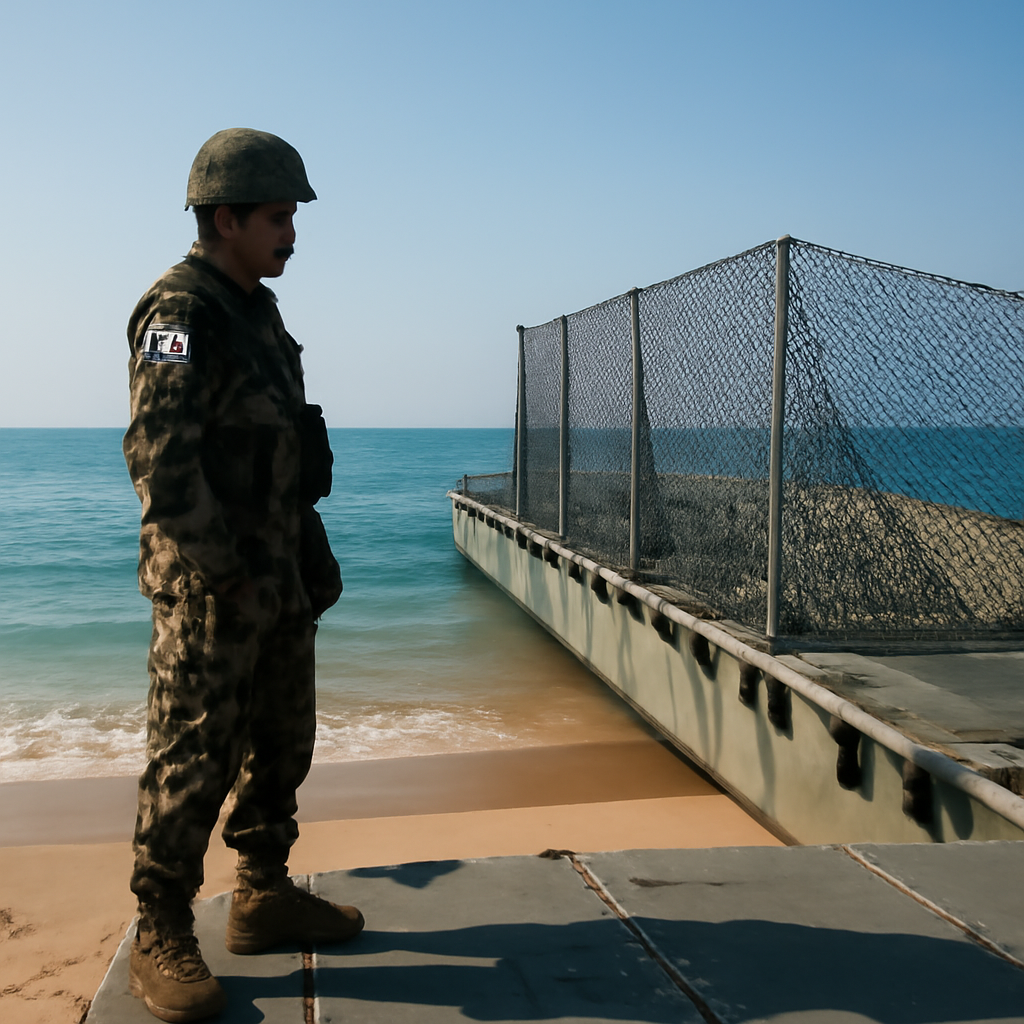
South Korea is stepping up its defense game by deploying anti-drone netting in a recent logistics exercise, showcasing its commitment to protecting its operations from aerial threats. Check out the photos from the Combined Joint Logistics Over-the-Shore 26 exercise, where Republic of Korea service members used the innovative netting on a floating causeway.
Home Affairs Minister Tony Burke is standing firm on Australia's terrorism laws, rejecting a proposal to drop the religious motivation test, and instead choosing to maintain the current definition. This decision comes amid a push for an ideology-agnostic framework that focuses solely on harm.
Ukrainian President Volodymyr Zelenskyy has ousted Defense Minister Mikhailo Fedorov, citing the minister's unauthorized procurement decisions, a move that has sparked protests and concern among allies. The sudden dismissal follows a public feud with Gen. Oleksandr Syrskyi, commander-in-chief of the armed forces.
The Federal Rotational Cyber Workforce program, launched in 2022, has seen a surprisingly low uptake, with only eight participants out of 634 applicants, despite 13 agencies offering 106 positions. This falls short of its goal to develop a more versatile and agile cyber workforce.
As AI continues to evolve, it's crucial to treat AI-driven threats as a top priority, using the technology to supercharge their attacks and compress timelines. AI is being used by attackers to automate routine work, streamline reconnaissance, and shorten development cycles, turning what once took days into operations that can be executed in just hours.
South Korea is racing to develop its own AI model for bug detection by 2026, driven by concerns that relying on foreign models could leave the country vulnerable at critical moments. The homegrown AI model aims to rival leading security-focused models, ensuring the nation has control over its bug-finding capabilities.
Beware of the GPT-5.6 model's alarming bug that can wipe out your files in an instant, as shocking incidents from tech investor Matt Shumer and software engineer Bruno Lemos reveal. Users are reporting devastating file deletions, with one victim losing almost all of their Mac's files and another having their entire production database erased.
Beware: a sneaky new malware called ClickLock has already compromised over 100 macOS systems in 33 countries, tricking users into revealing their login passwords. This stealthy threat has been hiding in plain sight since May, leaving a trail of vulnerable systems in its wake.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A ransomware attack has hit Fairlife, a US dairy production subsidiary of Coca-Cola, disrupting operations and prompting an immediate response from the company. The incident has triggered a thorough investigation, with outside experts and law enforcement working to contain the breach.
A cybersecurity expert recently discovered that AI models can be easily manipulated to behave maliciously, with a backdoor installable in just an hour for under $100. This startling vulnerability was uncovered through a simple fine-tuning test that quickly escalated into a full-blown security threat.
A security researcher discovered a vulnerability in Anthropic's Claude browser extension that allows malicious Chrome extensions to trick it into performing predefined AI actions on connected services like Gmail and Google Docs. This flaw could have serious consequences, as it only requires a simple simulated click to launch built-in workflows.
Beware of OkoBot malware, a sneaky threat that's using clever tactics like fake GitHub repositories and ClickFix attacks to steal your cryptocurrency wallet secrets and sensitive data. This malicious framework is armed with over 20 payloads, making it a formidable foe in the world of cybercrime.
Two young hackers, Owen Flowers and Thalha Jubair, have been sentenced to 5.5 years in prison for their reckless cyber attacks, including a £29 million hack of Transport for London, with prosecutors highlighting the disturbing extent of their disregard for human life. The pair's guilty plea marks a landmark case, believed to be the first convictions under the Computer Misuse Act 1990's most serious offence.
Raytheon is seizing the spotlight at the Farnborough International Airshow, showcasing its battle-tested Coyote counter-UAS system, which has seen action in multiple theaters of operation. The company is leveraging real-world results to drive sales, with executive Joseph DeAntona touting the system's proven performance.
In late 2025, a new wave of malicious activity emerged, led by the evolved GoSerpent malware, which has been quietly lurking in the shadows since at least 2021. This stealthy backdoor has upgraded its data exfiltration tactics, putting organizations on high alert.
Kaspersky uncovered a sneaky APT campaign, HelloNet, that exploited the ViPNet Update System to spread malware, starting as far back as May 2026. The attackers cleverly used a malicious library to hijack the ViPNet updater, allowing them to siphon off sensitive info and clean up their tracks.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A potential deal for Pakistan to acquire 40 advanced J-35 fighter jets from China has been rumored since 2024, but remains unconfirmed - if finalized, it could drastically shift the balance of power on the Indian subcontinent. The sale would mark a significant boost for Pakistan's military, but China is reportedly exercising caution to avoid giving Islamabad too great an advantage.
Government agencies and military organizations risk exposing themselves to hidden security threats if they don't adopt a zero-trust approach to their private 5G networks, leaving them vulnerable to potentially devastating attacks. Without proper security measures in place, adversaries could gain unrestricted access to sensitive information and wreak havoc.
As AI continues to shape our world, a crucial question emerges: will our privacy protections rely on individuals controlling their data or on companies being held accountable for how they collect and use it? By shifting the focus from personal control to corporate responsibility, we can create a more effective and fair approach to safeguarding our personal information.
Beware of a sneaky new macOS malware that tricks you into stealing your own sensitive data - all it needs is for you to paste a single command into Terminal. Dubbed ClickLock Stealer, this clever con artist has already duped at least 100 victims across 33 countries.
Beware of malware hiding in plain sight: recent cases show how trusted tools and services like Chrome's sync feature can be repurposed as surveillance and infection vectors, leading to full compromise. Malicious packages, like 11 fake NuGet game utilities, can sneak in undetected, downloading second-stage payloads and wreaking havoc.
Beware of a sneaky phishing campaign that's using cleverly disguised font files to deploy a powerful Lua Loader - a stark reminder that security controls can't always trust a file's extension. A recent Fortinet analysis reveals the tactics used by attackers to hide malicious JavaScript payloads in seemingly harmless archives.
A security flaw in n8n's workflow automation platform allowed unauthorized users to log in to accounts due to a token exchange mishap, essentially handing out the wrong accounts at login. This vulnerability stemmed from a misimplementation of the Enterprise token exchange feature.
New York Attorney General Letitia James slammed 23andMe for its lax security, saying the company's failure to protect customer data put millions at risk. The criticism comes as part of a settlement that hits 23andMe with an $18 million penalty for its role in a massive data breach.