[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
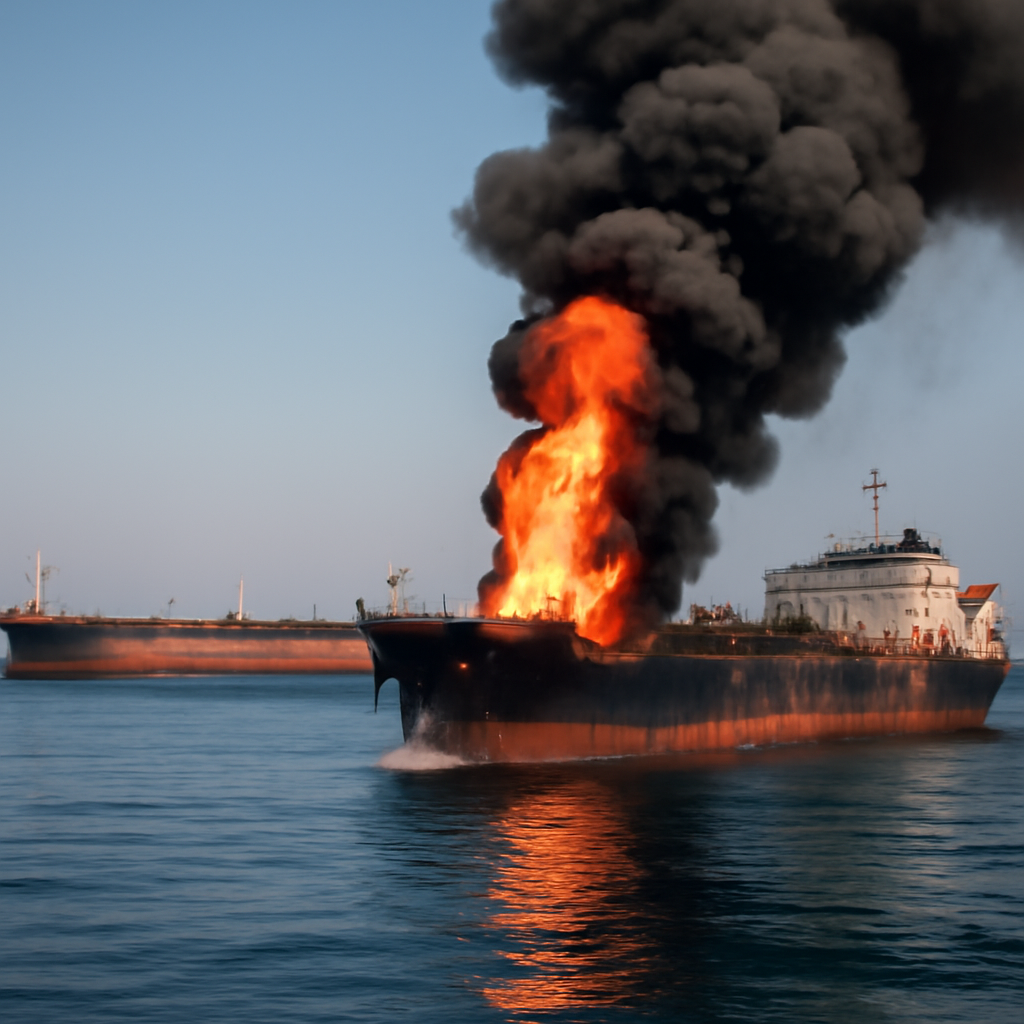
The Houthis have launched a daring attack on two Saudi oil tankers in the Red Sea, striking them with a combination of ballistic missiles, cruise missiles, and drones, and sparking a massive fire on both vessels. The bold move has reportedly forced nearby ships to retreat, with one tanker confirming it was hit by an unknown projectile off the coast of Saudi Arabia.
The UK's defense industry is poised for growth, with government and business leaders uniting to tackle cultural barriers and unlock private investment, sparking optimism for a collaborative solution. By drawing inspiration from the US experience, the UK can learn to move quickly and persist through challenges, while staying true to its unique strengths.
Lockheed Martin Ventures is set to make a significant splash in Europe's defense tech scene with a $100 million investment, aiming to tap into the region's thriving innovation landscape. The move follows a surge in promising deals, and marks the largest boost in the venture fund's 19-year history.
Defense Secretary Pete Hegseth faced intense scrutiny from senators over his claims about the US war on Iran, struggling to provide clear answers about the strategy and impact of the conflict. Hegseth made assertions about the devastating effects of US strikes on Iran's military and infrastructure, but also made partial admissions about Tehran's ongoing capabilities.
The Oregon Air National Guard's 142nd Wing just took a major leap forward with its F-15EX Eagle II, successfully completing its first-ever air-to-ground bombing training missions at Mountain Home Air Force Base in Idaho. Over 10 flawless missions, the crew dropped 36 inert training bombs with perfect scores and zero safety incidents.
The Government Accountability Office has uncovered a staggering truth: nearly 7 in 10 federal cybersecurity reporting rules are duplicated, with 80 out of 117 rules at 37 agencies requiring redundant written reports. This revelation raises critical questions about the efficiency and effectiveness of current federal cybersecurity regulations.
The Farnborough International Airshow 2026 in the UK has wrapped up after an action-packed few days of thrilling displays and cutting-edge demonstrations. For those who missed it, a sneak peek at the event's favorite images is now available.
Imagine having an invisible backdoor to your most sensitive information - that's what happened when China-backed hackers infiltrated private 5G networks, leaving no limits to what they could access or manipulate. Government agencies and cybersecurity experts warn that these threats, known as Salt Typhoon and Volt Typhoon, have been targeting US networks for years.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The US Army is reviving its Patriot missile buys, with Raytheon securing a major deal worth $441.6 million, marking the first domestic GEM-T production order in over 30 years. This move comes as the Army faces stockpile strains, highlighting the ongoing demand for these critical defense systems.
Greece is set to supercharge its air defenses with a groundbreaking $3.4 billion initiative, dubbed Achilles' Shield, which will weave a comprehensive network of overlapping defense systems across the country. Spearheaded by Defense Minister Nikos Dendias, this ambitious project promises to revolutionize Greece's defense capabilities.
The Cybersecurity and Infrastructure Security Agency (CISA) has unveiled a game-changing collaboration framework, ANCHOR-CI, to revolutionize how the federal government and private partners work together to protect critical infrastructure. This fresh approach replaces the two-decade-old CIPAC model, promising a more effective and resilient cybersecurity partnership.
Two federal employee unions are taking a stand against the Pentagon's sudden move to scrap collective bargaining agreements, asking a judge to restore their rights and hold the Department of Defense accountable to a fair process. The American Federation of Government Employees and the National Federation of Federal Employees argue that Secretary Pete Hegseth's April decision was made without justification or transparency.
Russian hackers have launched a global espionage campaign, exploiting a vulnerability in Zimbra Webmail since July 2025, with a sneaky zero-click phishing attack that tricks victims into handing over sensitive info. The clever tactic uses fake news headlines and hidden code to inject malware into browsers, all without requiring a single click.
Malvertising on Bing Ads led to a massive attack, compromising at least 29 organizations in just two days with SectopRAT malware via a fake Claude app installer. A malicious artifact on Claude's own domain was downloaded over 7,100 times before being taken down.
A single, stealthy view is all it takes for hackers to exploit a Zimbra flaw, allowing them to siphon off 90 days' worth of emails, passwords, and sensitive data. This alarming vulnerability, tracked as CVE-2025-66376, has prompted a joint warning from US and international cybersecurity officials.
The Solomon Islands' prime minister hit the nail on the head, saying "This is not something a friend does," as over a dozen Indo-Pacific governments, including Pacific island nations, united to condemn China's recent ballistic missile test launch. The test, which Beijing downplayed as "routine," sparked alarm across the region, with leaders like Australia's prime minister warning it undermined stability.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
The Pentagon is calling on industry partners to collaborate on a critical mineral supply chain overhaul, with a focus on friendshoring, domestic shoring, and supplier changes to reduce reliance on high-risk foreign sources. By presenting credible plans, contractors may be able to negotiate flexible timelines with the Pentagon, ahead of the 2027 deadline set by a new executive order.
The Selective Service System is gearing up to evaluate its emergency response capabilities and is seeking simulation software to help assess its staffing and resource needs. Vendors have until August 14 to submit proposals for the project, with questions due by July 28.
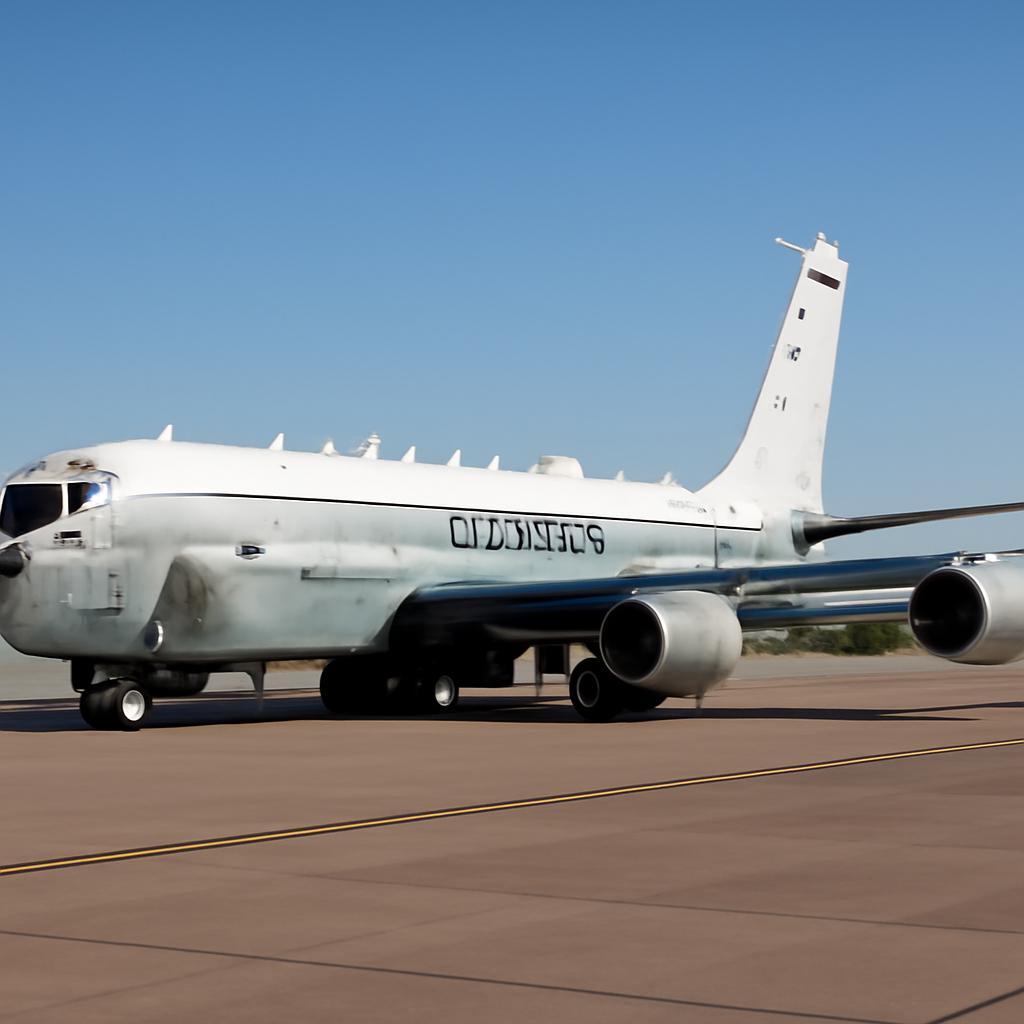
Iran has issued a stark warning to a UK air base, threatening it as a legitimate target if used to launch attacks on Iranian territory, after US bombers took off from the base to carry out strikes. The base, RAF Fairford in England, has also recently welcomed electronic warfare aircraft, heightening tensions.
As public agencies move advanced AI from pilots to mission-critical operations, they face a major hurdle: a data trust gap that's holding back widespread adoption. The root of the problem lies in the disconnect between the data architectures of today and the requirements of trustworthy AI.
A single click on a malicious email could be all it takes for hackers to gain access to your mailbox, thanks to a highly exploitable zero-day vulnerability in Zimbra's software. Dubbed CVE-2025-66376, this flaw allows attackers to execute JavaScript code and inherit user mailbox access simply by viewing a crafted HTML email.
Imagine a thief unlocking your car doors with just a Bluetooth connection - no smashed windows or broken locks required. Researchers have discovered a security flaw in certain dealer-installed systems that puts 2.2 million vehicles at risk of remote hijacking.
This week's ThreatsDay bulletin revealed a disturbing trend: hackers are disguising malware as ordinary tools and features, using familiar names and routine functions to infiltrate code repositories, desktop systems, mobile apps, and more. Even trusted platforms like GitHub and PyPI are being exploited, with GitHub announcing a security update to block vulnerable support bundle uploads.
Kremlin hackers, also known as Laundry Bear, have been exploiting a vulnerability in the Zimbra Collaboration Suite to secretly infiltrate government and commercial networks for over a year, aiming to gather sensitive information for the Russian Federation. They've been using malicious emails to inject JavaScript code, allowing them to covertly acquire email data.